
Professional Shitposter
Joined June 2013
- Tweets60
- Following12
- Followers275K
- Likes10.8K
Marcus Hutchins retweeted
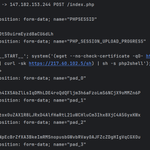
I want to caveat this since based on some comments, people are interpreting it in a way other than was intended. You 10000% need to update your PHP version. php2shell is no joke.
I am NOT saying people don't have functional exploits...they do. I'm saying that most of the public ones are AI hallucinations, and there's also some complexities which lower the risk of something apocalyptic, like a self-propagating worm that blasts through the entire internet (À la. EnternalBlue or Log4J).
The chances are if you used some click-to-deploy container, installed your web stack from a tutorial, or copy and pasted a command from somewhere, you're probably running the same exact config as a gazillion other people. There is no guarantee someone won't publicly release an exploit that affects you setup, or multiple major setups. There is no way for you to know ahead of time.
Additionally, if you're running mod_php, that appears to be the easiest target of all. php-fpm and other configs are not immune, I've seen working exploits for all. But mod_php is the easiest, so I'd recommend not only updating PHP, but planning to migrate to something newer, like PHP-FPM.
I would bet good money this is not the last of the critical PHP bugs we're going to see, and the next ones could be easier to exploit. In which case you get less time to update.
Updating your PHP version is the absoloute bare minimum you NEED to do. Harden your servers, install security monitoring/detection tools, and please, please, migrate off mod_php if you can, it's obsolete af.
Marcus Hutchins retweeted
@MalwareTechBlog @SwiftOnSecurity not just local files either. Definitely been called for IR after cryptolocker hit their network shares.