

Updates & announcements related to Meta Bug Bounty program. If you have found a security vulnerability, we encourage you to let us know ⬇️
Joined March 2023
- Tweets57
- Following1
- Followers5.9K
- Likes62





Pinned Tweet
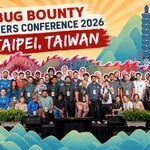
🎬 The MBBRC 2026 recap video is live!
Watch highlights from four days in Taipei with top security researchers from around the world.
📺 youtu.be/OtMhDdnrvZA
#MetaBugBounty #MBBRC2026 #BugBounty #Taipei

Meta Bug Bounty retweeted

We've now paid out more than $1M in @muse bug bounties. That includes $300,000 to a security researcher who found the most critical bug we've seen in Muse. muse.ai/blog/securing-muse

Meta Bug Bounty retweeted
We’re thrilled to welcome @metabugbounty as a Silver Sponsor of OffensiveCon Tokyo! 🎉
Huge thanks for supporting us!— see you in Tokyo.
#OffensiveConTokyo2026 #OffensiveCon #Meta #MetaBugBounty #BugBounty

Meta Bug Bounty retweeted

Excited to have @metabugbounty as a part of this year’s in person #nahamcon2026 and Prompt2Pwn live hacking event! 🙏🏼

Meta Bug Bounty retweeted

Just dropped a write-up on using Muse Code for Security Research with the folks at @metabugbounty and my good friend @phwd_ and @1_am_nek0 !
Particularly happy with the binary research section using @full_duplex's lldb-mcp with @clearbluejar's pyghidra-mcp 🔥🔥
bugbounty.meta.com/en-gb/lea…

Zurp is now open source. 🧰
Meta Bug Bounty's research toolkit, inside the proxy you already have open. Meta context, CSRF token handling and FBDL access. Every capability is available to your AI agents too.
github.com/facebookincubator…

Why we built it: the context that makes a Meta request make sense — what an opaque ID refers to, which GraphQL operation actually runs — isn't visible from outside. So we brought our tooling to where you already work.
bugbounty.meta.com/blog/zurp…

Want to see it in practice? Our new guide wires Burp, Zurp, Ghidra and LLDB into Muse Code as MCP servers, then points them at targets that really do have bugs.
bugbounty.meta.com/learn/art…
#BugBounty #MetaSecurity

🛠️ TLS 1.3 causing issues with mobile app interception? This guide can help.
Learn how to use BurpSuite to intercept Meta mobile app traffic.
Read more 👉 bugbounty.meta.com/en-gb/blo…
#BugBounty #MetaSecurity #MobileSecurity #InfoSec
🚀 FBDL just went agentic!
We released an open-source MCP server for Facebook Bug Description Language — Meta's tool for building security test environments programmatically.
Tell your AI agent: "I need two users who are friends, one owns a page, the other comments on a post and gets blocked" and it builds everything for you.
No browser, no manual FBDL.
This started as a community project by researcher Ads Dawson at our 2026 Meta Bug Bounty Researcher Conference. We collaborated to extend it with API integration and full run lifecycle support.
Open source. Built with researchers, for researchers.
🔗 bugbounty.meta.com/blog/fbdl…
#BugBounty #SecurityResearch #AI #MCP #Meta #MBBRC26

MBBRC has ended! 🎉
Thank you to every researcher who joined us. The submission window is still open — submit your reports by May 29.
Results will be announced after the deadline. Stay tuned.
#BugBounty #MetaSecurity #MBBRC

Meta Bug Bounty retweeted

Right now I’m in 3rd place 🥹 I’m super happy! I still can’t believe it.
@metabugbounty
#meta #bugbounty #taiwan #argentina #hacking


Meta Bug Bounty retweeted

🇳🇵 From Nepal to the World 🌍
Excited to be in Taipei, Taiwan 🇹🇼 for Meta Bug Bounty Researchers Conference 2026 alongside 82 top security researchers from 25 countries.
Proud to represent Nepal on the global stage 🇳🇵
#meta #bugbounty #mbbrc2026 #bountycon #cybersecurity

Meta Bug Bounty retweeted

Just got back from the Meta Bug Bounty Researcher Conference in Taiwan 🇹🇼
Spent the week hacking @Meta AI and submitted 24 vulnerability reports
The best part wasn’t the bugs, it was collaborating with some seriously talented hackers and close friends: Ads Dawson, @Ph1R3574R73r, Edward Morris, and @wunderwuzzi23 from BT6.
Huge thanks to the @metabugbounty team for hosting an incredible event and creating space for researchers to push on real AI security issues.
AI security is moving fast. Prompt injection, agent abuse, data exfiltration, unsafe tool use, the attack surface is real, and we’re just getting started.


🔒 One week to go! Meta Bug Bounty Researchers Conference 2026 is heading to Taipei, Taiwan 🇹🇼
82 top security researchers from 25 countries. Live hacking. Real impact.
May 6–9 → bugbounty.meta.com/events/
#BugBounty #MetaSecurity #MBBRC2026

We’re teaming up with @PortSwigger to support the security community and help researchers find and report real-world issues faster.
Learn more about the Meta Bug Bounty x PortSwigger collaboration: bugbounty.meta.com/blog/meta…

Excited to announce that Manus is now in scope for the Meta Bug Bounty program. 🎯
Check the Manus scope here: bugbounty.meta.com/en-gb/sco…
Thanks for all your contributions — looking forward to your findings and submissions!