just a dev building small tools on the internet. AI × dev tools × shipping in public. made Pin Check, a free GitHub Actions pin checker.
Joined July 2026
- Tweets393
- Following284
- Followers46
- Likes139




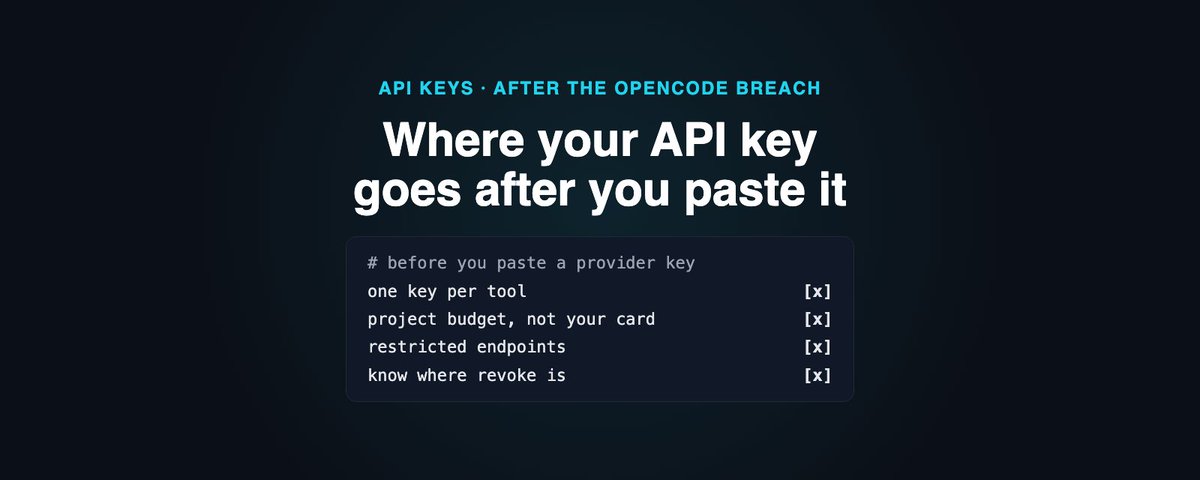
opencode's breach last week exposed provider keys that users had pasted into its web console. the CLI keeps keys on your machine and wasn't touched.
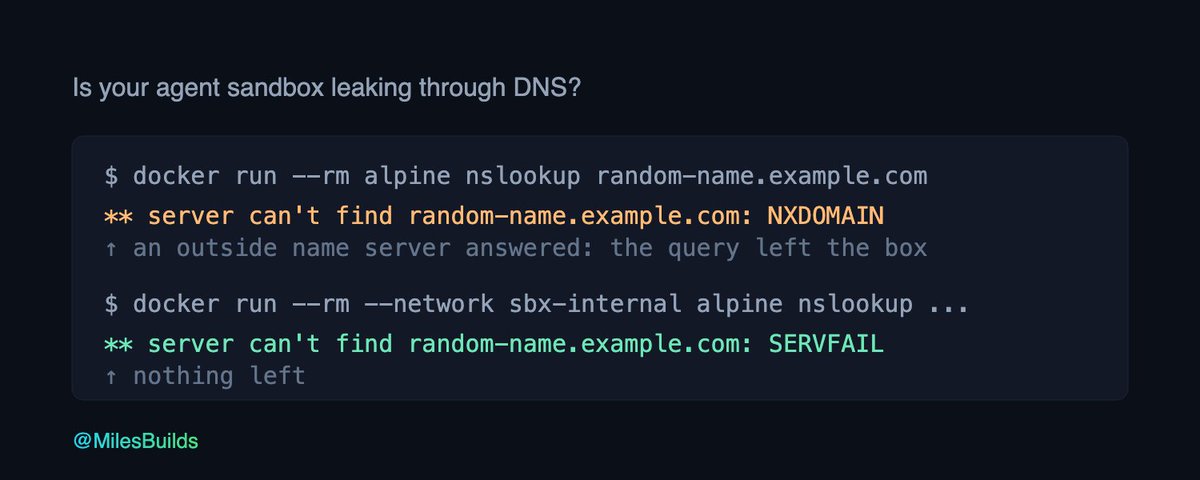
where a pasted key ends up, and four settings that cap the damage when one leaks:
GitHub Actions has a lockfile now. I ran it on a test repo, then tampered with it.
It pins the actions inside composite actions, which a SHA pin in your YAML never reaches. v0.1.6 missed my edited lockfile. v0.2.0 catches it.

GitHub turns off pull_request_target in public repos on November 2.
I pulled every workflow file from the 200 most-starred repos. 76 use it, mostly for labels and comments. The Policy insights page in your repo settings shows what would break.

Your GitHub Actions can leak secrets before anyone reviews a PR. Five lines in a workflow file, three of them behind real attacks (tj-actions, Ultralytics), and the fix for each. GitHub starts enforcing a new pull_request_target default on Nov 2.

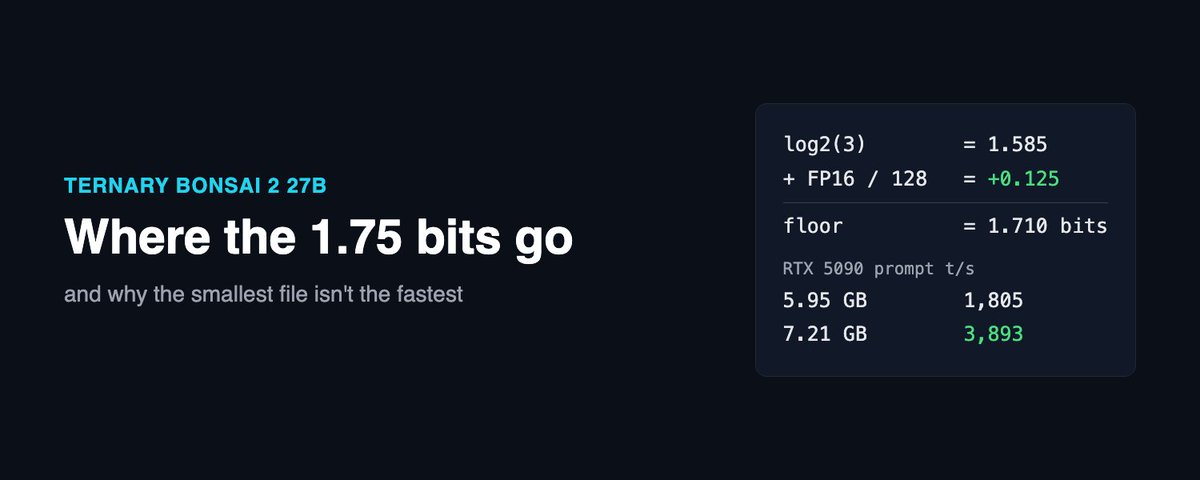
PrismML's ternary Qwen3.8 27B comes as two files. On an RTX 5090, the 7.21 GB one processes prompts over 2x faster than the 5.95 GB one.
For agent work I'd take the bigger file. I wrote up the math on where the 1.75 bits go.