

Noise2Signal Podcast : host @MehulRevankar interviews founders, engineers, and leaders who built the industry on all things Cyber and AI.
Atlanta, GA
Joined April 2026
- Tweets40
- Following105
- Followers130
- Likes2



Business Is a Series Of Hacks teapawt.net/i/broadcasts/1PJqrNbPN…

19
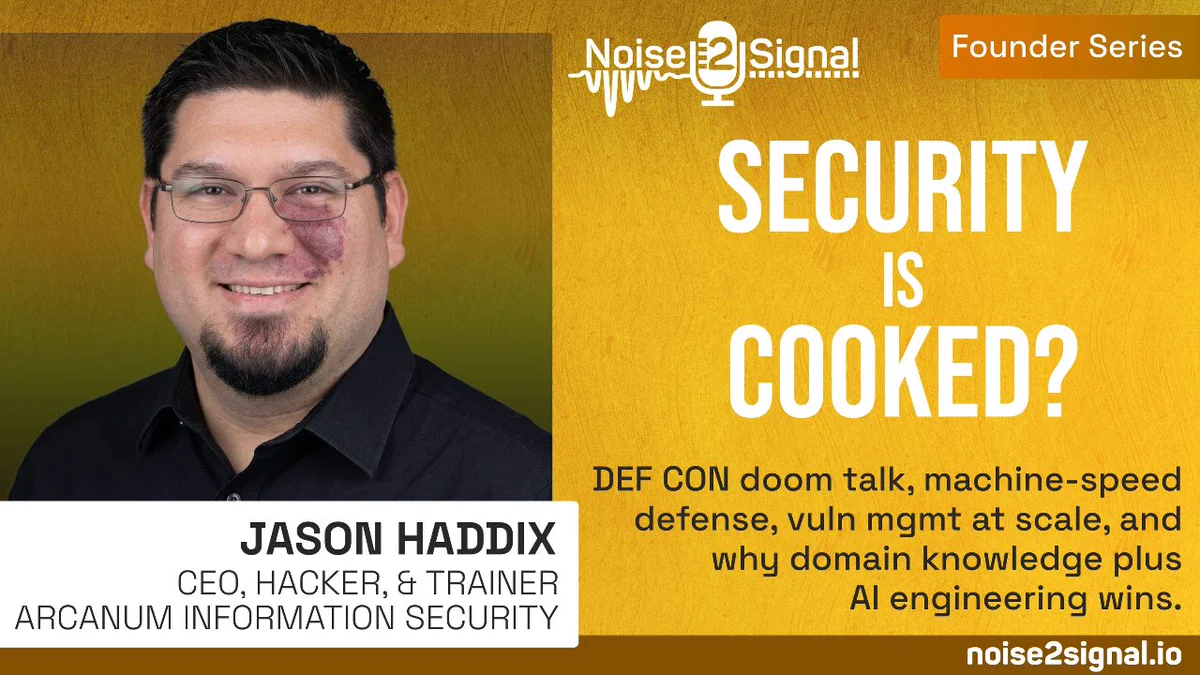
Defcon is Dead, Security is Cooked? teapawt.net/i/broadcasts/1yxBePolZ…
16
Seven Samurai's of VulnOps and Dead Men Walking teapawt.net/i/broadcasts/1DGLdZkwD…

21
The economics of Cyber Offense & Defense teapawt.net/i/broadcasts/1DGleVmMV…

1
25
The CISO before the CISO's w/ Scott Crawford teapawt.net/i/broadcasts/1pKkOXqrg…

12
0 to 1 on EPSS w/ Jay Jacobs teapawt.net/i/broadcasts/1yxBePlRv…

The Accidental Entrepreneur w/ Alan Shimel teapawt.net/i/broadcasts/1jxXgBmVb…

46
Noise2Signal retweeted

Our CEO and Co-Founder Dr. @ayampolskiy sat down with Mehul Revankar on the Noise2Signal @Noise2SignalPod Podcast to talk about going from CISO to founder, and what it actually took to build the security ratings category before the market knew it existed.
They also get into how AI-native attackers are making offense cheaper and faster, and why defenders increasingly need automated systems of their own to keep pace.
👉 Learn more about Alex's journey here: youtube.com/watch?v=zRHsOIv4…
#security #CISO #AI #leadership #cybersecurity #podcast

The Don of Security Ratings Mafia w/ Aleksandr Yampolskiy teapawt.net/i/broadcasts/1pKkOXrEm…

1
33
Noise2Signal retweeted

I am pleased to welcome @alexcpsec to @Noise2SignalPod .
Every year, the @Verizon Data Breach Investigations Report (DBIR) comes out (19 years and counting), and every year, I wait patiently to read it. The thing that strikes me the most about the DBIR report is that it takes a dry, dreadful topic such as data breaches and transforms it into fun, entertaining enjoyable read. Every single time.
So I wanted to get behind the scenes, and talk to the authors on how they create the report.
I asked Alex Pinto, one of the primary authors, to come on the pod to discuss the report. I’ve always had so many questions about the DBIR. I wanted to know: Who actually writes those jokes 😉 ? What do the authors really think about long-term trends?
This interview tries to answer all of that and more.
Here are few highlights:
- An in-depth, behind-the-scenes look at how the report is made
- Who writes the jokes in the DBIR?
- Why ransomware is the "yoga pants" of cybersecurity
- Top trends of 2026
- Why vulnerability exploitation became the #1 vector for compromise
- What launch day is actually like for the DBIR team
Full Episode : noise2signal.io/episode/14/
Looking forward to contributing Quantro Security AI CVE exploitability data to DBIR next year.
#DBIR

Preview : Inside the @Verizon DBIR with @alexcpsec
Tune in on Aug 11th, 10 AM ET.
Vulnerability Research is Not Cooked w/ Thomas Dullien (Halvar Flake) teapawt.net/i/broadcasts/1lKQRRMjB…

2
587
I am excited to welcome Thomas Dullien @Noise2SignalPod to the Noise2Signal podcast!
This episode's title was inspired by Thomas Ptacek’s excellent write-up, "Vulnerability Research is Cooked," which is equal parts inspiring and depressing. Inspiring because finding vulnerabilities in codebases has become so accessible; depressing because we risk losing a generation of experts skilled in the fine art of reverse engineering, which, as Thomas notes, is fundamentally an exercise in endurance.
Fortunately, Thomas Dullien brings a much more uplifting perspective on the future of cyber offense and defense with AI. His take: a human equipped with a tool will continue to outperform the tool alone for the foreseeable future.
Having spent the early part of my career in vulnerability research before founding @QuantroSecurity, I’ve long looked up to pioneers like Halvar and HD Moore (from Season 1). It was fascinating to dive into how they came up through the cracking and hacking scene of late 90's and early 2000's.
A few episode highlights:
- How Thomas Dullien became Halvar Flake.
- The 90s cracking and hacking scenes.
- The origins of BinDiff (and the crazy stories of shadowy figures trying to buy it)
- Google’s acquisition of BinDiff and the comedy of errors that followed.
- Founding Optimyze
- How AI will reshape the future of cyber offense and defense
Listen to the full episode here noise2signal.io/episode/13/
Thomas joins @OpenAI next week to "better cyber". Wish him luck. 🙌 🙏
Noise2Signal retweeted
New Season Premiere. Vulnerability Research is Not Cooked with @halvarflake on @Noise2SignalPod

Noise2Signal retweeted
Excited to welcome @halvarflake on @Noise2SignalPod.
The interview drops tomorrow.
noise2signal.io/#upcoming
