
Fighting/Tracking/Reporting on-chain scams in my free time.
Joined September 2022
- Tweets188
- Following240
- Followers295
- Likes687




Pinned Tweet
Here's how the funds moved cross chain from SOL to ETH-@DriftProtocol hack
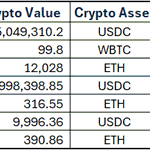
-~$268M was bridged from Solana to Ethereum in ~7 hours.
-At least 6 bridges were used (excluding gas-related transfers)
-Total cross chain transactions: 143
Breakdown of bridge usage and volumes below.

The funds are currently unspent across 4 Ethereum addresses:
0xbddae987fee930910fcc5aa403d5688fb440561b
0x0fe3b6908318b1f630daa5b31b49a15fc5f6b674
0xaa843ed65c1f061f111b5289169731351c5e57c1
0xd3feed5da83d8e8c449d6cb96ff1eb06ed1cf6c7
intel.arkm.com/explorer/enti…

Chainflip paused their Solana bridge as soon as the hacker started using their bridge 👏🏻xitter.cf/i/status/2039426069967…


Attacker addresses linked to the Jan 5 and Jan 8 Kontigo hack. (Base/Ethereum)
Jan 5 attack:
0x1347914ac3184382e955e2b26089743836cb24a0
0xfeeb5227ef65eb78ef6baccbcd643944103684f6
0x61FcBA9828c8f65B1C5a62E420B1F56517f6FcD7


On-chain sleuth 🕵️ retweeted
Phishing is a year-round sport...
...but crypto has been providing especially bountiful waters lately.
When it comes to the experts, it seems nobody is safe.
What lurks in the murky depths?
rekt.news/gone-phishing/

On-chain sleuth 🕵️ retweeted
It appears North Korea is also responsible for the $54M @coinexcom hack from yesterday after they accidentally connected their address to the $41M Stake hack on OP & Polygon.
0x75497999432b8701330fb68058bd21918c02ac59

Stolen tokens on on all 3 chains are being converted to thier native tokens.
Additionally, a portion of the funds on Polygon has been transferred to a new address
oklink.com/polygon/address/0…
@coinexcom


Looks like keys compromised. Outflows from lots of their hot wallets across many chains.
Zach dropped more theft addies here 👉 t.me/investigations
CoinEx has been around a while and has shit across all the chains. I expect more outflows to be found in coming hours.

Stolen funds on Ethereum are on the move.
3,365.31 ETH worth $5.35 million is transferred to a new address (0x2118e4432d668aCFa347ddBA0efCcc6BB04DB297)
#hack #ETH
@coinexcom
As more information emerges and losses extend to two additional chains, BTC and XRP, the total stolen amount has surged significantly!
BTC: 1BHNb9UJy4cWFB5wywZkTVgoNB4JbFmswH - 231 BTC ($6M)
XRP: rpQxVcjVF2fC23r3xKyJS53jw8d5SRhZQf - 12,625,364 XRP ($6.1M)
xitter.cf/coinexcom/status/17016…

#CoinExResponseUpdate - We have identified and isolated the suspicious wallet addresses linked to the hack:
$ETH:
*0xce013682eddefaca8c94fe56a43a04212ebe4673
*0x8bf8cd7F001D0584F98F53a3d82eD0bA498cC3dE
*0xCC1AE485b617c59a7c577C02cd07078a2bcCE454
*0x483D88278Cbc0C9105c4807d558E06782AEFf584
$BTC:
*1BHNb9UJy4cWFB5wywZkTVgoNB4JbFmswH
$TRON:
* TP75t6owoqXxskLq6FB2R37PymNTmohq9L
* TPFUjxQzG88Vwynrpj2W61ZAkQ9W2QYgAQ$XRP:
* rpQxVcjVF2fC23r3xKyJS53jw8d5SRhZQf
We are actively collaborating with the affected crypto projects to formulate a solution. Furthermore, we urge crypto projects and our fellow crypto exchanges to remain vigilant. If you detect any unusual or related activities from the aforementioned wallet addresses, please contact us immediately.
By standing together, we could navigate and surmount any challenges that come our way.
🚨 Stolen funds from @Stake on BNB chain are on the move! via @axelarcore @squidrouter, shifting from BNB to AVAX.
Sending/Receiving address address on BNB/AVAX: 0x695A2a6713D911fA48D9b0e2eb936F95575Ad894


On-chain sleuth 🕵️ retweeted

Looks like the @coinspaid hack might be more than what's report:
Ethereum (ETH) Network Loss:
Addresses: -0x68aff47f17ec39015d921bbb70a190197e349de2
Amount Lost: 6,698.96 ETH, equivalent to $12.5 Million
Tron (TRX) Network Loss:
Address: -TUGFXFeoQ72w9EpYPibUNhXwzzKKmkNQp6
Amount Lost: 29,688,313 USDT and 3,228,250 TRX, equivalent to $29.68 Million and $0.26 Million respectively.
Bitcoin (BTC) Network Loss:
Addresses:
-3H2Sb2YrHrgtNw9uuYJkpEfN8HvignqqzH -37sevJj8VsWv2Y82CVtiHutnNqQAYsCTNn
Amount Lost: 12.9 BTC (equivalent to $376,397.49) and 34.51584939 BTC (equivalent to $1,005,740.08)
The total loss across all networks amounts to $43.87Million at this time.


CoinsPaid is back to processing after being hit by a hacker attack. Сlient’s funds were not affected and are fully available.
More details in our blog: coinspaid.com/tpost/0zx28tmj…

ALT CoinsPaid is back to processing after being hit by a hacker attack
On-chain sleuth 🕵️ retweeted
🚩MistTrack Update🚩
Recently, the crypto community has been stirred by a sequence of incidents involving @coinspaid, @AtomicWallet, and Alphapo.
A veneer of mystery shrouds these incidents, yet there's a possibility that Lazarus might be behind them all!

On-chain sleuth 🕵️ retweeted

Web wallets are impossible to secure.
I know because I built one too.
I don't know why yall insist on repeating history.
Even if you manage to secure your own product and infrastructure, the hackers will just hack the infrastructure of the internet.
theverge.com/2018/4/24/17275…


I can’t believe that in 2023 someone built a browser wallet - @MutinyWallet is a terrible idea and NOBODY should use it!
We spent YEARS (2014 - 2017) trying to find ways to secure @MyMonero’s web wallet release against an ever-increasing series of attacks including:
- registering thousands of domains to block phishing attempts
- paying @PhishFort thousands of Dollars to monitor and takedown phishing sites
- working with tier 1 ISPs to block ongoing BGP rerouting attacks
- became deeply embedded with @gandi_net’s security team after hundreds of social engineering attempts at stealing our domain
- working with @Cloudflare when an insider was allegedly trying to sell access to our CF control panel
- took full advantage of things like the HSTS preload list and SRI (even when it wasn’t widely supported)
- creating an entire browser plug-in called SafeBrowse which used DNS TXT records to serve out-of-band hashes of JavaScript and HTML objects to ensure they were safely delivered to the browser
- working with @tayvano_ to share intel as they faced similar challenges with @myetherwallet
Despite all of that, the cumulative losses of users JUST to MyMonero phishing sites must be in the millions of Dollars. I cannot begin to tell you how soul-crushing it is when a user insists that they are technically competent and weren’t stupid, only to have them dig into their browser history and realise they weren’t on the .com but on some phishing site😔
Eventually we released mobile and desktop apps, because even though we can’t have reproducible builds on iOS devices, it’s at least an attack surface we all understand. Classes of attacks like phishing apps in the Google App Store are fixable, and hardly infinite.
It is literally impossible to secure a web wallet attack surface, which is why tools like BrainWallet were deprecated and removed from the live internet. Don’t use web wallets!
🚨Suspicious BTC addresses alert!
These addresses are most likely linked to The Lazarus group:
3MGGaHbbEoiYxMwVP122vqEkTzArJp42gy
32gb99jbM3WZh4jjBar8JrU6uMHsR53zYN
38uYxAYg89wynwQkZFPMsvSjhUYPgeU2cD
3K51fnck4PKSoYWQ8ttwoe3nfZcc4BcPj4
A total of 1,200 BTC has been gathered in these 4 addresses through Sinbad Mixer, and the funds remain unutilized.
👀Watch out for a sudden influx of funds flowing towards #Avalanche
#Atomicwallet #LazarusGroup #SinbadMixer #NORTHKOREA #hack
🚨 Keep an eye on these addresses:
3GRPGErVNW7zLh1jP1rSBCm6NYtP7TDx8Z
3DiESmnv611axcvcj6d4i8WA8i52q9KFkJ
3GFPYbffaN14Dy2tdMq7vfk1UoZFtdoyFi
3CfxTy1QW6LL3NBCiiHvpUNFzHTiJaWzXw
3PSwvYKyeXdEkBNZdwQNtvznPtQk45rYEL
#AtomicWalletHack
#lazarus #NorthKorea
Based on their previous hacks (#HARMONY and #Ronin), this group follows a consistent pattern for their Bitcoin transactions: Stolen funds -> #SinbadMixer -> Avalanche Bridge -> Tron/Ethereum/Back to Bitcoin.