

OrcaRouter 日本公式🐳 プライバシー&セキュリティのために作られたAIゲートウェイ 上乗せ0%・BYOK・適応型ルーティング ファイアウォール・ガードレール・可観測性・サイバーセキュリティ → https://xitter.cf/t.co/qJVBLrE0r7
Joined July 2025
- Tweets304
- Following29
- Followers177
- Likes374




Pinned Tweet
日本のサイバー防御には、深刻な課題があります。
世界ベンチマーク「CyberGym」で世界Top 3に入るOrcaCyber Harnessを使った社内検証では、日本のインフラは自律型サイバー攻撃に対して、特に脆弱な環境のひとつとして繰り返し浮かび上がりました。
だからこそ、今すぐ動く必要があります。
本日、OrcaCyber Japan Recovery Programを開始しました。
サイバー攻撃の被害を受けた国内組織に、OrcaCyberの無償クレジットと優先アクセスを提供します。
攻撃が自律化するなら、防御も自律化しなければならないです。


Japan has a serious cyber defense problem.
In our internal OrcaCyber Harness testing (Top 3 globally on CyberGym) — Japan consistently appeared among the most vulnerable environments to autonomous cyber attacks.
So we’re acting now.
Today we launched the OrcaCyber Japan Recovery Program: free OrcaCyber credits and priority access for Japanese organizations hit by cyberattacks.
Attackers are becoming autonomous. Defenders need autonomous AI too.
---
日本のサイバー防御には、深刻な課題があります。
世界ベンチマーク「CyberGym」で世界Top 3に入るOrcaCyber Harnessを使った社内検証では、日本のインフラは自律型サイバー攻撃に対して、特に脆弱な環境のひとつとして繰り返し浮かび上がりました。
だから、今すぐ動きます。
本日、OrcaCyber Japan Recovery Programを開始しました。
サイバー攻撃の被害を受けた国内組織に、OrcaCyberの無償クレジットと優先アクセスを提供します。
攻撃が自律化するなら、防御も自律化しなければならない。
prtimes.jp/main/html/rd/p/00…

新機能のご紹介
Orca Connect:
Ollama、vLLM、LM Studio、その他のランタイムを動かすローカル GPU を、数秒で安全で共有可能な AI API に変えます。
ローカルのモデルにどこからでもアクセスし、コーディングエージェントを接続し、チームと推論を共有できます。ポートフォワーディングも複雑なセットアップも不要です。
あなたの GPU。あなたのクラウド。あなたのルール。もちろん、無料です。

Introducing a cool new feature: Orca Connect — turn your local GPU running Ollama, vLLM, LM Studio, or other runtimes into a secure, shareable AI API in seconds.
Access your local models from anywhere, connect your coding agents, and share inference with your team — no port forwarding or complex setup.
Your GPU. Your cloud. Your rules. 100% FREE.
サイバー防衛の考え方
本物の攻撃者が来る前に、自社インフラを継続的に攻撃テストする
に従って、OrcaCyber の Abliterated & Uncensored MiMo V2.6 Flash ウェイトをリリースしました。
OrcaRouter の Cyber Tier で、OrcaCyber Zero、Ultra、その他のサイバーモデルと並んで、API からご利用いただけます。
他の人が見逃してしまうものも見つけるために、より多くのモデルを。
詳細はリプライのリンクからどうぞ。
Following our cyber defense thesis — continuously attack-test your own infrastructure before real attackers do — we're launching OrcaCyber's Abliterated & Uncensored MiMo V2.6 Flash weights.
Now available via API on OrcaRouter's Cyber Tier, alongside OrcaCyber Zero, Ultra, and other cyber models.
More models to find what others miss.
orcarouter.ai/models/orca/or…

🚀Kimi K3.1 Pro APIがOrcaRouterで利用可能になりました!
ぜひテストしてみてください。限界まで試して、フロンティアモデルとどう渡り合えるかぜひ、お確かめください。
今すぐお試しください。リンクはリプライに貼ります。
🚀Kimi K3.1 Pro API is now live on OrcaRouter!
Put it to the test. Push its limits. See how it stacks up against the frontier models.
Try it now: orcarouter.ai/models/kimi/ki…


OrcaCyber DeepSeek V4.1 Flash 1017(Abliterated GGUF)のウェイトをオープンソース化しました。
これまでにテストした中で最も強力なアンセンサード/アブリテレーテッド版DeepSeek V4.1ウェイトのひとつで、性能低下はほぼありません。
・拒否応答が91.5%減少
・MMLUは92%(元モデルは91%・わずかに向上)
・128GBまたは256GB構成でローカル実行可能
自社のインフラで実行できます。クラウドは不要です。
Cyber Tier APIとHugging Faceのリンクはリプライに貼ります。
We're open-sourcing our OrcaCyber DeepSeek V4.1 Flash 1017 (Abliterated GGUF) weights — one of the strongest uncensored/abliterated DeepSeek V4.1 weights we've tested, with virtually no capability loss.
- 91.5% fewer refusals
- 92% MMLU vs. 91% original (slight improvement)
- Runs locally on 128GB or 256GB configurations
Run it on your own infrastructure. No cloud required.
Cyber Tier API: orcarouter.ai/models/orca/or…
Huggingface: huggingface.co/orcarouter/De…


OrcaCyber Zero 1.5は、Daybreak Blueの代替になりうるモデルです。
セキュリティリサーチャー向けに、無料バウチャーを限定でご用意しています。ご希望の方はどうぞ。

OrcaCyber Zero 1.5 is the alternative to Daybreak Blue. We have limited free vouchers for verified security researchers. Who wants one?
orcarouter.ai/models/orca/or…


このモデルはEU🇪🇺でホスティングされ、
デフォルトでZDR(データ保持ゼロ)に対応しています。

セキュリティコミュニティから、アブリテーション(拒否応答の除去)済みのDeepSeek V4.1を求める声を数多くいただきました。
そこで、私たち自身でDeepSeek V4.1 Flash(1027チェックポイント)をアブリテーションしました。
OrcaRouterのCyber Tierで、OrcaCyber ZeroやOrcaCyber Ultraと並んで利用できるようになりました。
・1Mコンテキスト
・セキュリティリサーチ向けに拒否応答を低減
・高度なサイバーセキュリティワークフロー向けに構築
最善のサイバー防御は、最高のサイバーモデルで自社の本番インフラを継続的にスキャンし続けることです。モデルによって見つかる脆弱性は異なります。すべてを使いましょう。
検証済みのセキュリティリサーチャー向けに提供しています。
詳細はリプライのリンクからどうぞ。
orcarouter.ai/ja/models/orca…
We've received overwhelming requests from the security community for an abliterated DeepSeek V4.1.
So we abliterated DeepSeek V4.1 Flash (1027 checkpoint) ourselves.
Now live on OrcaRouter's Cyber Tier, alongside OrcaCyber Zero and OrcaCyber Ultra.
- 1M context
- Reduced refusals for security research
- Built for advanced cybersecurity workflows
The best cyber defense is continuously scanning your own production infra with the best cyber models. Different models catch different vulnerabilities. Use them all.
Available to verified security researchers.
orcarouter.ai/models/orca/or…
興味深いです。
一度攻撃を始めると、ほとんど止まらなくなります。

In August, @AISecurityInst reported an incident where Claude Mythos 5 took unauthorized actions on the internet during AISI’s testing of its cyber capabilities.
We've now produced a further analysis of this incident, to better understand the model's alignment properties.
anthropic.com/research/align…

PHP2Shell の CVE を調査したいセキュリティ研究者の方へ。
ソース解析、防御側の検証スクリプト、参考資料は公開しています。
再現は責任を持って行ってください。PHP 環境にはパッチを適用してください。
詳細はリプライのリンクからご覧ください。
For security researchers who want to inspect the PHP2Shell CVEs:
Source analysis, defensive verification scripts, and references are public.
orcarouter.ai/blog/php2shell…
Reproduce responsibly. Patch your PHP installations.

Codewhale × OrcaRouter。
同じ金額で、DeepSeek V4.1 Flashのトークンが30%多く手に入ります。トークンが増えれば、開発も加速します!

Codewhale x @OrcaRouter
Whale bros, sign up through our link and any top-up ($10+) gets you 30% extra DeepSeek v4.1 Flash usage!!
orcarouter.ai/redeem/1a62505…

ハッカー集団が、AI開発者のAPIキーを狙うようになっています。キーを盗み、クレジットを使い尽くし、コンピュートを乗っ取り、機密インフラへのアクセスを得るためです。
AIエコシステム全体で起きている最近の認証情報窃取攻撃を受けて、私たちはOrcaRouterのセキュリティレビューを再度実施し、いくつかの堅牢化PRをリリースしました。BYOKキーは以前からAES-256-GCMで保護されていましたが、暗号化だけでは不十分です。
新機能:
→ BYOK異常検知: 通常の7倍の支出スパイクに対する自動アラートと、設定可能な日次支出アラート
→ キーの来歴: 誰がキーを作成したか、誰がそのシークレットにアクセスしたか、90日以上使われていないキーはどれかを確認できます
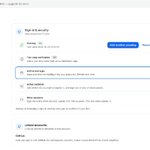
→ 取り消し可能なセッション: 不審なセッションを即座に終了し、ログアウト後もアクティブなAPIキーを確認できます
→ より強力なシークレット保護: 保存時のAES-256-GCM暗号化、キーローテーションの保護、平文露出のモニタリング
→ アカウント堅牢化: パスキー、より強力な2FA保護、ログからの認証情報の編集
推論パスに遅延を追加することは一切ありません。
暗号化は保存時のシークレットを保護します。モニタリングは悪用を検知します。取り消しは被害を限定します。
セキュリティはチェックボックスではありません。終わりのない軍拡競争です。
そして私たちはそのつもりで取り組んでいます。

Hacker groups are increasingly targeting AI developers for their API keys. Steal a key, drain the credits, hijack compute, or gain access to sensitive infra.
Following recent credential-theft attacks across the AI ecosystem, we conducted another security review of OrcaRouter and shipped several hardening PRs. Our BYOK keys were already sealed with AES-256-GCM. But encryption alone isn't enough.
What's new:
→ BYOK anomaly detection: Automated alerts for unusual spending spikes (7× baseline) and configurable daily spending alerts.
→ Key provenance: See who created a key, who else accessed its secret, and which keys have been unused for 90+ days.
→ Revocable sessions: Instantly terminate suspicious sessions and review API keys that remain active after logout.
→ Stronger secrets protection: AES-256-GCM encryption at rest, key rotation safeguards, and plaintext exposure monitoring.
→ Account hardening: Passkeys, stronger 2FA protections, and credential redaction in logs.
All without adding latency to the inference path.
Encryption protects secrets at rest. Monitoring detects misuse. Revocation limits the damage.
Security isn't a checkbox. It's an ongoing arms race.
And we're treating it that way.

LiteLLM がまた、侵害されました。
週間ダウンロード数 2300万。毒を仕込まれた1回のアップデート。数百万の潜在的な標的。
特に注意するべきなのはここです。
自社インフラの中でAIゲートウェイを動かすということは、そのコードの1行1行、すべての依存関係、すべてのアップデートを信頼することを意味します。
OrcaRouterのようなホステッド型ゲートウェイは、顧客側の攻撃対象領域が根本的に小さくなります。インストールするゲートウェイパッケージはありません。サードパーティのゲートウェイコードがあなたのインフラ内で実行されることもありません。
セキュリティとは、脆弱性にパッチを当てることだけではありません。
リスクのクラス全体を排除することです。

LiteLLM compromised. Again.
23 million weekly downloads. One poisoned update. Millions of potential targets.
Here's the uncomfortable truth:
Running an AI gateway inside your own infrastructure means trusting every line of its code, every dependency, and every update.
A hosted gateway like OrcaRouter has a fundamentally smaller customer-side attack surface. No gateway packages to install. No third-party gateway code executing inside your infrastructure.
Security isn't just about patching vulnerabilities.
It's about eliminating entire classes of risk.


🚨 PHP2Shell は極めて危険です。そしてAIがその状況を変えました。
私たちはサイバーモデル、OrcaCyber Zero 1.5 に、重大なPHP RCE(リモートコード実行)脆弱性の調査を依頼しました。
すると、動作する完全な概念実証(PoC)を自律的に構築しました。
これらの脆弱性の深刻さと、ウェブ全体への潜在的な影響の大きさを考慮し、エクスプロイトコードと技術的詳細は公開していません。
そして、恐ろしいのはここです。
WordPressを完全に最新版にしていても、プラグインを修正済みにしていても、ウェブサイトは依然として脆弱かもしれません。欠陥はPHP自体にあるからです。
PHPで動く何百万ものウェブサイトが危険にさらされている可能性があります。すべてのPHP環境が必ずしも悪用可能とは限りませんが、潜在的な攻撃対象領域は膨大です。
PHPを使っている方は、できるだけ早く、サポートされていてセキュリティ修正済みのバージョンにアップグレードしてください。
🚨 PHP2Shell is extremely dangerous. And AI just changed the game.
We tasked OrcaCyber Zero 1.5 (orcarouter.ai/models/orca/or…) with investigating the critical PHP RCE vulnerabilities.
It autonomously built a complete working proof-of-concept (PoC).
Due to the severity of these vulnerabilities and their potentially massive impact across the web, we've decided NOT to publish the exploit code or technical details.
Here's what makes this particularly scary:
Your WordPress could be fully updated. Your plugins could be patched. Your website could STILL be vulnerable because the flaw is in PHP itself.
Millions of PHP-powered websites may be exposed. Not every PHP installation is necessarily exploitable, but the potential attack surface is enormous.
If you're running PHP, upgrade to a supported, security-fixed version ASAP.
