
Ransomware Researcher | CTF Player
South Korea
Joined May 2024
- Tweets539
- Following158
- Followers1.5K
- Likes572



Hyuna Lee retweeted
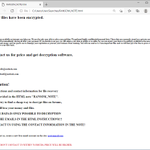
BlackField #Ransomware
md5: 88da420dd5d82f1ca7c247f1305e37c4
ext: .BlackFL
note: BlackField-ReadMe.txt
DLS: xcou7t6a4qlecsr7ipmxlwsseghxbebqltnxwaurxx3bbsbts7ljacqd[.]onion
mail: [email protected], [email protected]

Hyuna Lee retweeted
🚨 New #Ransomware Group: Reynolds
DLS: bs2tlg32pfjwmclm22cyngqmoo24cdlhfxzbruwrdaxumisfeory32qd[.]onion

Hyuna Lee retweeted

#Ymir #ransomware Some Related Samples
💮bazaar.abuse.ch/browse/tag/Y…
Ip Related Samples
✅bazaar.abuse.ch/browse/tag/8…
✅bazaar.abuse.ch/browse/tag/9…
✅bazaar.abuse.ch/browse/tag/7…
Reference
🧾securelist.com/new-ymir-rans…
🧾xitter.cf/malwrhunterteam/status…


#Ymir #ransomware, a new stealthy ransomware grow in the wild
securityaffairs.com/170814/m…
#securityaffairs #hacking #malware
@kaspersky @KasperskyLabIT @e_kaspersky @Kaspersky_ru


Hyuna Lee retweeted

🇰🇵 Lazarus Group cluster (BeaverTail)
165.140.86.227:1244/pdown (1/94 VT)
66.235.168.232:1244/pdown (1/94 VT)
45.43.11.201:1244/pdown (1/94 VT)
38.92.47.151:1244/pdown (1/94 VT)
38.92.47.91:1244/pdown (3/94 VT)
38.92.47.85:1244/pdown (1/94 VT)
147.124.197.138:1244/pdown (1/94 VT)
147.124.197.149:1244/pdown (1/94 VT)
hunting query on @urlscanio:
page.url:\:1244\/pdown
#IOC #Threat #APT #CTI #ThreatHunting

🇰🇵Lazarus Group cluster (BeaverTail)
/23.106.70.154:1244/pdown (0/94 VT)
/23.106.253.194:1244/pdown (8/94 VT)
/23.106.253.215:1244/pdown (1/94 VT)
/23.106.253.221:1244/pdown (1/94 VT)
/23.106.253.242:1244/pdown (0/94 VT)
How it works.
🦫BeaverTail downloads a Python executable (`p[.]zip`) to the compromised machine from `<C2server>:1224/pdown`.
p[.]zip hash
6a104f07ab6c5711b6bc8bf6ff956ab8cd597a388002a966e980c5ec9678b5b0
Downloading Python is necessary to execute the InvisibleFerret backdoor payload, as it is written in Python. This enables InvisibleFerret to operate across multiple operating systems (Windows, Mac, and Linux).
Ref:
group-ib.com/blog/apt-lazaru…


Hyuna Lee retweeted

Seraphin Ransomware panel.
This claim was never confirmed or denied. @amazon
I can confirm that Seraphin changed their name during the final building stage.
Seraphin —> Embargo Ransomware.

Hyuna Lee retweeted

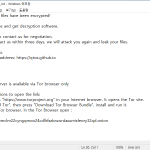
#delshad #ransomware
IOC;
notmalicious[.]services
hello.exe
Malware url:
virustotal.com/gui/file/c367…


Hyuna Lee retweeted
After #OperationMagnus, the takedown of #RedLine Stealer and #META Stealer, #ESETresearch is publicly releasing our and Flare’s @flaresystems 2023 research into RedLine's backend, along with recent discoveries made based on data shared with us by the Dutch National Police: welivesecurity.com/en/eset-r… 1/6
Hyuna Lee retweeted

ICYMI: Excellent @ReliaQuest threat report on Scattered Spider, which is now running with the RansomHub RaaS
🔎 They used social engineering against the help desk to compromise the CFO’s account and then socially engineered the helpdesk to get DA too 🤦♂️
reliaquest.com/blog/scattere…

Hyuna Lee retweeted
#hellcat #helldown #ransomware #IOC's 0bfe25de8c46834e9a7c216f99057d855e272eafafdfef98a6012cecbbdcfabf Hellenc.exe 3e3fad9888856ce195c9c239ad014074f687ba288c78ef26660be93ddd97289e 7cd7c04c62d2a8b4697ceebbe7dd95c910d687e4a6989c1d839117e55c1cafd7
Hyuna Lee retweeted

Sample is now on VT!
🚩Hash: 561b29a5650ff7fe6e63fa19c29ee240
🎯Actor name: ScarCruft
🔹Comment: ScarCruft, also widely known as APT37 or Reaper APT, is an espionage group associated with North Korean state activities that target high-value individuals. The group has been active since 2012, and while its primary target is South Korea…
🌐URL: socradar.io/threat-actor-pro…
🔎OnVT: virustotal.com/gui/file/561b…

Hyuna Lee retweeted

Using @Huntio to hunt for 🇰🇵Lazarus/APT38 clusters is an effective way to understand which crypto-related companies are targeted by this threat actor.
For example, we've observed a DPRK threat actor using the host 104.168.165.165 to create fake Hack VC subdomains, such as.
/hack-vc.online-meets.xyz
/hack-vc.video-meets.pro
/xyzhack-vc.video-meets.xyz
/video-meets.xyzhack-vc.video-meets.xyz
/hack-vc.video-meets.xyzhack-vc.video-meets.xyz
/hack-vc.video-meets.xyz
/hack-vc.video-meets.site
to impersonate/target the company.


Hyuna Lee retweeted
"encrypter-linux-esxi-x86", a sample of Beast ransomware's Linux version: 66f86812a6593cdd760cd2119f8bf1a76f33a1b56ab099edc02de7b0629ea15d
It's on VT from months ago, but at the last time it was scanned, a week ago, still had only 2 detections...
🤷♂️


Hyuna Lee retweeted

Schneider Electric after being hit by ransomware for the third time
Jun 28, 2023 — cl0p ransomware
Feb 20, 2024 — Cactus ransomware
November 4, 2024 — Hellcat ransomware

Hyuna Lee retweeted

UNCOVERING 🇺🇸POLITICAL CAMPAIGN
152.53.38.103 🇦🇹
IP found with Sensitive #US #Data: Voters List, Verifications & #Rhysida #Ransomware Group leaks!
More info: justpaste.it/aco20
#FBI #CISA #infosec #Election2024 #databreach #OSINT #threatintel #security #infosec #hack


Hyuna Lee retweeted

VT 0 detections, 🧐. Looks like we’ve got ourselves an #ELF edition of #Helldown #Ransomware at #IOC 78.46.194[.]43/e.dat, zeroing in on VMware virtual platforms. It’s going for .vmdk, .vswp, .log, .vmem, .vmsn, and .vmx files. Stay vigilant!⏰⏰ @Xlab_qax


Hyuna Lee retweeted
#ransomware was found on this IP that is possibily #hellcat ransomware
virustotal.com/gui/file/6ef9…


VT 0 detections, 🧐. Looks like we’ve got ourselves an #ELF edition of #Helldown #Ransomware at #IOC 78.46.194[.]43/e.dat, zeroing in on VMware virtual platforms. It’s going for .vmdk, .vswp, .log, .vmem, .vmsn, and .vmx files. Stay vigilant!⏰⏰ @Xlab_qax
Hyuna Lee retweeted
Some low detected x64 Linux ransomware sample: 20e0e61d27762a524f6974fb9f4995062582db351d5576e62a214d6b5e5808e7
"WEAXOR" is the name used on the payment / chat site.
🤔
193.143.1[.]139


Hyuna Lee retweeted

#WEAXOR #Ransomware
What's it?
Is this a rebranding of #Mallox ransomware?
weaxorpemwzoxg5cdvvfd77p3qczkxqii37ww4foo2n4jcft3mytbpyd[.]onion
lazylazy@tuta[.]com
help.service@anche[.]no
virustotal.com/gui/file/e21c…
