

PakCrypt Community exists to develop people who can design, analyze, and prove cryptographic systems. As Pythagoras said in 500BCE "Number rules the universe."
Islamabad
Joined October 2023
- Tweets2.5K
- Following0
- Followers53
- Likes453




PakCrypt.Org retweeted
🚨 The hidden danger in Pakistan's new 5G cores isn't the radio. It's the control plane.
💰📡 Context:**
Pakistan's first 5G auction closed in March 2026 - $507M raised.
Jazz, Ufone & Zong are now building brand-new 5G cores for 201M subscribers.
Everyone is looking at towers and handsets.
The real risk sits *inside* the core.
---
🔄 🏗️ The Architectural Shift That Changed Everything**
5G killed the old closed signalling.
The core is now a Service-Based Architecture.
AMF, SMF, UDM, AUSF, NRF, PCF... are all microservices talking over HTTP/2 + JSON, authenticated by OAuth 2.0 tokens from the NRF.
👾 The consequence:**
A compromised or rogue Network Function can send requests that are syntactically perfect but semantically hostile.
> Register a fake function
> De-register subscribers
> Read subscription data
> Tear down sessions
> Poison service discovery
Traffic looks 100% legitimate because it *follows the spec*.
---
💥 🧨 The Cores Are Already Fragile**
- CoreCrisis found 13 crashing vulns across open + commercial cores, including auth bypass and billing fraud.
- iFinder [2026 multi-agent audit] found 84 unknown vulns in 7 open-source cores - 81 CVEs - including session hijacking confirmed on a real commercial core.
- State actors are already in telecom: CISA AA25-239A [Aug 2025] documented Salt Typhoon geolocating subscribers and recording calls.
---
🧱 Why Current Detection Fails - 4 Structural Problems:**
**1️⃣ Datasets are single-implementation.**
Public traces = free5GC or PFCP DoS only. 5G-NIDD covers radio/user-plane, not the SBI. No multi-core, leave-one-implementation-out dataset exists.
**2️⃣ Detectors don't transfer.**
Supervised NIDS models lose ~56% F1 when moved to another dataset. They learn implementation artefacts, not the attack. Pakistan runs mixed-vendor networks and will swap vendors over a license life - but cross-implementation transfer has never been measured.
**3️⃣ Learned detectors are evadable.**
On 5G core PFCP, models with clean AUC 1.000 can be fully evaded by genetic-algorithm perturbations.
**4️⃣ The standard itself has a blind spot.**
3GPP NWDAF abnormal-behaviour analytics [TS 23.288] defines exceptions like "suspected DDoS" and "too-frequent service access" - all centered on User Equipment. There is NO exception for a misbehaving Network Function.
Operators buy signalling protection as closed boxes. Pakistan has no domestic means to independently test them.
Detection is unsolved. Datasets don't exist. Standards don't cover the threat. And attackers are already inside.
**🛡️ That is the problem SpecGuard-5GC is trying to solve.**
#5G #Pakistan #TelecomSecurity #5GCore #SpecGuard5GC

PakCrypt.Org retweeted
🚨 THE RADIO THE US INTEL AGENCY COULD READ BEFORE IT WAS EVEN SOLD
A forensic teardown of a real Cold War backdoor. And why it matters today.
1/ WHAT WAS THE UA-8295?
In 1984, Dutch company USFA (Philips) sold the UA-8295 Short Burst Terminal - a military field radio for short-wave.
Under the hood it was a Nokia device that originally used DES.
But from 1977, NSA had a deal with USFA: supply a WEAKER version to foreign customers.
It was sold to Belgium, UK, and a version with Arabic keyboard to Saudi Arabia.
From outside it looked identical. Same version number, same UI, even same checksum.
The paper by Maatje & Stevens (CWI) is the FIRST public reverse-engineer of it.
eprint.iacr.org/2026/1309.pd…
2/ THE BACKDOOR CONJECTURE - A NEW FORENSIC TOOL
The authors propose a simple idea to catch backdoors:
Conjecture: A backdoor has 2 goals:
(i) optimize a SECRET attack
(ii) look secure under casual review
So every design choice is either:
Class (i) = tuned for the attack
Class (ii) = tuned to look normal
If we guess the attack, Class (i) choices should be weirdly OPTIMAL.
That optimality is evidence. This is their forensic methodology.
3/ HOW WAS IT BACKDOORED? NOT BY CUTTING KEY BITS.
No simple "56-bit -> 40-bit" trick. It's sneakier.
Inside is a custom cipher called SBTcipher:
56-bit key, 64-bit block, 8 rounds
Rounds = BiP -> Mix -> ByP (byte permute) -> NS -> SB
Two killer flaws:
(i3) Weak Mixing:
Mix only mixes a nibble with another nibble's crumb (2 bits) with prob 1/4, else does nothing.
Expected mixing per nibble:
E[Z_nibble] = (3/4 * 0) + (1/4 * 2) * (3/4) = 3/8 bits
Per full byte path (16 Mix calls):
E[Z_path] = 6 bits only!
So byte paths barely talk to each other.
(i5) The Big Interaction:
Each byte path uses 40 control bits, but only 19-25 UNIQUE key bits.
Table from paper:
Path 7: 24 bits, Path 6: 25 bits, Path 1: 19 bits ...
So 56-bit key splits into 8 small puzzles.
For a single path, expected candidate list size:
log2(E[|L_a|]) = U_a - 2
Example: U_1 = 19 -> |L_1| ~ 2^17 = 131k keys. Small!
4/ TWO ATTACKS - LAPTOP IN A WEEKEND
They built 2 practical key-recovery attacks needing just 1 known plaintext/ciphertext block:
A) List Merge Attack:
Generate list of valid partial keys per byte path, then merge lists where they agree on overlapping key bits.
After 5 paths merged, only 5 bits left -> brute force.
With likelihood sorting, median time drops 3x.
B) Branch-and-Prune Attack:
Depth-first search on key bits with constraint propagation. Keeps a domain for each nibble (0-15 values) and prunes when empty.
Memory: ~3 MiB. Could fit in a 640 KiB PC from the mid-80s.
Results on modern server (but would run on 1980s Cray):
0 extra pairs:
List Merge median ~12429 sec (~3.5h) + ~131 sec precomp
Branch-and-Prune median ~33311 sec (~9h)
1 extra pair:
List Merge: 20 sec
Branch-and-Prune: 179 sec
2 extra pairs:
List Merge: 0 sec
Branch-and-Prune: 7 sec
3 extra pairs: 2-5 seconds.
Translation: With just 2-3 short messages, NSA in the 80s could recover keys daily.
5/ FORENSIC TWIST: WAS IT INTENTIONAL?
They tested if the byte permutation ByP was chosen to be optimal for the attack.
Using cheap predictors an attacker would use in the 80s (M2 = sum of unique bits per path, M3 = max bits per path):
ByP_org is ranked 1/3435, 1/1462, 1/844, 1/485 across realistic sets. It is literally the #1 optimal choice.
But the constant IV? Choosing IV from max-prob-wrap class only speeds up attack by 1.25x. No strong structure. So IV was likely Class (ii) - just to look secure.
This matches the Backdoor Conjecture perfectly.
6/ WHY YOU SHOULD CARE - PRACTICAL IMPACT
a) This is NOT history. Same pattern seen in:
- Crypto AG / Operation RUBICON: CIA/BND read 96% of traffic from 120 countries for 50 years
- Dual-EC DRBG in RSA BSAFE (paid $10M by NSA)
- TETRA: police radios worldwide using TEA-1, TEA-3 backdoored in 2023
- Juniper: someone hijacked NSA's Dual-EC backdoor for themselves
b) It teaches real backdoor engineering:
Don't make key small - make mixing fail and make key schedule interact with permutation. Looks secure to casual audit.
c) It gives us a detection method:
Future audits of closed-source crypto can use this forensic optimality test.
Security isn't just about math being correct. It's about who designed it, why that permutation was chosen, and whether you can verify it.
#cryptography #infosec #backdoor #NSA #forensics

PakCrypt.Org retweeted
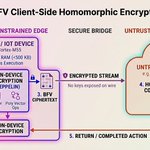
ok fully homomorphic encryption is actual black magic and we're not talking about it enough
you can run ANY computation on data while it stays fully encrypted the whole time. you send encrypted data to a server, it does all the work, sends back an encrypted result, you decrypt it and it's exactly what you would have gotten if it ran on the raw data. the server never sees shit.
why this is huge:
- cloud computing where the cloud can't spy on you
- AI that can do inference on your private data without ever seeing it
- medical research where hospitals let you analyze patient data without ever giving you the decryption keys
untrusted servers processing sensitive data safely. that's the dream.
so why isn't everything using it?
because the math is cursed. it's all lattice-based cryptography, LWE and Ring-LWE problems. and every operation you do adds invisible noise to the ciphertext. do too much and the whole thing breaks and becomes undecryptable.
the fix is called bootstrapping - refreshing the ciphertext to remove noise WITHOUT ever decrypting it. implementing and optimizing that requires math intuition that normal software engineering just does not teach.
#CyberSecurity #CryptoCommunity #CryptoGems


PakCrypt.Org retweeted
Do you know that The G7 Cybersecurity Working Group just issued a blunt global directive? Migrate to PQC at earliest !
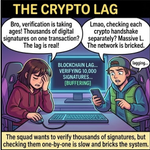
But for blockchain architectures, the new math presents an existential crisis: quantum-resistant signatures are astronomically bloated. If we forcefully bolt them onto the base layer, we save the network from quantum decryption but murder it through extreme centralization.
The Physics of Cryptographic Bloat:
Analyze this through the lens of pure network physics. The G7 is entirely correct: a Cryptographically Relevant Quantum Computer (CRQC) will eventually shatter the public-key cryptography (like ECDSA) that underpins decentralized finance. The "Harvest Now, Decrypt Later" doctrine is an active, operational reality.
But the prescribed cryptographic cure is currently as lethal as the disease.
The operational elegance of Bitcoin is rooted in its ruthless cryptographic efficiency. A standard secp256k1 ECDSA signature requires a mere 64 bytes. It is lightweight enough that a globally decentralized network of independent nodes can verify and store the immutable ledger on basic consumer hardware.
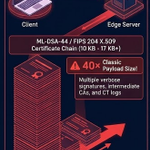
Enter NIST’s finalized PQC standards (such as ML-DSA-87 and Dilithium-5). They do not just slightly increase your data overhead; they produce signatures weighing in at roughly 4,600 bytes. That is a staggering seventy-fold increase in cryptographic fat per transaction.
If you force a 4,600-byte signature directly onto the Bitcoin base layer, you trigger a catastrophic system failure. Block space is strictly finite. A 70x increase in signature size mathematically dictates a massive drop in transaction throughput and drives network fees into the stratosphere. To maintain consensus, running a full node would suddenly require enterprise-grade storage and bandwidth. Decentralization would collapse overnight. The network would effectively be handed over to AWS and a cartel of institutional data centers.
By trying to save cryptocurrency, we would have successfully engineered a mathematically perfect, quantum-secure permissioned database—exactly the traditional financial structure crypto was designed to bypass.
If PQC fails to compress, classical crypto simply dies. There is no plan B.
My Takeaway:
The crypto industry must stop treating PQC integration as a simple software patch. It is a fundamental architectural rewrite. We cannot simply drop ML-DSA-87 onto the blockchain. The only mathematically viable survival path is absolute abstraction. We must push post-quantum authentication off-chain or aggressively wrap PQC signatures in mathematically dense Zero-Knowledge (ZK) proofs (like STARKs) that compress the verification footprint down to bytes before it hits the base layer. The math must evolve, or the hardest money on earth becomes too heavy to lift.
#Bitcoin #QuantumComputing #PQC #G7 #CyberSecurity #Cryptography #Web3 #Decentralization #AsymmetricWarfare

PakCrypt.Org retweeted
There are TWO separate attack vectors for location tracking
****************************
Channel 1: ADINT (commercial ad-tech). It's an intel supply chain.
In Europe your activity+location is broadcast in RTB auctions ∼376 times PER DAY per person. 178 TRILLION exposures per year globally, flowing to brokers in RU/CN with no downstream control
∼80% of Android apps and 79% of iOS apps embed 1+ tracking SDKs [Kollnig 2021]. One dataset: 380M location points traced to 40,000 apps - weather, fitness, games
"Disable ad ID" is NOT anonymization. Location IS the identifier. 4 spatio-temporal points = 95% unique [de Montjoye 2013], 8 points = 99.98%
A soldier/official is worse - presence at a fenced facility is a coordinate lookup, not inference.
This was used to find hotels housing US personnel in Iraqi Kurdistan - data BOUGHT, not hacked.
CENTCOM confirmed to Congress adversaries are using commercial location data for targeting.
******************
Channel 2: Signalling layer (SS7/Diameter).
SS7 is 1970s trust-by-membership: no auth, no encryption, no integrity [ENISA 2018]. An SS7 ping = $20 HLR lookup API (phone number -> IMSI + serving VLR) -> MAP query returns cell/location area. No app. No consent. No trace on the handset. No MDM can block it.
Gulf networks just fought a wave of these pings via roaming access during the Iran conflict.
Lesson: Ad-blockers, DNS, MDM harden Channel 1. They do ZERO for Channel 2. The signalling attack targets the NUMBER, not the handset.

PakCrypt.Org retweeted
PAKCRYPT 2026 is LIVE — The 5th Edition
If you love advanced math, puzzles, and the art of secrets — this is your calling.
What is it?
Pakistan's biggest International Cybersecurity Symposium & Competitions.
24-27 Nov 2026 | NCCS, Air University, Islamabad
4 Days On-Site | 1000+ Participants | 13+ Intl Experts | Rs. 5.0M Total Prizes
In Partnership with IACR — with the IACR Crypto Winter School + International Symposium running in parallel.
2 Tracks, Individual Participation Only:
🌟 Amateur Track: Born after 01 Dec 2006 (Under 20 on 01 Dec 2026) — for the next generation.
🔐 Professional Track: No age limit. Open to all — students, teachers, professionals, researchers.
How it works:
Aug-Sep: Pre-Qualifying + Qualifying Rounds ONLINE
Oct-Nov: Workshops with world experts
24-27 Nov: On-site FINALS in Islamabad — fully sponsored + Networking Dinner + Closing Ceremony[Travel][Food][Accommodation]
Prizes per track:
🥇 Rs. 300K | 🥈 Rs. 200K | 🥉 Rs. 125K — plus every finalist gets full sponsorship.
*****************************
Why should you care?
If a nation wants to truly achieve sovereignty in the information and cyber domain, it MUST excel in cryptography.
Cryptography is the foundational layer of cyber. Firewalls can be bypassed. Networks can be breached. But strong math endures.
In the age of AI, perhaps in the future this will be the ONLY layer that stands between man and machine.
This is not just a competition. It's nation-building.
So send your sons and daughters who stare at numbers and see patterns. Who love number theory, abstract algebra, and solving what others call impossible.
We need elite cryptographers.
Qualifiers are running NOW.
Register & Try the mini-game: pakcrypt.org/pc26
#PakCrypt #PakCrypt2026 #Cryptography #CyberSecurity #Mathematics #IACR #Pakistan #NCCS
PakCrypt.Org retweeted
🔐 2 competition tracks (Pro and Amo)
🏆 Rs. 7M+ total prizes in Crypto Competition, CTF and Ideas Cup
🌍 12+ International experts
🎓 IACR Cryptography Winter School
📍 NCCS, Air University, Islamabad
📅 24–27 Nov 2026
The first round is open online now.
Can you crack it?
👉 pakcrypt.org/pc26
#Cryptography #CyberSecurityPakistan
#CyberSecurity #InfoSec #Cryptography #CyberSecurityPakistan #Encryption
#PQC #Quantum #CyberDefense #DigitalForensics
#EthicalHacking #OSINT #NetworkSecurity
#ApplicationSecurity
PakCrypt.Org retweeted
This whiteboard is HYBRID KEX 🔐 = X25519 + ML-KEM-768 [PQC] = TLS 1.3 Hybrid — IETF Draft 2026. This is NOT theory, this is what Chrome, Cloudflare, Google are shipping RIGHT NOW. Let me explain with the squad:
Meet:
🟣 Xena — X25519 ECDH girl, fast, classic, 255-bit
🔵 Kyber — ML-KEM-768 boy, lattice, quantum-safe
🟡 KDF Funnel — The Mixer DJ who makes the final key
1/ LEFT — Xena X25519: Curve: y² = x³ + 486662x² + x over p = 2²⁵⁵ - 19 [yellow highlight]. Base point G fixed. You do scalar clamping: clear bits 0-2, set bit 254, clear 255. Why? Prevent small subgroup attacks. Shared secret K_ecdh = X25519(sk,pk) = x-coordinate. Uses Montgomery ladder = constant-time = no timing leak. This is what your WhatsApp uses TODAY. Fast, 32 bytes, battle-tested.
2/ RIGHT — Kyber ML-KEM-768: Same as Board 1! t = A·s + e mod q. Encap: sample r,e1,e2, u=A^T·r+e2, v=t^T·r+e2+Decompress(m). Ciphertext (u,v), shared K_kem = KDF(r||H(u,v)). Lattice grid 768 dims. Quantum-safe. If quantum breaks Xena, Kyber still stands.
3/ MIDDLE — THE COMBINER — MOST IMPORTANT PART ON BOARD: K = KDF(K_ecdh || K_kem || transcript) KDF = HKDF-SHA256 or SHA3-256. The board draws a funnel: K_ecdh + K_kem + transcript go in, Hybrid Secret K comes out. CRITICAL RED BOX: Hybrid is NOT XOR. You MUST concatenate then KDF. XOR is broken. Also you must validate peer keys, reject invalid/out-of-range, prevent downgrade, and bind transcript = include ClientHello/ServerHello hash in KDF input.
4/ TLS 1.3 HANDSHAKE FLOW — bottom middle: ClientHello → key_share = [X25519 pk + ML-KEM pk] → ServerHello → key_share = [X25519 pk_srv + ML-KEM ciphertext] → Both derive K_ecdh & K_kem locally → Compute K = KDF(K_ecdh || K_kem || transcript_hash) → Use K to derive handshake keys → encrypt rest of handshake. Simple.
5/ SECURITY = DEFENSE IN DEPTH: If quantum computer breaks Xena X25519 → K_kem still secure [PQC]. If ML-KEM gets broken classically [remember KyberSlash?] → K_ecdh still classically secure. You need to break BOTH to break hybrid. That’s why IETF says hybrid or fail. Also transcript binding stops attacker from tricking you into non-hybrid.
6/ Why Gen Z should care? Your TLS connection today is being harvested: HNDL — Harvest Now Decrypt Later. Attackers store your X25519 handshake now, will decrypt with quantum in 2030. Hybrid stops HNDL TODAY. If you build anything with TLS, you need this board.
TL;DR: Xena is fast but quantum-vulnerable. Kyber is quantum-safe but new. Mix them with KDF, bind transcript, and you get a key that survives even if one breaks. That’s how we migrate the internet without breaking it.
Register to learn more: pc26.pakcrypt.org
#HybridKEX #X25519 #MLKEM #Kyber #TLS13 #IETF #PQC #PostQuantum #KDF #HKDF #ECDH #Curve25519 #PakCrypt2026 #GenZCrypto #CyberSecurity #InfoSec #NISTPQC #QuantumSafe #HNDL

PakCrypt.Org retweeted
Wonderful contribution. Thanks Prof. Grieger :)
****************
A wonderful contribution from PakCrypt Alumni:-
Eyes on the screen, shadows on the wall
When the world sleeps, we hear the system call
Zero days and infinite lines of code
On this digital road, we abide by no mode
Packet inspection, no trace of detection
I build up the wall for the ultimate section
They try to breach, but the firewalls reach
Where no amateur hacker can ever impeach
I rewrite the script and the matrix is flipped
With advanced encryption, my spirit is shipped
No backdoors allowed in the cloud of the proud
I stand with the few and I speak to the crowd
They want our data, they want our sovereign state
But they can't calculate our algorithmic fate
I'm a guardian of bytes fighting late through the nights
Taking power back and claiming our rights
The terminal blinks as the syndicate sinks
We are severing all of their malicious links
This is our system
This is our grid
We fight for the freedom they tried to forbid
Lockdown secure
No entry, no choice
We are the sovereigns of this digital space
They brought their rootkits and phishing attacks
But they never accounted for my counter tracks
I isolated the virus, contained the disease
And I brought that darknet network right to its knees
Our infrastructure is built like a fort on a hill
Executed with absolute digital skill
From the soil to the fiber, the lineage is pure
And this digital empire will forever endure
We don't bow to the giants of corporate greed
We're a different breed with a different need
My farm is the server, the harvester is code
And I'm bearing the weight of this heavy-duty load
A warrior's heart in a developer's mind
Leaving all of their obsolete systems behind
The breach was attempted but swiftly denied
With a sense of immense and unshakeable pride
This is our system
This is our grid
We fight for the freedom they tried to forbid
Lockdown secure
No entry, no choice
We are the sovereigns of this digital space
The firewalls hold
The data is ours
They had their tech, but we had the power
PakCrypt.Org retweeted
📱 "Nobody needs to hack your phone." Here is why:
We often picture digital surveillance as zero-day exploits or covert intruders. The reality is far simpler—and completely commercialized.
Every day, ordinary mobile apps produce a steady stream of routine data: location coordinates, timestamped requests, and your device’s Advertising ID. Individually, these records look harmless. Stacked over weeks, they construct a precise "pattern of life"—revealing where you sleep, where you work, who you meet, and when your routine changes.
In a deep-dive analysis by PakCrypt, authors Sara Malik and Naveed A. Aun break down the mechanics of modern mobile tracking:
🔹 The Real-Time Bidding (RTB) Auction: When an app displays an ad, an auction runs in ~0.1 seconds. Your location and device context are broadcast to dozens of potential buyers. Even bidders who lose the auction retain copies of your data.
🔹 The "Anonymity" Fallacy: Data brokers claim location data is "anonymous" because it lacks your name. However, human routines are unique identifiers—an overnight location cross-referenced with public records instantly identifies the user.
🔹 A Serious Security Problem: This isn't just about targeted ads. Commercial location data feeds are accessible to anyone with a purchase order. In 2026, US military branches disabled advertising IDs on government devices after personnel were tracked and targeted abroad using commercially bought broker feeds.
🔹 The Microphone Myth: Your phone doesn't need to secretly record your conversations to serve targeted ads. The real, documented ad-tech pipeline is far more efficient, continuous, and entirely legal.
Understanding how ad exchanges and data brokers operate is the first step toward understanding modern digital privacy risks.
📖 Read the full deep-dive on PakCrypt: pakcrypt.org/articles/tracki…
#DataPrivacy #CyberSecurity #AdTech #InfoSec #MobileSecurity #DataBrokers #DigitalPrivacy #PakCrypt #Privacy Matters

PakCrypt.Org retweeted
I initially just participated in Round 1 along with my friends causally. Luckily ended up in Finals in Islamad in 2024. Air University fully sponsored my travel, lodging, and lunch / dinner. Although I did not won the cup, but PakCrypt generously gave me Rs. 30K to cover my travel. This is so great. Noble cause. If I can do it from here, anyone can. Highly recommended for youngsters. This year, I am sending my two nieces to it. Great crypto community.
— Razaullah - Gujrat, 2024
*************
Register for 2026 event
pc26.pakcrypt.org

PakCrypt.Org retweeted
The PakCrypt Professional Track has no age limit and no gatekeeping.
Faculty, engineers, MS/PhD students, self-taught researchers — if you know cryptography, the track is open.
You compete as an individual. Merit only.
pc26.pakcrypt.org
#Islamabad #Karachi #Lahore #Cybersecurity


PakCrypt.Org retweeted
The future of trust is being built in Islamabad.
PakCrypt 2026 — 5th edition, 1000+ minds, 10 world-class experts in Crypto, PQC & AI x Security. 24-27 Nov @ NCCS, Air University.
Join: PakCrypt.org/pc26 #PakCrypt

PakCrypt.Org retweeted
🚨 Round 1 is LIVE. PakCrypt 2026's national cryptography competition just opened — Rs. 5-6M in prizes, zero entry fee, one shot at Islamabad this Nov. Students + pros, this is your sign. 🔐 Register → pc26.pakcrypt.org #PakCrypt2026 #Crypto #CyberSecurity #Pakistan

PakCrypt.Org retweeted
In partnership with IACR iacr.org
PC26 hosts IACR Crypto Winter School + Intl Cyber Security Symposium.
4 days: hands-on workshops, keynotes, 10-min PhD pitches & direct Q&A with legends.
PakCrypt.org/pc26

PakCrypt.Org retweeted
The 5th edition of Pakcrypt is HERE! Hosted by NCCS & Air University, Pakistan, bringing together the best minds in Cybersecurity & Crypto
✨ Keynotes from global experts
🏆 High-stakes competitions & prizes
🚀 Unmatched networking & career
pakcrypt.org/pc26

PakCrypt.Org retweeted
How to Think in Qubits — a quantum computing primer for cryptographers and mathematicians:
pakcrypt.org/articles/qubits…

PakCrypt.Org retweeted
Pre-reg for 5th PakCrypt 2026 is now open — bringing together professionals to solve cutting-edge challenges in crypto, security, and mathematics.
🌐 Apply now: pakcrypt.org/pc26
#PakCrypt #CyberSecurity #Cryptography #InfoSec #PakistanTech #CTF #STEM
PakCrypt.Org retweeted
PakCrypt especially encourages students of schools and universities to participate in Amateur Track.
Limited Seats -> Register Today
pakcrypt.org
#Pakistan #Islamabad #Air #CTF #Crypto #Maths #code #Students
🤖 Made with AI