

Comms @a16zfrontier | Upstate Born & Raised | Mets, Bills, & Country Music
Joined March 2009
- Tweets10.5K
- Following5K
- Followers2.8K
- Likes13.3K


Paul Cafiero retweeted

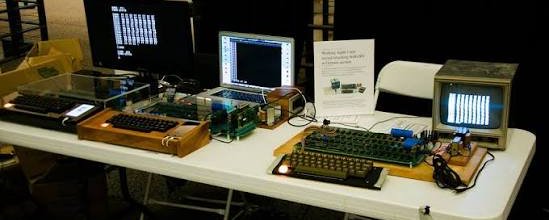
What the smartest people do on the weekend is what everyone else will do during the week in.... how many years now? what things?



Come work with us, plz

I am hiring a social media lead for a16z Frontier!! “We’re lucky enough to be living through one of the most consequential curves in human history today” — THIS is the time, come work with us now! ⚡️🔑🔭💥🗺️
a16z.com/about/jobs/?gh_jid=…

New Frontier, same compliance disclosures. Let's go.

Not an offer or solicitation. None of the information herein should be taken as investment advice; some of the companies mentioned are portfolio companies of a16z. Please see a16z.com/disclosures for more information. A list of investments made by a16z is available at a16z.com/portfolio.

Paul Cafiero retweeted
“The next big thing will start out looking like a toy.” -Chris Dixon, 2010
Chris is an OG American Dynamism investor. An OG VR investor. An OG robotics investor. The OG crypto investor.
Finally, an OG Fund, only for originals.


Paul Cafiero retweeted

Today, a16z Crypto is becoming a16z Frontier.
Since joining a16z in 2013, @cdixon has focused on technologies that look futuristic well before they reach the mainstream. Those themes led to investments in Oculus, Skydio, Zipline, Coinbase, Solana, and Uniswap.
Frontier expands that mandate beyond crypto to back "outer planet" founders who are building new technologies and creating markets that may take years to develop.
Chris joins @pmarca, @bhorowitz, and @eriktorenberg to discuss why crypto has become part of the broader tech landscape, why Frontier fills a hole in the firm's architecture, and why they'd rather be too early than too late.
They also get into why the gap between AI-native startups and incumbents is the widest Marc has ever seen, how AI could pull forward 20 years of frontier technology, why stablecoins may become the way AI agents pay each other, how AI is breaking the internet's business model, and why today's 18-year-olds are about to become superhumans.
0:50 Introducing a16z Frontier
2:49 Smartphone parts to drones and VR
4:47 Backing the "outer planets"
7:11 Good ideas that look like bad ideas
10:43 The JP Morgan photo in Marc's office
15:13 Good tech ideas eventually work
16:53 AI may pull tech 20 years forward
18:18 The widest AI gap Marc's ever seen
22:06 Workers adopt AI before companies do
26:32 Old use cases vs. AI-native ones
30:08 Beyond "product manager brain"
34:45 AI can reverse engineer any hardware
38:23 The case for open source AI
46:36 How AI breaks the internet's model
49:11 VR, homebrew hacking, multiplayer AI
54:00 If you're 18, study "modern alchemy"
YouTube: youtu.be/-9XQMHhpypc
Not an offer or solicitation. None of the information herein should be taken as investment advice; Some of the companies mentioned are portfolio companies of a16z. Please see a16z.com/disclosures for more information. A list of investments made by a16z is available at a16z.com/portfolio.
Paul Cafiero retweeted

The SEC's initial proposal for Reg Crypto Assets was an important first step towards creating a clear fundraising pathway for builders of blockchain networks.
Yesterday, @a16zcrypto submitted recommendations to make that pathway more useful and durable.


Paul Cafiero retweeted

The @USOCC released its final rule implementing the GENIUS Act requirements for payment stablecoin issuers under its purview. Thank you to @USComptroller Gould and the OCC for their leadership in advancing GENIUS implementation.
CCI appreciates that the OCC carefully considered public comments, including ours. The final rule follows the language of the GENIUS Act by eliminating the rebuttable presumption regarding rewards arrangements between issuers and affiliates or third parties. CCI looks forward to reviewing the final rule more closely.

At the @USOCC, we have worked diligently and expeditiously to deliver the GENIUS Act final rule ahead of schedule to support President Trump's vision and @SecScottBessent's leadership to grow the economy and lead the global digital currency revolution.
Today marks the birth of a new industry having a federal framework for payment stablecoins in the digital age. It also brings us back to our original mission when the OCC was charged with the responsibility for organizing and administering a system of nationally chartered banks and a uniform national currency.
Paul Cafiero retweeted

A few reflections on the lattice vs. hash-only debate that our recent Aerie post sparked:
1. Cryptographic ossification for blockchains was never safe. Until the day we know with certainty that P ≠ NP, that finding short vectors in lattices is intractable, that Keccak effectively behaves like a random oracle in deployed SNARKs, and that every single bug has been eliminated from our codebases, blockchains cannot ossify. That is simply not how safe systems are built. Issues will arise, and the system will have to respond.
It’s a double standard to reject lattices because blockchains are hard to upgrade if lattices break, while counting on upgrades if AI breaks your hash function or finds a critical zkVM bug.
The best counterargument is that hash-only designs are more agile: if your hash function breaks, just swap out the hash. But we must aspire to a higher level of agility than this. Indeed, as I cover next, if SNARK recursion itself turns out to degrade security, the proposed hash-only blockchain designs would need to be rethought from the ground up.
2. The real security debate is not lattices vs. hashes — it is lattices vs. building everything on SNARK recursion. That’s because “hash-only” is not really hash-only: it rests on hashes plus the soundness of deep SNARK recursion. Ethereum’s roadmap relies on exactly that: hash-based aggregation needs recursion to keep up with a slot’s worth of signatures, and EIP-8288 would send other signature schemes and users’ own proofs through the same recursive pipeline. In contrast, Aerie proves a slot’s worth of signatures on one laptop without any recursion.
All deployed post-quantum SNARKs rely on the Random Oracle Methodology (via Fiat–Shamir) to establish their security. This is an idealization we know fails in the real world: we have explicit counterexamples where “SNARKs” coming out of this methodology are totally insecure when instantiated with any concrete hash function.
We generally ignore these counterexamples in part because they only arise when proving contrived, self-referential statements about the very hash function used by the SNARK verifier.
But proving statements about the verifier’s own hash function is the exact thing you do in SNARK recursion. That’s why the security of recursive SNARKs can’t be established even in the random oracle model.
On top of that, the standard security proofs for recursion (in other models) suffer an “extractor runtime” blowup that is exponential in the recursion depth, suggesting that security may degrade as more recursion is applied. Yet Ethereum’s own EIP-8288 enables unlimited-depth recursion, even as it lists soundness of recursive SNARKs as a trust assumption. Proofs in more idealized models avoid the blowup, but they mainly tell us that an attack on SNARK recursion would have to exploit the concrete hash function, which is exactly what the Fiat–Shamir attacks above do.
To be clear, we don’t know of any outright attacks on SNARK recursion, and I very much hope it is secure. But some of us who have studied the question have a lingering sense that an attack may be possible in some settings. And if AI is going to supercharge cryptanalysis, there is no reason to expect it to spare Fiat–Shamir for SNARKs, let alone SNARK recursion, both of which have had far less scrutiny than lattices.
So, I do not concede that a “recursion everywhere” hash-only approach is clearly more conservative than one built on standard lattice assumptions.
3. “Just wrap everything in a hash-based SNARK” (like EIP-8288) faces challenges.
Aggregating signatures and proofs off-chain into a single block-level proof is a powerful design independent of the hash-only vs. lattice debate, and I am not telling people to avoid it. But claiming, as Vitalik Buterin did this week, that users can run whatever cryptography they want locally and wrap it in a client-side leanVM proof glosses over major hurdles.
For example, leanVM today is a minimal VM designed almost entirely to prove hash-based signatures and recursion, not general-purpose computation. And binary-field SNARKs like leanVM remain slow at proving the integer multiplications that lattice cryptography does en masse.
I am optimistic that many of these zkVM challenges can be met (including via my own work, binary-field Twist and Shout, which are now implemented in Magnetar). But regardless, if lattices can make aggregation simpler and faster, then they should be leveraged. We need to be agile no matter what.
4. For chains whose reason for existence is privacy, I truly struggle to understand the pushback. Public-key encryption (and fast single-server PIR) cannot be built from hashes alone, at least not in any black-box way. If lattices break, it is going to be very, very hard for these chains to provide acceptable levels of privacy and functionality. For a project whose entire reason for existence is privacy, a loss of confidentiality is an existential failure. Next to that, a second signature upgrade (after the first one, from elliptic curves alone to, hopefully, a hybrid lattice scheme) is easy.
Summary: We don’t know for sure what is secure and what isn’t. We are all weighing unquantifiable risks against each other, and we do not need to agree on a total order on them. But hash-only solutions face many open engineering challenges, and they are not more “conservative” in the way some have argued. Some of those challenges are entirely prosaic and have nothing to do with bugs or cryptography, like hardware support for custom schemes whose hash function is still undecided. I hope we can overcome those challenges within the appropriate timelines, but they must be acknowledged and portrayed realistically.
Overall, cryptographic agility and defense in depth (e.g., hybrid signatures) are the answer, which is why we are building both lattice-Jolt and hash-Jolt. In practice, the positions are less polarized than social media discourse suggests: for example, StarkWare is working to make Falcon verification cheap (falcon.provably.fast/), which is great to see.
Here is the (apparently) controversial take I am sticking to: Conditioned on agility, whenever lattices make systems simpler or more functional, we should embrace them rather than default to “hash-only” designs. Lattices are what the rest of the world will depend on, with decades of study and hardening behind them, and at the system level, less functional often means less secure. Where hash-only designs are just as simple and functional, by all means use them.

Paul Cafiero retweeted

In MSG ...minutes before the banner unveiling... not sure I've seen more hardened New Yorkers just smiling ear to ear in one place at the same time. Men, women, kids, adults. Not sure how long it'll last (1 minute into the game?), but quite a joyous scene at the Garden.


Paul Cafiero retweeted

“Openness and transparency are the real keys to AI safety. Open weights let you look under the hood of a model. Auditable training goes even further by letting anyone with a laptop verify everything that happened during the model’s training run. Really exciting work from @benfielding and the @gensynai team."

Gensyn CEO @benfielding warns that AI agents auditing other AI agents can be compromised too:
"We create swarms of AI agents that can do far more work than any human could. A human can’t follow along and check everything. One of the big counters is to say that agents can do the verification."
"But METR says those agents themselves can become corrupted by the training process, and you can’t trust any agent that’s auditing another agent. If you’ve trained a model in an auditable way, you can trust it."
"Any claim where the model is hiding its chain of thought falls away, because you have an exact log of everything that’s happened, and you can rerun every single step on any device."
"For national security, finance, pharma, health, insurance, it’s essential that they have models like these. If a regulator wanted to audit, they wouldn’t have to go off promises of the company."
@gensynai
Paul Cafiero retweeted

Enjoyed chatting with Guy and Brian -
A reminder that if you are doing interesting or weird (or both) stuff between tradfi and defi, come talk to me!


Great panel with @brian__foster and @MuyaoShen at @money2020.
It’s about bringing finance onto the internet. A lot of finance still runs on Excel spreadsheets, and it’s no longer about tradfi or DeFi, it’s about making finance move at the speed of the internet.
On the crypto side we have to update the words we use to meet traditional finance where they are. DeFi and decentralization doesn’t mean a ton yet but reducing counter party risk does.
It was great to be onstage at Money2020 to help that translation process.

Paul Cafiero retweeted

Great panel with @brian__foster and @MuyaoShen at @money2020.
It’s about bringing finance onto the internet. A lot of finance still runs on Excel spreadsheets, and it’s no longer about tradfi or DeFi, it’s about making finance move at the speed of the internet.
On the crypto side we have to update the words we use to meet traditional finance where they are. DeFi and decentralization doesn’t mean a ton yet but reducing counter party risk does.
It was great to be onstage at Money2020 to help that translation process.