

Security Researcher || Smart contract Security Instructor @GuildAcademy_ @Web3Bridge @Blockheaderweb3 || 50+ audits & over 70 H/M found || https://xitter.cf/t.co/7ojMfMpYX2
EVM
Joined April 2023
- Tweets2.2K
- Following1.1K
- Followers1.5K
- Likes5.5K



Pinned Tweet
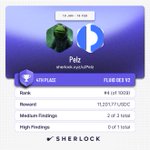
Happy to announce that i came top 4 amongst 1000+ researchers. Can’t lie, this was a tough contest on @sherlockdefi and a lot of battles had to be won but above all i’m glad i came out on top.
More wins incoming!!!
Expect a lot more from me this year..i’m all in..

Pelz 🕵🏾♂️ retweeted

I was able to save a protocol $9.8m at risk.
- all exploit details, full e2e, & acknowledged by team.
An unprivileged attack that’d cost an attacker just $1-5 causing loss of +114btc and an halt.
- Reach out if you want a review on your codebase 🫡
gist.github.com/blessingbloc…

Pelz 🕵🏾♂️ retweeted

Quick thoughts on the events I missed over the past two months:
- The XRP bug is a great finding, but the reward was low. But even Ethereum had a $250k max bounty a few months ago, so I wouldn’t criticize Ripple too hard.
- The max cap wasn’t specified in the XRP bounty program, so most hunters didn’t even bother checking it.
- The $50k Vercel bounty is too low. They advertised a $1 million bounty, which is misleading, since there's a $50k max cap. Are they expecting 20 Criticals?
- Other projects continue lowering their bounties or closing programs while hacks increase. I understand that it hurts to pay so many reports, but there’s no coming back from a hack.
- The “Duplicates” problem hasn’t been solved. You can still report a Critical issue, prevent major damage to a project and its users, and they will still try to find a way to pay you nothing while pointing to some non-impactful report as sharing the same root cause. Platforms should address this scam immediately.
- The LLM decompilation movement is pretty cool. It's the end of the era of closed-source code.
- People building security tools that depend on LLM tokens should try to make a profit today, or have a clear plan to sell their company before models get better. There's no long-term plan.
- LLM spam continues to be the main trend for getting bounty rewards. It feels like buying lottery tickets. The more tokens people spend, the more chances they have of landing an actual exploit. Having a unique approach seems to help too. But nobody is performing much better than the model they use, since there's no clear outstanding winner in the leaderboards.
- We’re getting to the end of 2026, and bounty rewards paid haven’t increased 10x with AI. According to Grok, for the top 100 on Immunefi the total earnings were:
* 2026 $16M, 1364 reports
* 2025 $11M, 820 reports
* 2024 $21M, 775 reports
* 2023 $17M , 559 reports
* 2022 $57M, 443 reports
- What happened with Ledger is worrisome. Keep improving your OpSec, whitehats.
Personal thoughts:
We keep seeing more and more bugs in all kind of software. That's not because of superhuman AI capabilities. It's because how bad we've been building software over decades in terms of security.
Nobody cared about exploits because they were difficult for the average hackers. Now everyone has a low-level-IQ tool that can crack neglected code, and we see the results.
We're in a transition phase, where LLMs trained with human bugs are outperforming the average guys. We'll probably get to an era of LLMs-code-first, with LLM bugs that with unprecedented vulnerabilities.
Yes, LLMs are just that bad at coding, and the current models might not be able to see some obvious errors, since they also have "cognition bias".
I see a bright future for bounty hunters, full of vulnerabilities waiting to be found and prevented. We just need to solve the bug-pocalypse first if we don’t want blackhats to win.
Pelz 🕵🏾♂️ retweeted

Seeing researchers worried about losing access to their locked Sherlock rewards, we’d like to offer a practical way forward.
@HackenProof is ready to handle KYC and payouts for all affected researchers, with zero fees for researchers or Sherlock.
If maintaining the old balances and processing payouts is an operational burden, we can take that on. Sherlock would need to agree to release the rewards, provide the list of affected researchers and their balances, and transfer the corresponding funds to us.
Researchers would receive their full balances without having to enter new contests to unlock them.
Happy to coordinate with @sherlockdefi team and make this happen.
Pelz 🕵🏾♂️ retweeted

@sherlockdefi announced yesterday that it will deprecate its Contents model and replace it with the Audit engine module, which they consider better.
The problem comes with the condition that Sherlock sets, which is that you need to have a validity score >= 20% as well as two valid issues to receive payouts.
In my opinion, this is unfair to SRs, and here is why I see it as unfair.
1- Sherlock in most of its contests, doesn't accept low issues, so the validity score itself is not accurate, valid Low issues are treated as invalid, even issues that was accepted as Medium/High and after long escalation war it gets downgraded to low.
2- A lot of contests end with invalidating an issue because of unclear docs, unclear scope and out-of-scope files. Issues get accepted, and then the Judger can make it out of scope; the Developer can mention that this is intended behaviour managed by off-chain systems. So new inputs coming after the contest finishes invalidate findings, which affects SRs validity threshold. I have examples for these situations.
3- A lot of recent contests were invite-only contests, picking only the top. So the new SRs didn't even have the chance to participate in these contests.
Because of these points, I see it is unfair to prevent paying SRs.
These are the points that make the system itself can't sustain this condition.
This is the decision compared to the system; I haven't talked about the morality of the decision itself, and how you dare to take another person's money.
- Some people may have left the space.
- Some can get into full-time positions and have no time.
- Others may need that money.
The 120-day period will not solve the problem; you don't know who still depends on contests and who does not, who left the space and who still, a lot of conditions, and this solution will not solve many of them.
I can't imagine how to have a clear conscience, and you are taking others' money.
The crash out by SRs on @sherlockdefi is crazy due to the recent announcements, i know how much i’ve had to fight for issues cause they always tried downgrading so how does one get to maintain their ratio if they keep getting downgraded!!!
Pelz 🕵🏾♂️ retweeted
Happy to announce that i came top 4 amongst 1000+ researchers. Can’t lie, this was a tough contest on @sherlockdefi and a lot of battles had to be won but above all i’m glad i came out on top.
More wins incoming!!!
Expect a lot more from me this year..i’m all in..
Pelz 🕵🏾♂️ retweeted
sneaked into top 10 haha..😏

Glider Contest final leaderboard.
🥇 @ChaseTheLight99
🥈 @0xodus
🥉 @0xK42
Congrats, and thanks to everyone who submitted queries.
sneaked into top 10 haha..😏
Glider Contest final leaderboard.
🥇 @ChaseTheLight99
🥈 @0xodus
🥉 @0xK42
Congrats, and thanks to everyone who submitted queries.

Pelz 🕵🏾♂️ retweeted

Here are the results of the @raincards Audit Contest!
1. @gjaldon - $9,532 🥇
2. @0xpiramide - $2,194 🥈
3. @Pelz_Dev - $2,098 🥉
$27,500 in rewards, bringing Sherlock's total researcher payouts to $21.0M+.
Link below for the full results 👇
Bug bounties aren’t easy mehn, i chased down a path for approx 2 days straight, it turned out to be a bug quite alright..but guess what?
upon submission i discovered its out of scope… :(
what to do when no response for crits for about 2 months now..
This is why black hats always have an edge against us white hats..our wings keep getting clipped… :(


I don’t know what to do anymore.. every bug i get is closed as a duplicate no matter how sophisticated i think it is..where are the bugs in bbp this dry spell is getting too much…i’d probably be dead by the time i get a valid bounty :(

Pelz 🕵🏾♂️ retweeted

All we do is find bugs.
It’s what we’re built for, what we’re obsessed with, and what we’ve done every single day for years.
We don’t write code. We don’t chase hype.
We hunt vulnerabilities and we’re damn good at it.
Pelz 🕵🏾♂️ retweeted

Making a billion dollar app with Cygent and Claude xitter.cf/i/broadcasts/1yxBeeQLO…

Join us !
How to actually earn $ as a web3 security researcher in 2026 xitter.cf/i/broadcasts/1NGarrMVn…
