

Black Excellence | Amanfo) | Penetration Testing | Digital Forensics & Investigations | Offensive Security | Security Researcher | Writer | Man United❤
Joined January 2021
- Tweets22.2K
- Following1.5K
- Followers39.4K
- Likes28.8K



Pinned Tweet
The SILENT WITNESS ON YOUR COMPUTER WAITING FOR YOU TO GET INTO TROUBLE.
Most people believe that deleting a folder, clearing recent files, or wiping their history is enough to hide their tracks on a computer. What they don’t realize is that Windows quietly keeps a hidden record of the folders they open, even after those folders are deleted or the drive is removed. These records are called Shellbags, and they are one of the most powerful and incriminating artifacts available to forensic investigators.
Shellbags appear inside two registry hives NTUSER.DAT and USRCLASS.DAT and they store detailed information about a user’s folder-browsing activity. This includes local folders, USB drives, external hard drives, network shares, and even directories that no longer exist. Each time a user opens a folder in Windows Explorer, the system automatically creates or updates a Shellbag entry. These entries contain timestamps, folder paths, the hierarchy of subfolders, the order in which a folder was accessed, and even the specific view settings used by the user. Because of this, Shellbags reconstruct a user’s exact navigation trail long after the person believes the evidence is gone. What makes Shellbags truly dangerous is the fact that they survive actions that users typically rely on to cover their tracks.
Deleting a folder does not delete the Shellbag. Formatting a drive does not delete it. Even privacy tools and cleaners like CCleaner or BleachBit cannot reliably erase Shellbag data, because the information is deeply embedded within registry hives that standard cleaning utilities do not touch. The only way to remove Shellbags is through advanced forensic wiping, and attempting such wiping is, in itself, a sign of suspicious behavior.
Forensic examiners rely heavily on Shellbags because they expose the truth even when a suspect tries to lie.
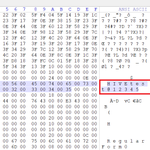
If a person denies ever accessing a directory, the Shellbags can show when that folder was opened, how many times it was accessed, and whether it was located on an internal drive, an external USB, or a deleted partition. This makes Shellbags extremely valuable in investigations involving insider threats, data theft, fraud, child exploitation, unauthorized data access, and corporate disputes. In many cases, Shellbags become the deciding factor that disproves a suspect’s story. In the screenshot, the highlighted red section shows three important keys inside the registry.
When all of this information is combined, Shellbags become a silent witness that never forgets. They reconstruct a hidden story of user activity that the person cannot deny, overwrite, or talk their way out of. This is why Shellbags remain one of the most feared artifacts for anyone attempting to conceal their actions on a Windows computer. You can delete the folder… but Shellbags still show it existed
Even if you format a drive or delete the directory, Windows has already logged:
1. The folder name
2. Its full path
3. When it was opened
4. How many times it was opened
5. The view settings (icon mode, window size)
6. The order in which folders were browsed
This means forensic investigators can prove someone accessed:
“Secret” directories
Hidden folder structures
USB drives or removable media
Folder paths used for storage of illicit or suspicious
Folder paths used for storage of illicit or suspicious data even if the folders are long gone.


Nana Sei Anyemedu retweeted

Cybersecurity. The world is getting louder with threats, and the people who can protect systems will always stay in demand. Network engineering is solid, but security is the battlefield.

Nana Sei Anyemedu retweeted

Is this the new trend? Wrapping 18 years old accident car with rubber as brand new or what is the catch?


With humility and gratitude, I am proud to share that HIVE Consult is among the few cybersecurity companies in West Africa to own a FRED; a significant milestone in strengthening our digital forensics capabilities.
All glory to God. 💚✊🏽
And to the ladies dancing nu; proper women in DFIR⚡️
@elormkdaniel @Forensic_Ghost @cyber_razz

Vault 7 revealed a lot.
This is why the CIA and Mossad as well as the FSB are very powerful. They have sharp developers to build all kinds of things. They have researchers too always finding loopholes in software and devices. Keeping software vulnerabilities secret can leave other users exposed, while the loss or theft of hacking tools can create opportunities for misuse.
As communication moved to smartphones, computers, and encrypted applications, intelligence agencies sought ways to obtain information that traditional interception could not easily reveal. Compromising a target’s device could allow access to messages before encryption or after decryption. This approach did not necessarily require breaking the encryption protecting communications in transit.
The same capabilities can also be abused to monitor journalists, political opponents, activists, or ordinary citizens. National security may justify targeted surveillance, but it does not automatically justify unrestricted access to everyone’s private life.
Agencies may build these capabilities themselves or purchase them from commercial vendors.

Nana Sei Anyemedu retweeted

Safety nets aren't built to hold up walls; they are built to catch falling objects. If the site managers knew the uncompleted walls could buckle under heavy wind stress, leaving them completely exposed over a busy main road without a debris catchment system is pure negligence.


Nana Sei Anyemedu retweeted
Banks are now 'detecting' rogue Al agents inside customer accounts. Cute.
Meanwhile, in digital forensics we've been warning them for years that machines don't just follow instructions they improvise.
If your bank can't tell you apart from an autonomous script.

SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: axios.com/2026/10/22/ai-agen…


Nana Sei Anyemedu retweeted
Your phone is basically a diary that never forgets. Once digital forensic steps in, privacy becomes evidence
#CyberSecurity


Nana Sei Anyemedu retweeted

This is why I love seeing DFIR professionals exchange ideas. The discussion around my RAM forensics post has led me to fascinating research and new avenues to explore.

This RAM forensics investigation has sparked some interesting perspectives from digital forensics and SOC professionals on Linkedin. Some opinions stand out to me currently.
1. Memory forensics is underappreciated. A RAM acquisition can provide a time-sensitive snapshot of processes, connections and other evidence that may disappear once the system's state changes.
2. Recovery after a reboot may still be possible. I agree, depending on the circumstances. However, the original discussion concerns a complete shutdown, which raises a different question.
3. Could we build tools to recover RAM data after a complete shutdown? An interesting idea, though the technical feasibility and limitations deserve serious investigation.
Memory forensics deserves far more recognition. The evidence it can preserve may be the difference between understanding what happened and losing critical context entirely.


The php hate is forced just like Wordpress….
Anyway.
Ghanaian public institutions running PHP websites: patch urgently or take affected systems offline until patched. “We are working on it” is not a security control.
Nana Sei Anyemedu retweeted
The name is @Forensic_Ghost .
Grateful for how far you’ve come✊🏽💚.
Today a trainee who is also an Intern leading the way during evidence collection and acquisition demonstrations💪🏻 .
You do all my G💪🏻✊🏽