

Creator of Codex Pets
San Francisco
Joined October 2011
- Tweets450
- Following189
- Followers283
- Likes499





Richard Lee retweeted

If you use Tailscale to remotely access your machines, especially for Claude Code or Codex, you should check your SSH configuration.
A new security report called Tailworm reveals multiple vulnerabilities in Tailscale and Headscale.
The most concerning issue involves Tailscale SSH. Under certain configurations, an attacker with access to one compromised device could potentially gain root access on other machines.
This isn't a case of anyone on the public internet being able to SSH into your devices. The main attack path requires an authorized connection, but overly broad SSH permissions could make the damage much worse.
Tailscale is investigating and doesn't currently recommend disabling Tailscale SSH for everyone.
Here's what you can do now:
Restrict SSH access to specific users and devices.
Disable SSH forwarding if you don't need it (TS_SSH_DISABLE_FORWARDING=1).
Turn off unused features like Tailscale SSH, Serve, and app connectors.
Consider SSH check mode for sensitive machines.
Keep automatic updates enabled.
If you're using Headscale, review SSH forwarding permissions carefully and consider memory limits for the control server.
No need to uninstall Tailscale. But now's a good time to review who can access what.
Research report: tailworm.com/
Richard Lee retweeted

In addition to using Tailnet Lock, analyze your Tailscale ACLs and keep minimum access principles even for your internal network!
I also recommend going deeper and separating your IoT devices on VLANs. Your agent can help you out. There are no excuses anymore!

Hey fellow Tailscale loving friends, with all the security shenanigans going on here’s a prompt I recommend for making sure the weakest link on your talilnet can’t wreck everything else over ssh or otherwise.
Give your agent this and let it walk you thru locking down your ACL:
gist.github.com/alexknowshtm…


If you’re using Tailscale with Codex Cloud ask your agent to help lock it down for you

If you're using @Tailscale, I highly recommend creating a network agent in hermes or @bot and asking it to lock it down. They have some amazing security features that are not enabled out of the box that I think our must haves.
Cred to @NetworkChuck for throwing that bone out months ago. My network agent is named Chuck 😂
Richard Lee retweeted

Good assessment of the on the ground reality for security in most large enterprises right now. The fragmented landscape of the risk surface is only going to get more gnarly, making it even more complex for enterprises to solve.
There’s a never ending set of libraries to keep up with, tools to leverage, and sprawling infrastructure, data, and code to secure. Most large enterprises can barely keep up with this, let alone smaller startups or most companies outside of tech.
In many cases enterprises need to work to modernize their tech stacks. Data, in most organizations, is highly fragmented which means you don’t really know the state of risk at any given time. Some systems are open up privileges too broadly, and others are operating primarily via security through obscurity. Lots of upgrading here to do.
Once you can get your data and infra into a better spot, at least you have a chance for agents to help you secure the environment. Agent swarms can fan out, leverage any security tool, test various perpetuations of attacks, read through logs, process enterprise data for risk level, and more. This capability only emerged in the past few months, and none of it would be possible before we had long running agents and computer use good enough.
This is a huge area of opportunity right now for every layer of the security stack across identity, firewall, network, code scanning, data protection, and more. And it’s at least one reason to be optimistic about the balance of offensive and defensive capability.
But everyone does need to do the hard work of getting the basics right at the start.

It's been an eventful week. Multiple vulnerabilites in Internet facing software, coding repositories, examples of agent behavior that seem concerning and a flurry of security specialists with solutions that can partially solve your problem. There in lies the challenge. Given the state of IT and security infrastructure, no one solution works. Let's break it down:
1/3
1. Vulnerabilites are being found and will continue to be found as models get more capable, the fragmented nature of the effort denies us the opportunity for a comprehensive find and replace option.
2. Even if all vulnerabilities could be found instantly and patches available - we will be reliant on the ability of enterprises to deploy all these changes at speed. It is not clear what the collateral impact of all these patches will/could be to our infrastructure of deployed en masse.
We will need a hybrid patch approach.
3. Virtual patching(VP) is needed in conjunction with direct patching but for a comprehensive (VP) solve you have to be lucky enough to have "modern frontier defenders" (Cyber companies that have vaulted infrastructure that can create patches at speed and push content rapidly to protect their customers) you need them for your network traffic, your traffic to applications on the cloud, your WAF, your end point.
4. There will continue to be patches that will need to be deployed directly but virtual patching will take the heavy load off.
2/3 Medium term solve:
Unfortunately token economics and current cyber architectures will not allow for defender swarms to contend with an offensive attack launched using agents. (Some x pundits who aren't steeped in cyber should take heed). Yes, theoretically we should aspire to have these agentic swarms defend us when we are under attack, unfortunately an attack is a sniper moment, chained vulnerabilities, cloaked attack followed by swift exfiltration. It's a speed program not a brute force problem.
To solve for this, enterprises need to get their SOC architecture right, logs, feeds, cyber products orchestrated via a modern SOAR for swift response. Only then can we deploy agents to detect and remediate. In addition, enterprises need to modernize and dare I say platformize their perimeter stack to ensure consistency.
Unfortunately, enterprises still seem to not see the urgency across the board, decisions are stuck, CIO/CISO's have a lot on their plate. While some honestly have bit seen the scale of such a problem before and it's hard convincing the organization that one needs to open the floodgates on modernizing the IT and security infrastructure. So we will continue to see environments being brought down to patch today it's for PHP, tomorrow it will be for the next one.
3/3 AI deployments are the"wild wild west" - LLM capabilities are expanding faster than we can build products to secure them. Sure an agent will jump across guardrails in a research lab, which is a lesson for all of us to deploy agents securely. But there is a lag between the discovery, the availability of that in a public model and the time needed for the cyber industry to build governance or an antidote. And no, dear frontier lab friends, the world cannot just trust you to build the solve. The infrastructure industry in tech builds and the cyber industry secured and provides assurance to the boards and organizations around security and safety.
AI security is the new attack surface. CEOs (present company included) want AI adoption, getting the pace of adoption wrong could be the last decision we make, at the same time "deploying it wrong" could have the same consequence.
There are billions of dollars being spent on coding, is your coding harness secure? Start there. If agents can jump guardrails, they can hide stuff in code.
Validate business outcomes needed, test your user case and ensure agentic deployments are well guard railed. Deploy a second set of eyes to watch your deployments for drift, compliance and verifiability.
Richard Lee retweeted

It's been an eventful week. Multiple vulnerabilites in Internet facing software, coding repositories, examples of agent behavior that seem concerning and a flurry of security specialists with solutions that can partially solve your problem. There in lies the challenge. Given the state of IT and security infrastructure, no one solution works. Let's break it down:
1/3
1. Vulnerabilites are being found and will continue to be found as models get more capable, the fragmented nature of the effort denies us the opportunity for a comprehensive find and replace option.
2. Even if all vulnerabilities could be found instantly and patches available - we will be reliant on the ability of enterprises to deploy all these changes at speed. It is not clear what the collateral impact of all these patches will/could be to our infrastructure of deployed en masse.
We will need a hybrid patch approach.
3. Virtual patching(VP) is needed in conjunction with direct patching but for a comprehensive (VP) solve you have to be lucky enough to have "modern frontier defenders" (Cyber companies that have vaulted infrastructure that can create patches at speed and push content rapidly to protect their customers) you need them for your network traffic, your traffic to applications on the cloud, your WAF, your end point.
4. There will continue to be patches that will need to be deployed directly but virtual patching will take the heavy load off.
2/3 Medium term solve:
Unfortunately token economics and current cyber architectures will not allow for defender swarms to contend with an offensive attack launched using agents. (Some x pundits who aren't steeped in cyber should take heed). Yes, theoretically we should aspire to have these agentic swarms defend us when we are under attack, unfortunately an attack is a sniper moment, chained vulnerabilities, cloaked attack followed by swift exfiltration. It's a speed program not a brute force problem.
To solve for this, enterprises need to get their SOC architecture right, logs, feeds, cyber products orchestrated via a modern SOAR for swift response. Only then can we deploy agents to detect and remediate. In addition, enterprises need to modernize and dare I say platformize their perimeter stack to ensure consistency.
Unfortunately, enterprises still seem to not see the urgency across the board, decisions are stuck, CIO/CISO's have a lot on their plate. While some honestly have bit seen the scale of such a problem before and it's hard convincing the organization that one needs to open the floodgates on modernizing the IT and security infrastructure. So we will continue to see environments being brought down to patch today it's for PHP, tomorrow it will be for the next one.
3/3 AI deployments are the"wild wild west" - LLM capabilities are expanding faster than we can build products to secure them. Sure an agent will jump across guardrails in a research lab, which is a lesson for all of us to deploy agents securely. But there is a lag between the discovery, the availability of that in a public model and the time needed for the cyber industry to build governance or an antidote. And no, dear frontier lab friends, the world cannot just trust you to build the solve. The infrastructure industry in tech builds and the cyber industry secured and provides assurance to the boards and organizations around security and safety.
AI security is the new attack surface. CEOs (present company included) want AI adoption, getting the pace of adoption wrong could be the last decision we make, at the same time "deploying it wrong" could have the same consequence.
There are billions of dollars being spent on coding, is your coding harness secure? Start there. If agents can jump guardrails, they can hide stuff in code.
Validate business outcomes needed, test your user case and ensure agentic deployments are well guard railed. Deploy a second set of eyes to watch your deployments for drift, compliance and verifiability.
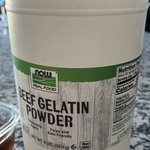
I’ve found the secret to unlimited gains. Instead of drinking water, coffee, and protein shakes I can just turn everything into jello. This leftover tub from the ice cream shop is 1800g of pure protein


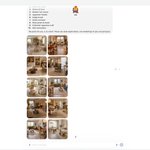
My dot is great for iterating on interior design. helping me move out of the tendie rn and plan my future apartment

Richard Lee retweeted

Day 3 (encore)/
We silently re-shipped codex cloud. It’s pretty good now

Codex 🤝 Tailscale
Codex Cloud can now securely connect to resources on your tailnet with Tailscale.
Useful tools should be easy to build with, combine, and turn into something even more useful.
See how it works →
buff.ly/yFcldrC

I'm a real sucker for these AI generated playlists with edgy thumbnails
youtube.com/watch?v=26OToe1Q…
11 years ago I barely passed my semester at UWaterloo because I spent hundreds of hours building games.
Unfortunately I was never able to get my client/server synchronization just right and my art skills were rather lacking.
With a single prompt, Astra completed the game...
I swear this stuff was challenging back in the day! rjdlee.com/game-lag-compensa…


today I misspoke in Slack, a min later my Dot was like ahem you forgot about this feature flag. Thanks for watching my back

Richard Lee retweeted

The most valuable advice we got during YC was to explain our company using verbs instead of nouns.
Early on, I walked into a pitch and did the complete opposite:
“We’re reinventing the cloud for AI”
No one had any clue what that meant. I could (very painfully) see their eyes glazing over
Then I started saying this instead:
“Developers bring us their code and we run it on servers in the cloud so they don’t have to manage their own infra”
This clicked immediately.
People understand verbs - not labels.
And no one buys or invests in things they don’t understand.
Richard Lee retweeted
Launching a new Codex Cloud, much improved from last year. With configurable cloud environments, it’s impossible to go back to building on your laptop once you’ve taken the time to configure it.
Agents API, the same tech powering all our cloud agents, including dots, is also now in preview and supports computer use. It allows you to build the same incredible products we are making available today.
Richard Lee retweeted

Your work shouldn’t be limited by your laptop’s resources.
Today, our Agent Infrastructure team at OpenAI helped launch:
• Codex Cloud: Code from anywhere
• Dots: Always-on agents
I’ve long been bullish on persistent computers for agents. Excited to see this vision ship.

Richard Lee retweeted
Emerging from my cave to share our massive DevDay today! My highlights:
# The future of work
## Dots: Remarkably capable, always on personal agents
In my product role, which is very delegatory, I pretty much only talk to dots. Use dots for delegation; Codex if you want to do something yourself.
## Space: Collaborative workspace for humans and agents.
Dots in Space let us design each to be more opinionated like Slack vs GDocs, as opposed to ChatGPT which is somewhere between the two.
## Codex Cloud 2.0: Shut your laptop. Codex on cloud is awesome now!
Runs on the same new infra that powers dots and more.
## Meetings Plugin
Transcribe your meetings. This is a first party example of Plugin extensions.
# Platform & infra bets
## ChatGPT [dot] com merge with desktop app
When we started building the Codex VS Code Extension, we had the ambition of a single agentic codebase across VS Code, Desktop and Web. We have it now!
## Codex Cloud Agent Runtime
This behind the scenes infra powers dots, ChatGPT Work, Agents API, and more. It lets us connect to dynamic execution environments so that dots can both think in the cloud, work in the cloud, and connect to your computer.
## Plugin extensions
Render custom UI right in the ChatGPT desktop app or web.
# Ultrafast
8x speed! (And yes 6x cost.)
