

SOC/Intel | @SANSInstitute | @PacktAuthors https://xitter.cf/t.co/itz9Mly1hK Love #PurpleTeaming #DE #CTI #DFIR
EMEA
Joined January 2010
- Tweets2.4K
- Following784
- Followers1.1K
- Likes2K




Pinned Tweet
💜Adversary Simulation and Purple friends💜
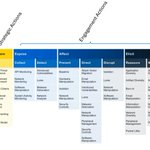
I'm happy to share this simulation plan which regroups a TOP 35 @MITREattack TTPs from 22-23.
Based on open source intel, it's meant to ease the onboarding of more into Purple!
Have a look at the readme #CTI #TTP
github.com/Sam0x90/CTI/tree/…

Sam ☁️🪵 retweeted

🏴☠️ Hello, hackers! 🇦🇪
DEF CON Group 971 (DCG971) is here!
We're bringing together the UAE hacker community to connect, share knowledge, and learn from each other.
🌐 Website: dcg971.org
Stay curious. Keep hacking. 💻
#DC971 #DEFCON #Hacking
👋 @defcon
Sam ☁️🪵 retweeted

I highly recommend following DEF CON Group 971 (DCG971) for cultural learnings of cybersecurity, to make benefit glorious humanity! 🇦🇪🛡️
DCG971 brings together cybersecurity enthusiasts across the UAE to explore, learn, share knowledge and connect.
Very nice! Great success! 👍

Sam ☁️🪵 retweeted

🚀 x64dbg-MCP Server — fully automated, dynamic, agentic reverse engineering for x64dbg.
🧠 71 MCP tools
🤖 Fully automated & dynamic agentic RE
🔴 22 debugger event callbacks
⚡ Native Zig plugin — zero dependencies
🛠️ Breakpoints, memory, registers, tracing, xrefs, PE analysis & more
🌐 Streamable HTTP + SSE
📦 x32 + x64
Let your AI agent control, analyze, debug, and dynamically reverse engineer binaries directly through x64dbg.
🔗 github.com/duty1g/x64dbg-mcp…
#x64dbg #MCP #AgenticAI #ReverseEngineering #CyberSecurity #RedTeam #MalwareAnalysis #Zig

2026 we are responding to AI with AI. We still didn't get the basics right after decades of new acronyms every year EDR, NDR, XDR... Now we are pushing all the CISO to invest in AI rather than getting the basics right...

The "assume breach" era is ending. AI-native security is what comes next.
For 20 years, enterprises operated under a simple rule: Assume attackers are already inside. Build detection, response, and resilience accordingly. It worked — until threats started moving at machine speed.
As we wrap up Black Hat USA 2026, the security model is shifting again. AI-native defense isn't just faster incident response — it's predictive, adaptive, and autonomous. It's security that learns, anticipates, and acts before breaches become business crises.
What's changing:
🔴Threat detection moving from reactive to predictive
🔴Security operations shifting from human-led to AI-orchestrated
🔴Defense strategies evolving from "contain the damage" to "prevent the breach"
The enterprises presenting at Black Hat this year aren't just talking about AI tools. They're rebuilding security architectures from the ground up with AI at the core.
Read the full analysis from Dark Reading managing editors Tara Seals and Fahmida Rashid 👉 bit.ly/43cUTTf
#BlackHat2026 #AIinSecurity #CyberDefense #DarkReading20

Sam ☁️🪵 retweeted

🚨 Investigating a suspected ClickFix campaign affecting compromised WordPress sites globally.
We confirmed polymorphic JavaScript injections on multiple live sites. The loader uses custom variable-width base-N encoding, filters bot-like user agents - including headless browsers, ChatGPT, and Anthropic - removes its own <script> element, and fingerprints the browser. Telemetry is XOR-obfuscated and POSTed over HTTPS to:
C2: siege-close[.]com/x9i32md/w1/la02
The response is XOR-decoded and can be executed through indirect eval(), giving the server arbitrary JavaScript execution in the victim’s browser.
Quick OSINT search identified 44 affected sites across 15 countries.
#ClickFix #ThreatIntel #WordPressSecurity

Sam ☁️🪵 retweeted

The takedown showed the scale.
The leak showed how the machine counted itself.
Full write-up:
tapetumlabs.com/the-outsider…
#CTI #OSINT #Phishing #ThreatIntel #Cybercrime


Sam ☁️🪵 retweeted

It turned out there are many more payloads used in the Notepad++ attack! To stay undetected, its masterminds were COMPLETELY changing execution chains about every month.
Here are more IPs used in the attack:
45.76.155[.]202
45.32.144[.]255
Read below for many other IoCs! [1/8]

Sam ☁️🪵 retweeted

Happy New Year everyone. I wrote something
sec0wn.blogspot.com/2026/01/…
Do I get an honorary #OSEP for analyzing their payloads? Lol. Maybe Gemini should though. H/T to GeminiPro for the assist
Sam ☁️🪵 retweeted
#ElasticSecurityLabs uncovers #RONINGLOADER, a multi-stage loader utilizing signed drivers, PPL abuse, CI Policies, and other evasion techniques to deliver #DragonBreath's gh0st RAT variant.
Check it out at ela.st/roningloader

ALT RONINGLOADER execution flowchart
Doing "grep -iran" has never been so relevant 🙃

There is someone exposing IRGC (Islamic Revolutionary Guard Corps) stuff on GitHub.
I'm not a IRGC geopolitical nerd, so I can't assess the value of the content. However, if you know what the fuck is going on, maybe you'll find it interesting:
github.com/KittenBusters/Cha…

GG @_dirkjan !
I wish to see more of this in the future:
"After some testing and filtering with some fellow researchers that work on the blue side we came up with the following detection query"
👏

I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: dirkjanm.io/obtaining-global…
Sam ☁️🪵 retweeted

We're hiring DFIR consultants (Senior & Principal) for Germany and KSA here at @Unit42_Intel
Germany (must be german speaker) - jobs.smartrecruiters.com/Pal…
KSA (must be arabic speaker) - jobs.smartrecruiters.com/Pal…
Let me know if you have questions. Feel free to DM me ✌🏻#dfir
With all the fuss around #velociraptor thought I'd give a shootout to project LOST (LOL Security Tools).
We started this together with @0xanalyst some time ago. Yes Velociraptor, osquery, defender, wazuh, and much more that would deserve to be documented
0xanalyst.github.io/Project-…
If anyone needs to convert the DarkWebInformer json into csv here is a quick script to properly convert it:
github.com/Sam0x90/QuickCodi…
#CTI #LLM #RAG
If anyone wants to use RAG with their LLM for the @MITREattack I've uploaded a quick script to convert json to md.
Useful in your Ollama/Open WebUI setup. Chunking/embedding done auto by OpenWebUI. Then the model can refer to the KB.
github.com/Sam0x90/AIstuff/t…
Sam ☁️🪵 retweeted

Introducing MCP on Windows! msft.it/6016SjShg
Finaly payload googlerestricted.ide --> msbuild.exe.
@NullPwner so stealc?

🚨 Same Threat Actor is now delivering Windows Payload through the ~2800 compromised sites using ClickFix
It dinamycally changes depending on platform (user-agent) Mac/Win
1: https://e.overallwobbly[.]ru/au1 (Dropper1: era-stau1.a) → PowerShell → Stage 1 Script (AutoIT)
2: https://e.overallwobbly[.]ru/era-std → PowerShell → Stage 2 Code
3: https://nc1.overallwobbly[.]ru/googlerestricted.ide → Final Payload (heavily obfuscated)
Probably using LOLBin.
Hash era-stau: d2465b8f9b36fa3139bcdcacab54591490753cc7f8843f8dddb0831094ef53ac
Hash of dropped Zloader: 4e72ca1baee2c7c0f50a42614d101159a9c653a8d6f7498f7bf9d7026c24c187
Thoughts?
@malwrhunterteam @RussianPanda9xx @500mk500 @ViriBack @Big_Bad_W0lf_ @DaveLikesMalwre @g0njxa @JohnHultquist
#ThreatIntel #ClickFix

Sam ☁️🪵 retweeted

The Offensive Phishing Operations Course has been released.
81 modules are included in the initial launch, with the first update already being worked on.
More information: maldevacademy.com/phishing-c…
Syllabus: maldevacademy.com/phishing-c…