





SarlackLab retweeted

Just learned that our @SarlackLab project has been listed as a Top Contributor on #ThreatFox (for the last 30 days). I’m SUPER PROUD of our team and this most-nerdy accomplishment 🎉
It’s an honor to be listed on such a legendary #Malware-fighting site

SarlackLab retweeted
Given the recent concerns of #InfoStealer malware - I wanted to highlight the @SarlackLab team’s active tracking of #C2 servers and their criminal hosting providers
Recommended Blocklist: github.com/Abjuri5t/SarlackL… 🔥
C2 Hunting: github.com/Abjuri5t/SarlackL… 🏹
#RedLineStealer #malware
SarlackLab retweeted
The @SarlackLab team is posting daily #blocklist & #IOCs to our GitHub
➡github.com/Abjuri5t/SarlackL…
Direct URLs:
- Blocklist (recommended for #firewall 🔥) raw.githubusercontent.com/Ab…
- Indicators (recommended for #IDS/#NDR 🔍) raw.githubusercontent.com/Ab…

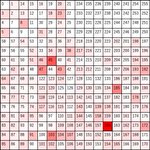
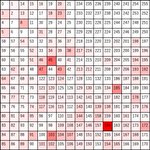
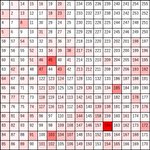
Command-and-control IPv4 map, 2024-05-18 to 2024-05-31 #InfoStealer
abjuri5t.github.io/SarlackLa…
38.128.0[.]0/9
124.220.0[.]0/14
101.42.0[.]0/15
106.52.0[.]0/14
91.92.240[.]0/20
3.120.0[.]0/13
94.156.64[.]0/21
5.42.96[.]0/24
111.230.0[.]0/16
156.242.32[.]0/19

SarlackLab retweeted
LARGE cluster of #DarkCrystalRAT C2 servers hosted within 137.175.0[.]0/17 (‘Peg Tech Inc’ 🇺🇸)
@DonPasci and @censysio identified #DCRat throughout
137.175.68[.]192/28
137.175.70[.]64/26
137.175.73[.]64/26
137.175.77[.]64/26
137.175.123[.]0/25
threatfox.abuse.ch/browse/ma…

Command-and-control IPv4 map, 2024-04-26 to 2024-05-09 #IOCs
abjuri5t.github.io/SarlackLa…
147.45.47[.]0/24
193.233.132[.]0/23
154.213.17[.]0/24
185.172.128[.]0/24
168.76.120[.]0/22
77.221.151[.]0/24
5.42.96[.]0/24
45.15.156[.]0/24
93.123.85[.]0/24
94.156.79[.]0/24

SarlackLab retweeted
Have you seen The Empire in your network?
A #cybercrime group, registered under “EVILEMPIRE”, is hosting dozens of #C2 servers for:
#RedLineStealer #LokiBot #HookBot #RisePro #Amadey #CobaltStrike #AsyncRAT #AMOS
Don’t let your computers enlist! Block 185.172.128.0/24 🔥
SarlackLab retweeted
People often ask why we track #C2 servers based on ASN/IP range instead of geo-location 🌐
In short: Geo-location is cool from a policy perspective
… but knowing the country an attack originates from doesn’t really help #SysAdmins with their day-to-day network defenses
🧵
Command-and-control #IP v4 map, 2024-03-23 to 2024-04-05
abjuri5t.github.io/SarlackLa…
154.216.54[.]0/23
193.233.132[.]0/24
43.240.48[.]0/22
154.219.144[.]0/23
45.156.216[.]0/22
154.219.148[.]0/22
194.147.140[.]0/24
154.219.152[.]0/21
193.143.1[.]0/24
5.181.80[.]0/24

SarlackLab retweeted
Just published research on #RedLineStealer Command-and-Control
- meta-analysis of #C2 infrastructure 📊
- network signatures 🕵️
- war story from late-night #IR ⚔️
Advice: medium.com/@the_abjuri5t/adv…
#IncidentResponse #InfoStealer #Suricata #IOCs

SarlackLab retweeted
RedLine #InfoStealer! 🦹♂️
But I thought the Sarlack was only trained to recognize #NanoCore…
We updated @SarlackLab’s hunting capabilities and are beginning to train it on a variety of infostealers. Stay tuned! 🤓
SarlackLab retweeted
Personally, I think there is value in the historical data for #ThreatHunting, #IR, and general reputation - but I’m interested to hear your thoughts!
If you have any suggestions/preferences, feel free to let me know in the poll or comments

These #BazarLoader C2s are reportedly offline - but they’re still on the map bc @SarlackLab’s threshold is 14 days since a #C2 was reported/verified
What do you think the TTL for IPs on the map should be? 🗺️
Please comment with any thoughts/suggestions/questions
0%24 Hours
100%7 Days
0%Keep at 14 Days
0%ALL OF TIME
1 votes • Final results SarlackLab retweeted
These #BazarLoader C2s are reportedly offline - but they’re still on the map bc @SarlackLab’s threshold is 14 days since a #C2 was reported/verified
What do you think the TTL for IPs on the map should be? 🗺️
Please comment with any thoughts/suggestions/questions
0%24 Hours
100%7 Days
0%Keep at 14 Days
0%ALL OF TIME
1 votes • Final results SarlackLab retweeted

Hello HA Community! This is a PSA: Retiring Falcon Sandbox Public API V1 Starting August 3, 2021. After this date, the Falcon Sandbox Public API v1 will stop responding altogether, so please be sure to transition to API v2 before that. More on our blog: hybrid-analysis.blogspot.com…

SarlackLab retweeted
New changes to my #IPv4 pewpew map. Seems to be a lot of new activity in the 119.0.0.0/6 range
C2 server IPs now also being pulled from @ViriBack @ScumBots and @HybridAnalysis. Thank you all for sharing your research publicly

SarlackLab retweeted
Top networks with the highest amount of new malware sites on URLhaus in September 2020 👎
1,021 AS30962 COMTRANCE 🇩🇪
985 AS13335 CLOUDFLARE 🇺🇸
518 AS36352 COLOCROSSING 🇺🇸
517 AS6724 STRATO 🇩🇪
👉 urlhaus.abuse.ch/statistics/
SarlackLab retweeted
Ever wonder why malware repositories refer to every sample by its #hash?
Ya, spend some time coding with their APIs, I promise it will make perfect sense ☕️
#LearningRE #MalwareBazaar #TooMuchCode
