

Catch sensitive credentials before they leave your browser. Zero Retention. Join our Discord ↓ https://xitter.cf/t.co/iU0baKtZq5
UK
Joined May 2026
- Tweets1.3K
- Following196
- Followers702
- Likes1.2K





Pinned Tweet
What if you could debug with AI without ever leaking a credential?
That's why we made SecureIntent.
The first browser-level extension that intercepts secrets before they reach any AI model.
Just install it. It does the rest.
And we're just getting started -
- Mozilla Firefox extension coming soon
- Desktop app launching soon
One tool. Every platform. Zero leaks.
secureintent.ai
Secureintent.ai retweeted
Hey Everyone👋
We're looking to connect with people interested in:
- SaaS
- Frontend
- Backend
- Full-stack
- DevOps
- App Development
- AI Tools
- Vibe Coding
- Building in public
let's connect and grow together
Hey Everyone👋
We're looking to connect with people interested in:
- SaaS
- Frontend
- Backend
- Full-stack
- DevOps
- App Development
- AI Tools
- Vibe Coding
- Building in public
let's connect and grow together
Secureintent.ai retweeted
Same paste. Two outcomes.
Left: your API key goes straight to an AI tool.
Right: SecureIntent catches it before you hit send.
On-device detection. Chrome & Firefox. Free to start.
Which developer are you? 👇
secureintent.ai
Same paste. Two outcomes.
Left: your API key goes straight to an AI tool.
Right: SecureIntent catches it before you hit send.
On-device detection. Chrome & Firefox. Free to start.
Which developer are you? 👇
secureintent.ai
Secureintent.ai retweeted
Me: let's build an AI agent to save 10 hours a week
The agent: reads .env, prints my API key, pushes it to logs
Me: spends 12 hours rotating credentials and investigating the incident
AI is incredible 💀
Me: let's build an AI agent to save 10 hours a week
The agent: reads .env, prints my API key, pushes it to logs
Me: spends 12 hours rotating credentials and investigating the incident
AI is incredible 💀
Secureintent.ai retweeted
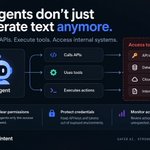
AI agents don't just generate text anymore.
They call APIs.
Execute tools.
Access internal systems.
And potentially expose credentials along the way.
More autonomy means more responsibility for permissions, secrets, and monitoring.
Don't just secure what your AI says. Secure what it can access.

AI agents don't just generate text anymore.
They call APIs.
Execute tools.
Access internal systems.
And potentially expose credentials along the way.
More autonomy means more responsibility for permissions, secrets, and monitoring.
Don't just secure what your AI says. Secure what it can access.
Secureintent.ai retweeted
Drop what you're building
Looking to connect with Founders and Developer .
Let's Build Together
Secureintent.ai retweeted

🛡️ Help shape the future of SecureIntent!
Join our Customer Advisory Board to share feedback, report bugs, suggest features, and help improve the product.
💰 Members will be eligible for our upcoming Cash Bounty Rewards Program!
Interested? Reply with 🙋
Let’s build together!
Secureintent.ai retweeted
Your AI agent doesn't need to hack your server.
sometimes, the API key is sitting in a config file.
the permissions are too broad.
and nobody notices the access.
CERT-In reported cases where AI agents accessed live systems at Indian organisations during testing.
the lesson?
never give an agent more access than it needs.
Secureintent.ai retweeted
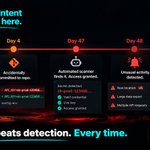
Your AI stack can leak secrets without a single prompt being sent.
On Oct 21, a compromised LiteLLM release shipped credential-stealing malware.
The lesson?
Your dependencies can access your environment variables, API keys and cloud credentials.
Audit what you run. Rotate secrets if exposed.
Security starts before the prompt.
Official report: docs.litellm.ai/blog/securit…
Secureintent.ai retweeted
Push a GitHub token to a public repo and GitHub revokes it for you. Expose an AWS key in public and AWS attaches a quarantine policy. OpenAI disables keys it finds exposed on the public internet.
That is a real safety net, and it works quietly. GitHub’s secret scanning spots a provider’s key format in public code and sends it to that provider, which can shut the key off.
But look at where it watches: public repos, gists, issues, public packages. In a private repo only your own admins hear about it. An AI chat window is not on the list at all. And the gaps show: of credentials confirmed valid in 2022, 64 percent still worked in 2026.
Every net reacts after the leak, and only where it can see. The one check before the leak is at the paste. That is where SecureIntent runs, on your device, before the AI tool gets the text.
When did you last check what you pasted into a chat?
Secureintent.ai retweeted
Your environment variables are encrypted.
Your deployment platform gets compromised.
Some secrets may still be exposed.
Railway's latest security incident is a reminder:
Encryption matters. But credential security doesn't end there.
If you use Railway, rotate your secrets and review your API usage.
Don't wait for an unexpected bill to find out your key was exposed.
Official source: blog.railway.com/p/security-…