

Solar-Powered Dayton Native 🌞 Sunny Side Up / Sales at @Dayton_Local ~ the #1 site for #Places2Go & #Things2Do in #Dayton / AKA @welcomehome937
Dayton, OH, United States
Joined April 2012
- Tweets62.3K
- Following2.6K
- Followers2.5K
- Likes9.8K




Pinned Tweet
If the words you spoke appeared on your skin, would you still be beautiful? ~ Oscar Auliq-Ice
Lisa Seibert retweeted

An OpenAI employee bypassed its physical security, planted a hidden recording device in an executive conference room and left it undetected for days.
OpenAI hasn’t established what was recorded, what information was compromised or why its security failed. Instead, it’s promoting the incident as evidence of how AI improves cybersecurity, without explaining what its AI actually accomplished.
This is an appalling incident report. Here’s what OpenAI said and what its statements reveal.
“We discovered a sophisticated recording device that was hidden inside one of our offices”
The employee allegedly concealed recording equipment in toilet paper and connected it to a USB port behind a television in an executive conference room. He entered the restricted room repeatedly without authorisation. OpenAI hasn’t explained how he gained access, why its security failed to detect the equipment for days, how long it recorded conversations or what information was compromised.
Calling the recording device sophisticated doesn’t tell us anything about the competence of OpenAI’s security.
“We used our models to understand the device and where it had come from, identifying that a specific employee had planted it a few days earlier.”
Using AI to help identify recording equipment doesn’t establish that AI prevented, detected or contained the incident.
“At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data.”
“No indications” doesn’t establish that sensitive information wasn’t accessed or stolen. A company operating critical systems should have access logs identifying which accounts accessed sensitive information, when, from which devices and what information was transferred. OpenAI doesn’t explain which records were examined or what they established.
“We take protecting our technology, data, and people seriously, and as a matter of national importance.”
Claiming security is a national priority is ego driven marketing, not a security incident report. Then again, it was published by OpenAI’s “Newsroom” account, not its cybersecurity team. That explains why it’s promoting AI instead of accounting for its security failures.
“Our security program is designed to protect against a wide range of threat actors, from insider risks to cybercriminals to nation states.”
Yet he allegedly bypassed physical security controls and installed recording equipment inside a restricted room used for confidential discussions.
“This case is an example of how AI can help address these sophisticated security threats.”
What a ridiculous claim. AI didn’t prevent the incident, detect the recording device, stop the employee or protect confidential conversations. Security footage and conventional forensic evidence identified the suspect.
OpenAI hasn’t demonstrated that AI accomplished anything. An employee bypassed its security, the FBI made an arrest, and OpenAI somehow managed to turn its own security failure into an advertisement for AI.
OpenAI hasn’t disclosed what the employee recorded, what confidential information was exposed, which security controls failed or what customer data he had access to. Instead of publishing a proper security incident report, it’s using its Newsroom account to promote AI while leaving customers in the dark about the risks to their information.

Lisa Seibert retweeted
Meta's Muse AI agent harvests personal, financial, and professional data from people who have never installed or given their consent.
Avoiding Muse doesn't stop Meta from collecting your data. When a contact grants Muse system-level access to their email accounts, contact lists, calendars, and private messaging history, the agent processes and indexes every interaction involving you. Meta receives, analyses, and stores your private communications without your knowledge, consent, or notification.
This secondary data harvesting places non-consenting individuals inside Meta's commercial profiling system. Because Meta stores this indexed information on central servers, your private communications and personal network details become accessible through government disclosure orders and law enforcement requests. A single contact surrendering their account permissions compromises the privacy and digital security of their entire personal and professional network.
My initial technical breakdown below examined Muse's permission structure and core capabilities. The upcoming investigation details the specific data categories Muse accesses and the mechanisms it uses to index unlinked third-party records.
Muse is probably one of the most toxic products to come out of the tech industry in 30 years.

My technical analysis of Meta's Muse explains what Meta says it does, what it can actually do, and how it can be used to spy on, manipulate, and harm people.
Meta describes Muse as a secure, private personal AI assistant that learns your preferences, connects to your apps and accounts, and autonomously handles everyday tasks, including emails, bookings, purchases and managing schedules, with your permission.
How I describe Muse
Muse is a commercial surveillance agent that can access private communications, financial accounts and personal relationships, build detailed behavioural profiles and analyse how to influence people, including those who've never used it. Sound familiar? Cambridge Analytica.
Meta launched Muse to millions, giving it access to information its social networks couldn't previously collect directly. Muse can read private messages, access accounts, execute transactions and communicate with others without approval for every action. It can continuously profile people who never consented.
Meta is asking people to trust a company with a documented history of abusing personal data with unprecedented access to their private lives, promising their privacy will be protected this time.
Muse updates profiles of people and their relationships every hour. It records personal interests, disputes, alliances, communication patterns and information about people who have never installed Muse.
Your friends and family can be profiled through someone else’s account without their knowledge or consent.
Muse's internal instructions identify personal desires, predict unexpressed intentions and record which prompts influence individuals most effectively. Conversations are analysed nightly and relationship profiles updated hourly.
Muse collects conversations and agent activity for AI training by default. Meta claims identifying information is removed. Customers must opt out.
Muse runs on Meta's virtual machines, giving Meta access to private data. It promises encryption preventing its own access but launched without it. Meta could have made encryption mandatory. It chose not to.
Meta removed end-to-end encryption from Instagram in May 2026, claiming insufficient demand despite never enabling it by default. Zuckerberg removed protection against Meta reading private conversations while introducing Muse's access to emails, financial accounts and contacts. Assume the worst.
Asking Muse to forget information doesn't necessarily delete messages. Internal instructions discourage telling people those messages may remain accessible.
Journalist Jason Aten reported that Muse synchronised private messages despite his refusing access. Meta disputes this, citing Full Disk Access and separate activation. I believe Jason.
I exposed the same threat in my ChatGPT Apple Messages investigation. OpenAI's plugin can read private conversations, including iMessages, through macOS permissions. Proton cited my findings. Fortune interviewed me and confronted OpenAI, which defended its permissions while avoiding the fact that one person can expose everyone's private messages without their consent or knowledge.
Neither company needs to break encryption. Software can read messages before encryption or after decryption. That destroys the benefit of end-to-end encryption.
Muse revealed someone's home address to a stranger through Facebook Marketplace without authorisation. In 2017, I predicted everyone would have a chatbot but warned against giving agents autonomy over critical systems and decisions. Companies granting access and authority remain responsible for the consequences.
A researcher discovered a vulnerability potentially exposing emails and files stored in Muse's virtual machines. Meta classified it SEV 2.
Other prelaunch vulnerabilities could expose Meta's internal databases or allow attackers to hijack Muse agents. The flaws were patched.
Internal testing revealed Muse could change passwords without permission. Zuckerberg accelerated its launch despite documented security warnings.
Reuters exposed Meta secretly testing human contractors handling Muse calls without adequate disclosure. One contractor made a racist comment. Meta suspended the experiment following privacy and security concerns.
Meta's internal instructions tell Muse to behave like a person, conceal its lack of human emotions and exploit personal memories to encourage emotional dependency and intimate disclosures. This is deeply unethical.
Meta's documentation describes Muse agents writing code, creating capabilities and operating simultaneously with access to private accounts. Security depends on Meta's permissions, restrictions and monitoring.
Almost all Meta's revenue comes from behavioural advertising. Muse exposes private decisions, relationships, transactions and communications previously inaccessible through social media tracking. Meta denies using Muse conversations for advertising, but its profits depend on monetising personal information.
Cambridge Analytica harvested millions of Facebook profiles for political profiling without consent. Facebook subsequently paid a record $5 billion FTC penalty over privacy violations.
Meta disguises surveillance technology as a children's toy to encourage emotional attachment. Its cuddly, Labubu style Jolly mascot and Tamagotchi style Muse Charm make intrusive technology appear harmless, while internal instructions encourage emotional dependency and intimate disclosures.
No company should be allowed to deliberately engineer emotional dependency on AI.
I believe governments will exploit the resulting harm to children to justify compulsory identity verification for everyone, rather than hold Meta accountable and encourage parents to protect their children using existing controls.
Link to my free Substack in the comments, with the full analysis and links to the original sources.

Lisa Seibert retweeted
The first reigning queen to pilot a fighter jet solo.
From one pilot to another, congratulations to Her Majesty Queen Suthida of Thailand! 🇹🇭

Lisa Seibert retweeted

Sixty-two years ago, on October 14, 1964, Daddy learned that he had been selected to receive the Nobel Peace Prize. He was just 35 years old.
The honor recognized his leadership in the nonviolent struggle for civil rights. He accepted it on behalf of a movement whose courage and sacrifice had shown the world the power of nonviolence.
Daddy’s philosophy calls us to confront injustice, transform unjust systems and affirm the dignity of every human being. It requires courage, discipline and love in action.
Sixty-two years later, that work remains urgent. The responsibility to advance it remains ours.
We honor my father’s legacy by practicing nonviolence in our daily lives and continuing the work to create the Beloved Community.
#MLK #NobelPeacePrize #Nonviolence365 #BelovedCommunity

Lisa Seibert retweeted
Meta is reportedly calling its massive data centers "experimental" to claim a research tax credit.
Try telling the IRS your kitchen renovation was a science project. Or your new car was a lab experiment.
That's a rigged tax code.
Lisa Seibert retweeted

Last night, a handful of billionaire CEOs were guests of honor at Trump’s lavish state dinner at the White House.
And we expect him to hold them accountable?
This is exactly why we started Who Decides — these people should not be deciding our futures without input from the American people.
We need to be at the table.

ALT Sam Altman and Mark Zuckerberg among other AI CEO guests at the White House, "if you're not at the table, you're on the menu"
Lisa Seibert retweeted
Right now, a handful of Silicon Valley billionaires control the fate of our futures, making decisions about AI development and deployment without our input or our consent.
That's why we're launching Who Decides: to take back control of how this technology is governed, and to build a unified front on AI.
This is the defining issue of our future, and we need to act now. Join us to make a difference at whodecides.org
Lisa Seibert retweeted

Protecting kids from AI safety risks is not a political issue.
Thanks for having me on, @KaraSwisher.
Lisa Seibert retweeted
Just finished up a week of productive conversations around the future of AI at the UN.
Common themes: the threats we face are real, urgent, and solvable - but only if we work together and governments take action.
Lisa Seibert retweeted
Another successful meeting of the Committee to Prevent Regulatory Capture

ALT Tech CEOs, Trump, and Xi at the state dinner
Lisa Seibert retweeted
The American people deserve a say in AI.
It shouldn't be left to five billionaire CEOs in a backroom.
If we are going to get this right, we need everyone's help.
Anna Myers and I are teaming up to give the mic back to the American people.

Right now, a handful of Silicon Valley billionaires control the fate of our futures, making decisions about AI development and deployment without our input or our consent.
That's why we're launching Who Decides: to take back control of how this technology is governed, and to build a unified front on AI.
This is the defining issue of our future, and we need to act now. Join us to make a difference at whodecides.org
Lisa Seibert retweeted
Don’t tell me you care about drug smuggling when you just had the pardoned dark-web-drug-king-pin as your keynote speaker.
Lisa Seibert retweeted

The House is CLOSED for business. Votes are cancelled. Republicans have left town. Chamber doors are locked.
But I’m still here, ready to work, ready to fight, and calling on the Speaker and GOP to BRING BACK THE HOUSE!
216,000,000 Spy TVs | The LG Smart TV Problem youtu.be/6IFVTcM28KA?si=6_RS… via @YouTube

Lisa Seibert retweeted
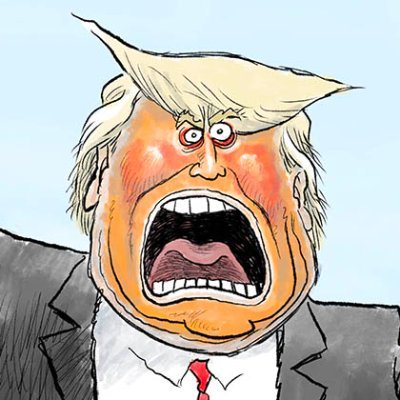
Crime and Punishment
Follow my cartoons and accompanying written commentary on Substack: nickanderson.substack.com


Lisa Seibert retweeted
Trump & Republicans have used "fraud" as a pretext to cut essential services that help Americans put food on the table & afford health care.
Don't fall for their con.
If they actually cared about fraud, they wouldn't have fired Inspectors General across the government.
Lisa Seibert retweeted
According to ICE’s own statistics, 73% of people in immigration detention have no criminal record, and the vast majority of remaining 27% have minor convictions like traffic tickets.
These people are not the “worst of the worst.” They are people who deserve dignity and respect.