SlowMist is a Blockchain security firm established in 2018, providing services such as security audits, security consultants, red teaming, and more.
Joined April 2018
- Tweets4.3K
- Following412
- Followers91.6K
- Likes3.5K




SlowMist retweeted

Dirty money isn’t only caught once it reaches an exchange. On-chain fund flows are traceable by nature.
Before accepting funds from an unfamiliar address, or from a “friend” or “relative,” check the address on MistTrack first. You’ll see its risk score, associated labels, and upstream/downstream fund paths, so you can spot fraud- or laundering-related risk early.
A check takes a minute. A freeze can take months to resolve.
👉 dashboard.misttrack.io/



SlowMist retweeted
We’re seeing @tether freeze a significant number of $USDT across addresses linked to this incident.
Based on our current tracking, the reported losses are approaching $90 million. Some affected users have contacted us for assistance, and our team is actively following up on these cases.
bc1qjqgwejnp8dc0x2938x9n9954hj97t82unx49dl
bc1qqnkwurxs99xkx5t4yffqhq3u6qwy0qpjyujtm9
bc1qgqheemzla77pesl227hdtgf5ykz62d0zvld26n
TK6DWNpNe1w2iJRNFpU8aHdrPTATxvXT6C
TBkcUMYC7CkTK99tkTnaStQVBastfrs9d9
TCGE3xp6YGRKXxDZiLfysgJW3f22KfMNsW
TSDWtuZ2pARUVz4v3PkL2hi3iXPjowAr5a
0x69c8f401cfc6cd40ac94691d6d7c48e3b7a47841
0x033636e45d519bebb7b5c2520ca6ce56fbdb4f7a
0x83aeac166f6832ae3500000a24510a95a052a599
🫡 cc @SpecterAnalyst


Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: support.ledger.com/
SlowMist retweeted

We are very grateful for SlowMist's quick response and professionalism in helping us investigate this incident thoroughly. They have shared their findings on the September 24 security incident.
Their investigation identified malicious activity involving third-party security products, including a zero-day vulnerability, and recovered a customized tool used by the attacker to initiate unauthorized withdrawals.
The findings align with the attack path we previously shared and add further detail on how the incident unfolded.
Our focus is firmly on what comes next: applying these findings, continuing to strengthen our security controls and continuing to protect our users and their assets.

@bitget has engaged SlowMist’s security team to investigate the September 25 hot wallet asset theft.
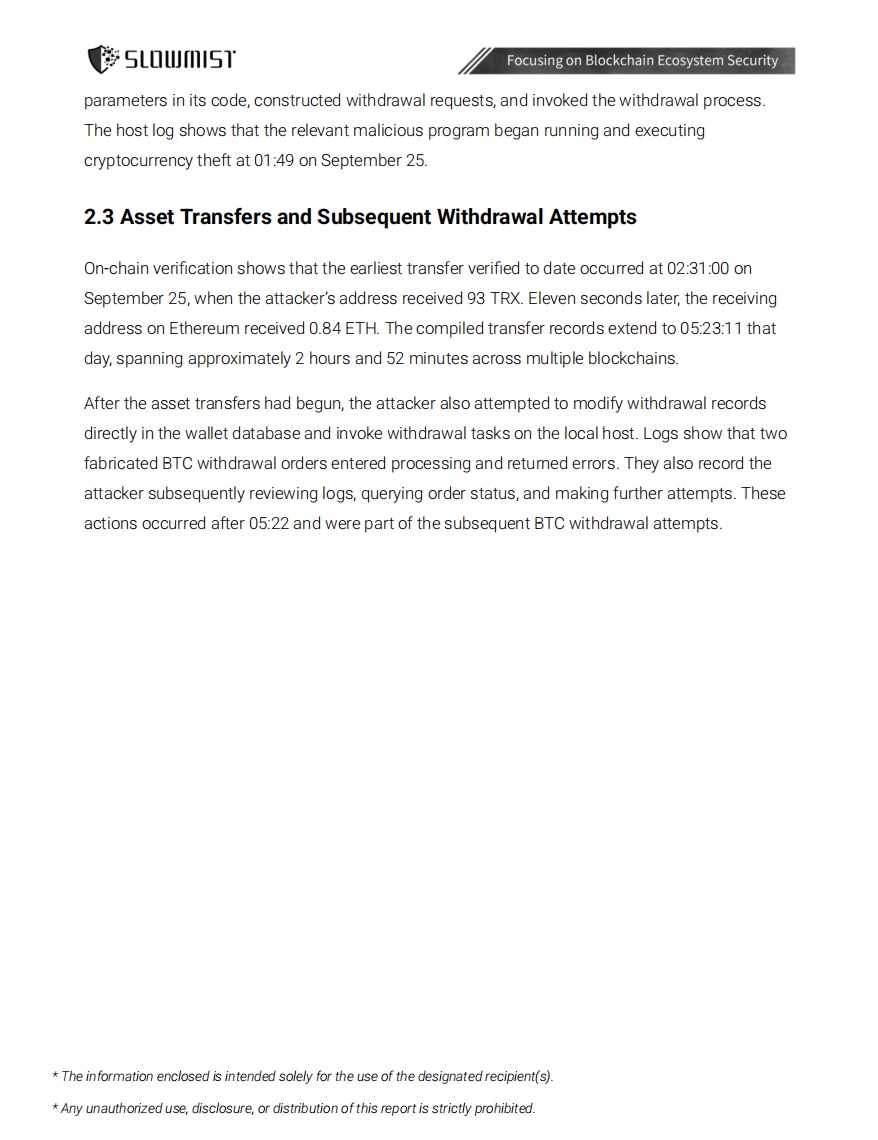
As of September 29, our investigation has identified malicious activity involving certain third-party security products and a wallet application host, as well as a highly customized withdrawal tool used by the attacker.
🔎 Key findings include:
1. Malicious activity on a certain third-party product involving exploitation of a zero-day vulnerability.
2. Unauthorized access to a certain third-party products management platform on September 25 using an internal employee identity.
3. Recovery of a customized withdrawal tool designed to interact with the wallet system’s withdrawal logic.
4. On-chain activity begins at 02:31 on September 25, with transfers across multiple blockchains over approximately 2 hours and 52 minutes.
5. Subsequent attempts to manipulate withdrawal records and trigger additional BTC withdrawals.
We are continuing to investigate how the attacker moved between the affected systems.
All date references are to UTC+8.
📄 Read the details of the investigation:
github.com/slowmist/Knowledg…

SlowMist retweeted
The @bitget exploiter tried to move the stolen funds through @Chainflip.
Chainflip’s response?
“Deposit rejected by the broker.” 👋
No freeze, but no luck either — the funds were refunded. 👍
Nice try. 😶
We’ll continue tracking the movement of the stolen funds.
🔗 scan.chainflip.io/channels/1…


SlowMist retweeted
So far, we have identified the following addresses associated with the @bitget exploiter that still hold funds. We will continue to update this list. @GracyBitget @xiejiayinBitget @Bitget_zh docs.google.com/spreadsheets…


[SECURITY NOTICE] Bitget Hot Wallet Incident — September 24, 2026
At 18:31 UTC on September 24, 2026, Bitget's security systems detected unauthorized transfers from some of our hot wallets. Our security team activated emergency response protocols immediately.
What we have confirmed:
-Estimated funds affected: approximately $351.6 million
-Cold wallets remain fully secure. Bitget operates a three-tier wallet architecture — the breach contained only a portion of the hot wallet and warm wallet layers.
-User funds are safe. The full amount of this loss falls within the coverage of Bitget's User Protection Fund, which currently holds over $464 million
Actions we have taken:
-Emergency response team activated within minutes of detection
-Abnormal transfer addresses identified, flagged, and reported
-Withdrawals temporarily suspended as a precautionary measure, pending security review
-Law enforcement and on-chain security firms have been formally notified and are engaged
What this means for you:
-Your account balances are accurate and your assets are protected
-Deposits and trading remain fully operational
Withdrawals are temporarily paused and will be restored as soon as the security review is complete
-What comes next: We will provide updates on an hourly basis across this channel and all official platforms. A full incident report — including root cause analysis and corrective actions — will be published within 24 hours. We will not speculate on the attack vector until the investigation is complete.
Bitget has navigated multiple market cycles. We will not run from this. Every dollar and every decision will be accounted for, transparently and in full.
Updates will be posted here and across all official Bitget channels as they become available.
— Gracy Chen, CEO, Bitget
SlowMist retweeted

⚠️ Security Alert: FomoPeek v1.1-1.2
A joint investigation by our security team and @SlowMist_Team has found malicious code in FomoPeek App versions 1.1–1.2 that may expose private keys, seed phrases, credentials, and other sensitive data on iOS devices.
If you've installed or used these versions:
• Stop using FomoPeek immediately
• Create a new wallet with new keys on a trusted device where FomoPeek was never installed
• Transfer your assets to the new wallet as soon as possible
• Update iOS to the latest available version
• Check your accounts for suspicious activity
If you detect unauthorized activity, contact the relevant platform's official support team and retain the affected device and evidence for investigation.
Protect your keys. Stay vigilant.
SlowMist retweeted

⚠️ Security Advisory | iPhone Users: Check Whether You’ve Ever Installed the FomoPeek App
Binance is aware of a security incident recently disclosed by the community. According to security firms including SlowMist, the third-party app FomoPeek (versions 1.1–1.2) contains malicious code that can exploit iOS system vulnerabilities to gain the highest level of device privileges, potentially accessing sensitive data stored on the device, including private keys, seed phrases, login credentials, chat history, files, and more.
Please note that this type of malware targets the device itself. If an attack succeeds, data from all apps on the affected device may be accessed.
Please check the following:
1. Are you using an iPhone or iPad running iOS 26.x or earlier?
2. Have you ever installed the FomoPeek app?
If both apply to you, we recommend taking the following steps immediately:
1. Delete the FomoPeek app and do not reinstall it.
2. Update your iOS to the latest available version.
3. For self-custody wallet users: On a device that has never had the app installed, create a new wallet and transfer your assets to the new wallet address.
4. If you notice any unusual asset activity, preserve the affected device and relevant evidence, and contact Binance Customer Support for further investigation.
We also remind all users: Do not install apps from untrusted sources, and keep your device software up to date.

SlowMist retweeted

CYPHER‑ASIA Summit | The Intelligent Crypto‑Finance Summit Concludes Successfully
What happens when traditional finance, crypto, AI and RWA are brought together around the same table?
Will next‑generation finance truly move on‑chain?
One shift is crystal‑clear behind these discussions:
In the past, crypto sought access to traditional‑finance systems. Today, traditional‑finance players are exploring how to bring real‑world assets, payments and financial services onto the blockchain.
As technology, capital, assets and regulation gradually interconnect, crypto is evolving beyond a pure trading marketplace into a broader digital‑financial infrastructure.
This may well be the next phase that truly matters for intelligent crypto‑finance.
Organizers: @FosunWealthHK @FinChain_EN @MEeventHK @feixiaohaocom, Accelerator
Speakers & Participating Organizations: @kucoincom @SunnyFengHan @NanoLabsLtd @JackClawAI @Solana_Company @exSatNetwork @_BitfireGroup @animocabrands @SlowMist_Team @0G_labs @monad @kamino
SlowMist retweeted

0x03D8096377Ea7683d840E395d72439F7B6415Abe was exploited.
Power by SlowMist AI 👇
bscscan.com/tx/0x96c9ce3c527…
Attack Overview
Attack Type: Oracle Manipulation (AMM Spot Price Manipulation) + Staking Reward Distribution Logic Flaw (Missing rewardDebt update) + EIP-7702 Account EOA Restriction Bypass
Victim Contract: Stake (0x03d8096377ea7683d840e395d72439f7b6415abe)
Attacker Address (EIP-7702): 0xc93a5ab3737081f00788b61da42281955d3df692
Helper Accounts (EIP-7702): 0xfd11c78a2ffc9102080f1accfb2c9cd2ce2aceab, 0x9007983c0b1db337e3c0ff29771027b8e2be550b
Total Profit: Approximately 209,793 USDT (133,490 USDT secured by 0xef670d9c2e24d1788f39ad35c70f4cc51b4e5898 and 76,303 USDT by 0x972bfaae4093baf00bd5b4db2e11d143adc16f97)
Flash Loan Source: Moolah Protocol (0x8f73b65b4caaf64fba2af91cc5d4a2a1318e5d8c), borrowing 1,900,000 USDT
Root Cause Analysis
Primary Vulnerability — Missing rewardDebt Update During Referral Reward Distribution
Contract: Stake (0x03d8096377ea7683d840e395d72439f7b6415abe)
Function: _distributeRefPower(address user, uint256 power)
Secondary Vulnerability — Price Oracle Utilizing AMM Spot Price
Contract: Stake (0x03d8096377ea7683d840e395d72439f7b6415abe)
Functions: getPowerAmount(uint256 amount) → getTURPrice() / getNobelPrice()
Both price sources rely on getReserves() (AMM spot price), which can be manipulated via flash swaps or large-scale swaps within a single transaction. This allows the attacker to artificially inflate the _power value calculated by getPowerAmount(), thereby magnifying the amount of power distributed to referrers via _distributeRefPower.

SlowMist retweeted

📢Assets and Security: Building Safe Financial Infrastructure for the Next Era
Join us with:
🎤 @MetaEraCN , Host
⭐️ @AlexD_HashKey, Senior Operations Manager of @HSKChain
⭐️ Lisa, Head of Security Operations at SlowMist @SlowMist_Team
🕗 Time: 20:00 UTC+8, Feb 9
🔗 Space link: teapawt.net/i/spaces/1djGXWroEORKZ…
#HashKeyChain #Hackathon #HSK #HSKChain #SlowMist

SlowMist retweeted
HashKey Chain - Horizon Hackathon is here!
🗓 Feb 1 – 13
🏆 Winners receive:
→ Prize Pool: 8,000 USDT
→ Official Incubation + Resources from HashKey Chain
Hosts:
@HSKChain | @dgrid_ai | @EthAppsGuild
Co-hosts:
@SlowMist_Team | @CalBlockchain | @BitMartExchange | @billions_ntwk | @BlockchainNYU | @StoneLink_Cloud
Ecosystem Partners:
@AWS_HongKong @0xtheweb3 @DoraHacks
Bring bold ideas. Build real applications.
#HorizonHackathon #Web3 #Hackathon #HashKeyChain

SlowMist retweeted

Excited to announce @PureWalletPlus's long-term security partnership with @SlowMist_Team! 🚀 This collaboration brings top-tier audits, threat monitoring, and ongoing protection to our wallet and chain ecosystem. With SlowMist's expertise in blockchain security, we're ensuring robust safeguards for your assets—offline key generation, multi-chain support, and beyond. Stay secure in Web3! #PureWallet #BlockchainSecurity #CryptoSafety
SlowMist retweeted
🚨 Scam Sniffer 2025 Report is out!
Crypto phishing losses dropped 83% — $494M → $83.85M, with 106K victims (-68%).
But the threat followed the market: Q3 rally = highest losses. EIP-7702 exploitation emerged post-Pectra.
Full report 👇
drops.scamsniffer.io/scam-sn…
SlowMist retweeted

🚀 Let's Build Trustless Agents (ERC-8004) — Phase 2: Casual Hackathon Launches Today!
📅 Oct 27 – Nov 9 | Reg + Learn + Workshops Oct 28 – Nov 8 | Open Day Nov 2 (Ideas + QA + Team Match) | Demo Day Nov 9
💬 Chat t.me/Trustless_Agents_ERC_80…
🧑💻 Join
github.com/CasualHackathon/T…
Hack · Learn · Connect · Have Fun 🧩


We’re launching “Let’s Build Trustless Agents (ERC-8004)” — a community initiative to advance ERC-8004 as the trust layer for Ethereum’s AI agent economy!
🔗 Register: intensivecolearn.ing/en/prog…
💬 Join: t.me/ERC8004
SlowMist retweeted

🌐 The Altseason is here, but it’s only a partial Altseason. How can entrepreneurs find PMF, build resource networks and moats, and survive?, how can entrepreneurs find PMF, build resource networks, and create moats to survive?
Tomorrow evening at 8 PM, BuildSpace's next event will feature practical insights and insights from frontline entrepreneurs.
🗓️ Time: Tuesday, September 23rd, 8:00 PM UTC+8
🎙️ Host: @Ethean_yu | @OurTinTinLand Brand Manager
🪐 Guest Lineup:
- Keywolf | @SlowMist_Team Partner & Chief Product Officer
- @Jack_C_Chen | Moon Lab
- @estherinweb3 | @Conflux_Network
📍 Follow @OurTinTinLand and tune in for the livestream.
🙌 Also, don't miss the BuildSpace Web3 Talent Program! 👉 forms.gle/6Jwbdub5WLQ9oosy7
💬 Add our WeChat assistant Tina [TinTinLand2025] for event details!
#Web3 #HongKong #BuildSpace #VC #TinTinland

SlowMist retweeted
🚨MistTrack Update on @yalaorg Incident
1️⃣ #Polygon Phase
🔹Initial addr: 0x55d67b5e0e1c88f48c8a9d978ea76b9ec9d488a9
🔹Gas from ChangeNow (104.49 $POL)
🔹Minted 120M OFTU
🔹Bridged 30M OFTU → 30M YU to Solana addr 87pS8qCum6qaSszbvoARBmFg1Mh1cqcE4ZTAsXfejBMz via LayerZero
2️⃣ #Solana Phase
🔹Addr: 87pS8qCum6qaSszbvoARBmFg1Mh1cqcE4ZTAsXfejBMz
🔹Gas from ChangeNow (0.82 $SOL)
🔹Bridged 10M YU to EVM addr 0x29F48B783EF90F81B51242D9a55e022A214274F5
🔹Sent 17.5M YU to 3pPbujCguJzhSakCYundcfjoaXC4JX1aHcDkAukR3J3h (still idle)
🔹Swapped 2.5M YU ≈ 2.49M USDC
🔹Bridged 2.43M USDC to 0x29F48B783EF90F81B51242D9a55e022A214274F5
🔹Also: 50K USDC → ChangeNow, 7,566 USDC → KuCoin
3️⃣ #EVM Phase
🔹Addr: 0x29F48B783EF90F81B51242D9a55e022A214274F5
🔹Gas from ChangeNow (0.57 $ETH)
🔹Swapped 5.213M YU → 5.213M USDC
🔹Sent 4.787M YU → Yala Deployer
🔹Aggregated 7.64M $USDC → swapped via Wintermute & UniswapX for 1635.57 ETH
🔹161 wallets received ~10.1 ETH each, 1 wallets received 6 ETH → to SimpleSwap
🔹15 wallets have already deposited ETH into Tornado Cash
🔹Remaining ETH idle in 146 wallets
MistTrack will continue monitoring.🕵️


SlowMist retweeted

🎙️《鏈上合規信任基石:香港穩定幣反洗錢新紀元》
在香港虛擬資產行業協會 HKVAIA 的支持下,HashKey Group、@RD_Technologies、@SlowMist_Team、@Beosin_com 共同成立 數字資產反洗錢專業委員會(DAAMC),並將於 9 月 17 日舉辦首場活動。
📍 香港中環|16:00–18:30
聚焦政策落地、技術創新與全球協同 🌐

SlowMist retweeted

Our protocol recently experienced an attempted attack that briefly impacted YU’s peg. Thanks to the quick collaboration with @SlowMist_Team and our security partners, we’ve identified the issue and are already rolling out improvements to strengthen the system.
All user assets remain safe. We’re focused on reinforcing stability and making the protocol even more robust. More updates coming soon.
SlowMist retweeted

We’re proud to co-found the Digital Asset Anti-Money Laundering Council (DAAMC) with @HashKeyGroup , @Beosin_com & @SlowMist_Team under HKVAIA’s support.
As a founding member, RD InnoTech is driving stablecoin compliance & financial integrity in Hong Kong. 🌐💡
#Stablecoin #Compliance #AML
