

Creator of Debloat and https://xitter.cf/t.co/tIYqmw6pxt Support: https://xitter.cf/t.co/l9kCPRoD2y Join the Debloat/CertGraveyard discord: https://xitter.cf/t.co/ZcWIqa6ZA9
The Cert Graveyard
Joined November 2020
- Tweets2.1K
- Following101
- Followers5K
- Likes12.9K






We updated the blogpost.
After the original post:
- I saw the malware in the network I monitor
- Others reached out to me to share TTP
- Others have published about it
- We've connected it to other signers and malware
All the signers have been added to CertGraveyard

Interesting malware signed “Guangzhou Guoying Communication Technology Co., Ltd.” and now revoked.
Functional PDF editor with backdoor. My report has 3 C2, but have seen more:
rogueauthority.org/quartzlin…

Trojanized PeaZip signed "Listenmaa Consulting Oy"
DLL swapped in for sideloading,
h/t @malwrhunterteam who found it while it was FUD on VT.
Certs been reported, getting detection now:
C2: apiupdated[.]com/Hrd50dFgjQW53n
157.173.16[.]197
rogueauthority.org/signed-pe…

Not malware analysis related, but still a project maintained with pride:
Tkinterdnd2 0.7.0
Adds better pyinstaller hook support.
Narrows the number of binaries it picks up and properly supports Tcl9.
github.com/Eliav2/tkinterdnd…

Signed "Lway Firmware" - 7th unique cert serial for them 🫥
h/t @malwrhunterteam
Microsoft teams lure -> BabaDeda loader -> CNCMachineRMS RAT
C2: wizardexpensive[.]com:
96.62.218[.]59
rogueauthority.org/signed-te…

Debloat 1.7.1 - github.com/Squiblydoo/debloa…
In 1.7.0, we added a "--no-extract" optional flag. This makes it easier to use Debloat in pipelines that expect only 1 item in return. Without it, it would extract NSIS installers automatically.
1.7.1 fixed the release bins for Tcl9

@malwrhunterteam shared two MSI installers with this signer "SOPHISTICATED SOFTWARES (PTY) LTD"
The first is a rust remote shell
rogueauthority.org/signed-wi…
The second is a tool which calls itself CrocoRAT:
rogueauthority.org/crocorat-…
We've seen CrocoRAT a few times 🧵

Some sample: https://updatestates.blob.core\.windows.net/files/WindowsDefender.msi
A file named "WindowsDefender.msi" coming from Microsoft's network, with no AV vendor detecting it on VT and was signed using an SSL Corp given cert with name "SOPHISTICATED SOFTWARES (PTY) LTD" must be legit, right?
😂
🤷♂️

PackClient RAT signed "Zaozhuang ZhongStore District HaoYouhao Department"
Kernel driver signed "Xidao E-commerce Studio, Yishui County"
rogueauthority.org/signed-si…
Payload: 108.187.43[.]139:8080/china4[.]zip
C2:
91[.]204.224.87:8790
156[.]251.16.214:8790
161[.]248.14.20:8790


As mentioned by @500mk500 , the ISO seems consistent with CastleLoader -> NetSupport (and StealC).
@malwrhunterteam 's thread already covered most of the details, the C2 and such. My AI analysis mostly connects the dots: rogueauthority.org/setup-iso…
CastleLoader: jumalputty[.]com
NetSupport: nizariuserp[.]com
StealC: crataga[.]site


Amazing: it somehow went from 1 detection on VirusTotal to 0
CertGraveyard volunteers report certificates for revocation, but in this case, the certificate was revoked before @malwrhunterteam shared it with us. We add it to our database and use these opportunities to investigate the malware anyway.
In his blogpost, @devmihaylov does an amazing job digging in and turning the malware inside out.
(Note: We can always use more volunteers to analyze malware, pivot on known bad indicators, tracking infrastructure and more. If you're interested, join the Discord and reach out: discord.gg/dvGXKaY5qr.)


Malware Analysis on a fake “Active Call” Python RAT
msvci[.]com/files/.ini - stage 2 download
45[.]61[.]139[.]149 - download server
g[.]obrn[.]cc - C2 (behind Cloudflare)
64[.]7[.]199[.]7 - operator server
medium.com/@devmihaylov/malw…
@SquiblydooBlog @malwrhunterteam

Though the domains sound cute… your enterprise network probably shouldn’t be reaching out to these.

Some other potentially related domains:
biggerworldclassstandard[.]com
maximalmaxing[.]com
sparksetuptechnology[.]com
supporterupdate[.]com
biggerskills[.]com
familypenguins[.]com
jumpingpenguin[.]com
hedgehogsbunny[.]com
lesliemonkeyinfants[.]com
commonhedgehogs[.]com
fastestsprints[.]com
babychimpserenity[.]com
RdViewer RMM tool that deletes itself, signed "温江区明宇网络技术服务工作室"
C2: 1[.]14[.]146[.]76
rogueauthority.org/signed-di…
h/t @malwrhunterteam

Gh0stRat variant signed "Zhengzhou Xiaoye Network Co., Ltd."
ca47e13a2980817e7849ddfef70312542ed11efaeba7b1b583161c06a440baf2
C2:
Primary: 103[.]82[.]53[.]214:7661
Backup: 103[.]82[.]53[.]214:80
rogueauthority.org/signed-se…
h/t @malwrhunterteam
Nice to see another analysis of Quartzline published.

(2/2) What we saw in real environments, plus IOCs, detection tips, and cleanup steps: expel.com/blog/quartzline-a-…
I never thought a malware with C2 like
tabbyottercub[.]com
motherotters[.]com
westbeavers[.]com
familypenguins[.]com
was going to be such a pain.
We've seen this family of malware going back several months, and I don't fully know what the end game is yet.
Interesting malware signed “Guangzhou Guoying Communication Technology Co., Ltd.” and now revoked.
Functional PDF editor with backdoor. My report has 3 C2, but have seen more:
rogueauthority.org/quartzlin…
Signed "FILIP KOZJAK" and added to the Cert Graveyard.
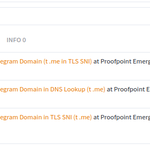
Regular reminder to be logged into VirusTotal even if it is a free account:
If you're logged in, it shows you Proofpoint's Suricata detection for the file reaching out to Telegram.


Analysts @HuntressLabs have been seeing an uptick of malicious MFA apps from the Microsoft Store the last few days. In some cases, they're being delivered via tech support scams through Teams, in others via malvertizing.
We've been digging into it, and hopefully we'll have more info soon.
Low detection Stealer, internally named "Zalmoxis".
Uses a signer that we've seen from two other CA: "YOUR CHANCE j.d.o.o."
ad0d08d54c9bbe2309bb7a8ae92def8a04297d0238f2799764d93929b57cbd5f
rogueauthority.org/signed-cr…
cdn[.]simplynetworking[.]eu
Zalmoxis c2: 45[.]152[.]149[.]66:6969
Panel was on port 3000
Previously seen signed as "Komers Trading Company LLC"
1534e8091708e13a24698de848faccac0ccbf82cc625f990bed0c7ec5388c345
h/t to @malwrhunterteam
We've seen this certificates for this signer issued by SSL, Sectigo, and GlobalSign


h/t @malwrhunterteam
Signed EtherRAT dropping signed StealC:
EtherRAT: 1b61b95a61996b44322e9841af2fa2b63fcdd18a569f16fa8acd30eb8d8ac854
Signer: "KARA-TASH I KO, OSOO"
StealC: 37d7a8c504227f9c1986619fd8148f1737cf94e56ac91687f8ba33be7e945f5e
Signer: "AirTiki ApS"
C2: presanis[.]com
Stealer Download: csg-soft[.]com / 45.135.180[.]185
StealC C2: glamour-studio[.]com / 194.11.226[.]153
This malware uses a non-functional captcha to distract the user. The installer is signed "HOLLIDAY DIGITAL LLC" and drops a trojanized aerodynamic design app signed by "Evelyn Paredes".
Both have been reported and added to CertGraveyard
rogueauthority.org/signed-in…
h/t @g0njxa


This file was mentioned in Google/Mandiant's report here: cloud.google.com/blog/topics…
Used in ShinyHunter's campaign against PeopleSoft.
The file is an updated version of SnappyClient. See the analysis of the file here: rogueauthority.org/light-all…


This is our second EV cert from "C&P Global Investors LLC" signing "BlackCrypt RMM". We're calling bullshit.
blackcryptknight[.]com, ws[.]blackcryptknight[.]com, devicehubcloud[.]com, apinetsolworkspace[.]network, 89.117.54[.]201
rogueauthority.org/blackcryp…


