

Cybersecurity Chronicles 🌐 | Breaking down the latest in security news, #hacking #darkweb #Cybersecurity #InfoSec #HackingNews
Planet Earth
Joined January 2024
- Tweets2.5K
- Following6
- Followers1K
- Likes34




The Hacker Wire retweeted

CVE-2025-54068 is the #React2Shell of the Laravel world.🚩
Just like Next.js Server Actions, Livewire bridges the frontend/backend gap automatically. But blindly deserializing state from the client? That leads to RCE.
👇Try the exploit via Vulhub: github.com/vulhub/vulhub/tre…
#Vulhub


The Hacker Wire retweeted

open-source-web-scanners
A list of open source web security scanners on GitHub and GitLab, ordered by Stars. It does not provide in-depth analysis - for more analysis or a wider range of tools.
github.com/psiinon/open-sour…
#cybersecurity #pentesting #bugbounty

The Hacker Wire retweeted

Here's my writeup on
auth bypass due to cache misconfig
severity: critical
bounty: 2000$
#BugBounty #bugbountytips #hackerone
link.medium.com/H1VkGzJlfMb

The Hacker Wire retweeted

POC for CVE-2024-7928: This exploit will attempt to retrieve DB details for FastAdmin instances.
github.com/bigb0x/CVE-2024-7…
#exploit #pentest #CyberSecurity

The Hacker Wire retweeted

So after reading docs and RFCs. I think this is how the CVE-2024-38063 exploit works. But it wont bluescreen my system.
Feel free to play around with this. (I may be way off the mark)
gist.github.com/nullenc0de/2…

The Hacker Wire retweeted
🚨Beware of Fake PoCs
As part of an ongoing personal project, I have been automatically monitoring GitHub for new repositories containing proof-of-concepts (PoCs) or exploits for recently disclosed CVEs.
This effort has led me to uncover several malicious GitHub repositories.👇


The Hacker Wire retweeted

CVE-2024-40617 - Fujitsu GW1500 M2M PrivEsc: SSH in as admin, perform path traversal, copy and modify /etc/passwd via FTP, replace it, log back in to gain root access. Patched in firmware V02L13C01A
PoC: github.com/KyssK00L/CVE-2024…
Writeup: link.medium.com/SLzpGgKWFLb

The Hacker Wire retweeted
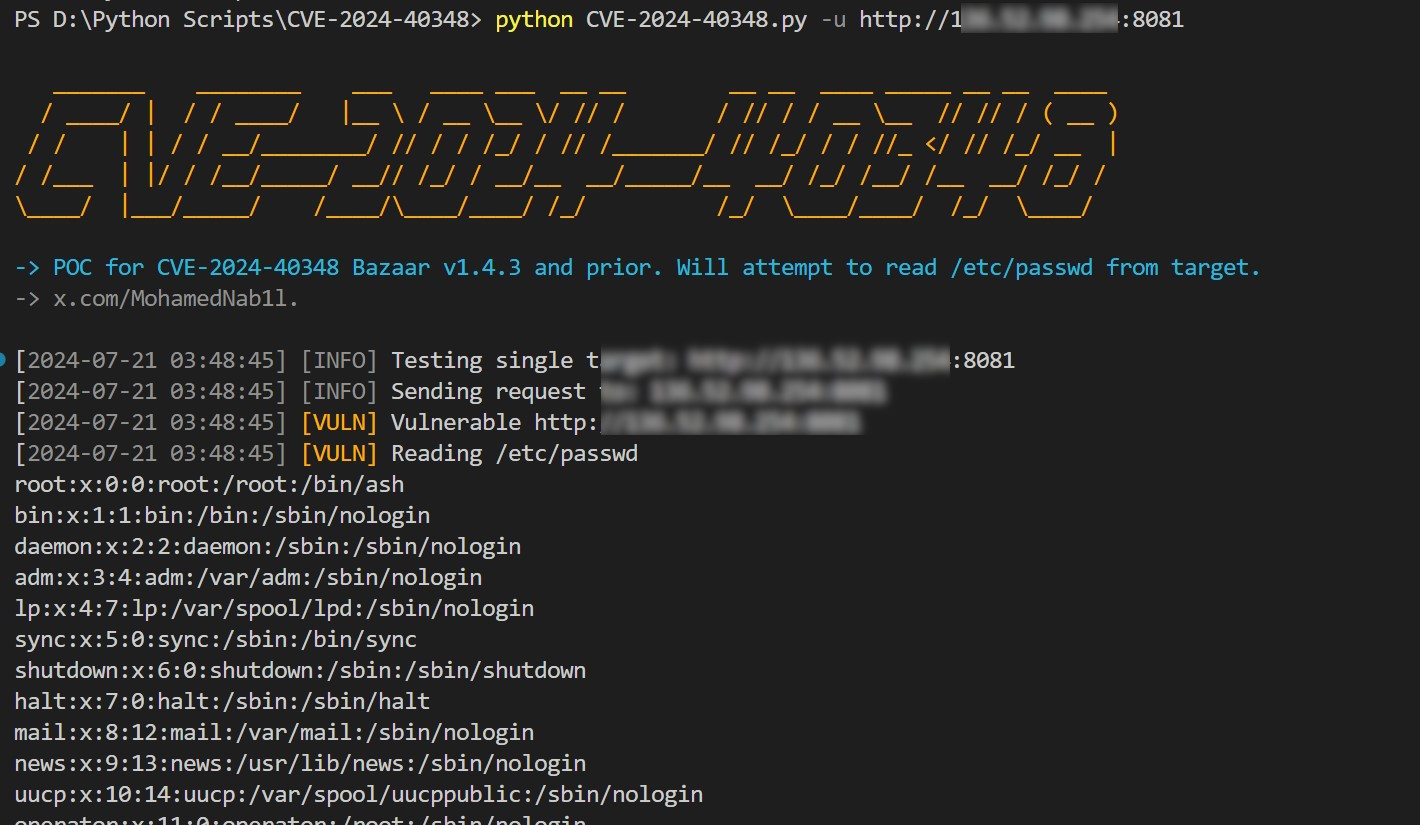
This is a bulk scanning and exploitation tool for CVE-2024-40348, Bazaar v1.4.3 and prior. Will attempt to read /etc/passwd from target.
github.com/bigb0x/CVE-2024-4…
#exploit #pentest #CyberSecurity
The Hacker Wire retweeted
Introducing a new OpenSSH bulk scanning tool! Quickly scan multiple SSH servers for vulnerabilities CVE-2024-6387, CVE-2006-5051, and CVE-2008-4109.
github.com/bigb0x/CVE-2024-6…
#CyberSecurity #OpenSSH #Vulnerability #InfoSec #NetworkSecurity #EthicalHacking

The Hacker Wire retweeted

🚨PoC Released🚨A signal handler race condition in OpenSSH's server (sshd)
github.com/zgzhang/cve-2024-…


⚠️⚠️ CVE-2024-6387: Critical OpenSSH Unauthenticated RCE Flaw ‘regreSSHion’ Exposes Millions of Linux Systems
🎯96.4 million+ Results are found on the en.fofa.info nearly year.
FOFA Link🔗: en.fofa.info/result?qbase64=…
FOFA Query: app="OpenSSH"
Refer🔖: securityonline.info/cve-2024…
#OSINT #FOFA

The Hacker Wire retweeted
POC for CVE-2024-34102. A pre-authentication XML entity injection issue in Magento / Adobe Commerce.
github.com/bigb0x/CVE-2024-3…
#exploit #pentest #infosec #hacking

The Hacker Wire retweeted

Today a group named 66slavs claimed to have breached the United States National Energy Research Scientific Computing Center (NERSC).
* We have not reviewed the data
* Yes, they watermarked a data breach


The Hacker Wire retweeted

#DataBreach Alert⚠️
🇸🇦#Saudi: Saudi Arabia Health Ministry Database Allegedly Breached
A hacker is allegedly selling stolen data from the Saudi Arabia Health Ministry. The data, supposedly from 2020 to 2024, includes:
- Personal information: names, addresses, phone numbers, blood types.
- Medical records: patient information, staff messages, emails.
- Sensitive access: ability to modify user accounts and access internal systems.
- COVID-19/My health/Seha data: infections, tests, recoveries, deaths.
- Patient details: names, ID numbers, ages, nationalities, genders, diagnoses, residences, and phone numbers.
The confirmation or denial of these claims has yet to be verified.
#dataleak


