

Building infrastructure for DeFi @finest_tokenize @BlockSign_io (Asset Operation & eSign & Verify/onboarding) @beginwallet, Cardano Ambassador, IANTD Cave Diver
Mos Eisley
Joined February 2021
- Tweets11.5K
- Following4.8K
- Followers2.8K
- Likes41.6K





Pinned Tweet
Five BlockSign products.
One trust platform.
Digital trust is not one problem. That is why @BlockSign_io is building one shared trust infrastructure across five products:
Asset Operations. eSign. Verify. CallShield. Verkauft!
Different products. Different markets. The same foundation: identity, authority, approval and verifiable evidence.
Built to be embedded into the workflows where trust actually matters.
Your assets. Your control.

This looks like a great treasury proposal!

Introducing PFMS: Bringing Government Scale Adoption to Cardano by Trivolve Tech
A Treasury proposal which brings massive scale real world adoption to @Cardano with its first user being an Indian state government. PFMS secures the entire Chain of Evidence on Cardano. The scale of the project is such that once it is deployed, it will become the largest government scale project ever on Cardano.
PFMS will be built as an open source public good for policing and justice systems worldwide.
What PFMS brings to Cardano with just the first deployment:
→ 1.53M + Cardano mainnet transactions in year one and rising every year as adoption grows.
→ Grows the current Cardano mainnet transaction metric by +18.2%.
→ ~5.1M DIDs across 3,500 facilities, 1.81M devices, 113,000 personnel and 3.2M evidence items connected to Cardano.
→ Cuts down case resolution time by 30% using Cardano.
→ Generates revenue through PFMS’s evidence verification service.
→ 70% of verification revenue returned to the Treasury, 20% to core Cardano library maintenance & 10% to Trivolve Tech.
→ Open source core (Apache 2.0) as a public good, designed for reuse across the world.
The ask: ₳9,600,000 over 15 months.
Here’s how we’re doing it 👇🧵

TIMxBRIDGE retweeted

Eine Unterschrift. Zwei Rechtsräume. Warum kann eine QES in der EU gültig sein, aber in der Schweiz oder UK nicht denselben Rechtsstatus besitzen?
Unser neuer Artikel erklärt eIDAS vs. ZertES, gesetzliche Grundlagen und reale Tests.


We are living in a great time. I like to be a tiny part of this evolution.


AI Agents Can Move Money. But Who Gives Them Permission?
AI agents are becoming economic actors. @IOHK_Charles explores this emerging AI economy in his keynote. Soon, agents won't just analyze markets. They'll manage wallets, execute payments and move stablecoins.
But who controls their authority?
BlockSign Asset Operations brings governance to digital assets. Automation needs authorization.
#Cardano #Nightframes #AI #Stablecoins @MidnightNtwrk
Back from a longer weekend. Battery is fully charged again! I need the energy for the coming days, since they'll be crucial for the team and me.
I'm optimistic that we, as the @blocksign_io team, will take an important step in the next three months that will also be of interest to other #Cardano projects.

When it comes to crypto taxation, Germany continues to set the benchmark in Europe. 🇩🇪

Wie erwartet wurde der Gesetzentwurf der Grünen zur Abschaffung der einjährigen Haltefrist bei Kryptowährungen mit 445 Nein- gegen 132 Ja-Stimmen gestern abgelehnt. Alle 198 anwesenden CDU/CSU-Abgeordneten stimmten dagegen. Auch die SPD lehnte den Entwurf ab. Ob die CDU/CSU auch den Regierungsentwurf von Lars Klingbeil ablehnen wird, bleibt offen bundestag.de/parlament/plenu…

TIMxBRIDGE retweeted
Wie bezahlen KI-Agenten und wer bestimmt ihre Befugnisse? Am Beispiel @Cardano zeigt BlockSign, wie Stablecoin-Zahlungen mit klaren Mandaten, Budgets und Freigaben funktionieren können. Denn ein Auftrag ist noch keine Zahlungsfreigabe.


TIMxBRIDGE retweeted
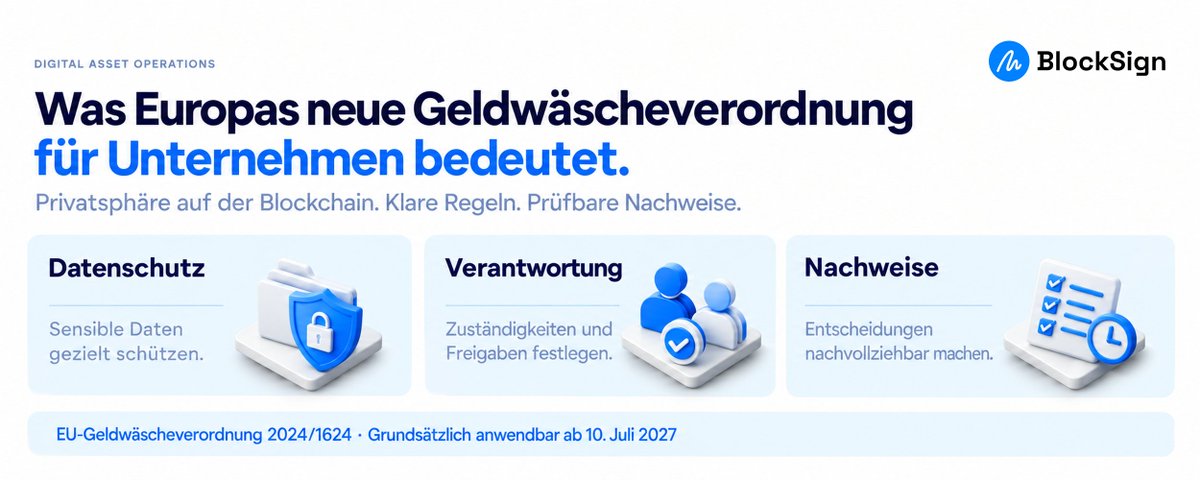
Vertrauliche Blockchain-Transaktionen, klare Kontrollen: Was Artikel 79 der EU-Geldwäscheverordnung regelt, wie Zero-Knowledge-Proofs helfen und wie BlockSign die Umsetzung unterstützt.
#DigitalAssets #Privacy
The AI investment thesis is becoming wonderfully convenient: assume extraordinary demand, borrow against it, and let future customers sort out the details.
Build enormous data centres. Commit to years of infrastructure spending. Price the company as though today’s benchmark lead guarantees tomorrow’s market dominance. What could possibly require a sensitivity analysis?
Competition, perhaps. A better model can weaken your advantage. Cheaper open-weight alternatives can put pressure on your pricing. Customers might even have the audacity to choose whichever model delivers the best result at the lowest cost.
Very inconsiderate of them.
Meanwhile, financing costs follow their own schedule. If a data centre is delayed by power shortages, permits or construction problems, lenders are unlikely to accept “AGI is coming” as an interest payment.
And moving financing into a special-purpose vehicle? That can redistribute risk. It cannot manufacture customers. Financial engineering remains disappointingly unable to turn an empty server hall into operating cash flow.
AI could become essential infrastructure and still deliver brutal losses for investors who paid too much, borrowed too heavily or assumed competition would politely disappear.
For businesses adopting AI, the opportunity is substantial. For those financing the buildout, the question is painfully conventional: who will pay, how much, and will the margins cover the investment?
The revenue is a forecast. The debt is a contract. Happy Sunday!

That’s quite cool! Well done @Cardano_CF
Learn to build a Cardano app with an AI agent.
The Cardano Academy's new course, Agentic Coding on Cardano, is live.
This free course teaches you to direct an AI agent, audit its code and prove each result on testnet.
Time to build the agentic way.
cardanofoundation.org/en/aca…

TIMxBRIDGE retweeted
CIP-113 is moving from specification to operations. And that’s where things get interesting.
At BlockSign, we have now successfully executed a governed programmable-token lifecycle on Cardano Preview:
→ Registration + initial mint
→ Separate mint
→ Wallet-to-wallet transfer
→ Burn
All confirmed on-chain. But making a transaction work is only half the challenge. Institutional operations need to answer different questions:
- Who is allowed to initiate it?
- Who must approve it?
- What exactly was approved?
- Can the transaction change after approval?
- Who can execute it?
- And can all of this be proven afterwards?
That’s why BlockSign separates:
Intent → Build → Validate → Approve → Execute → Confirm → Evidence
❗️Changing the transaction means changing the approval.❗️
This week, CIP-113 builders are meeting to discuss improvements to the emerging infrastructure. Our testing is already producing concrete operational learnings around governance, transaction flows and the requirements for using programmable tokens in real-world environments.
The next step is bigger than minting tokens. It’s making programmable assets operationally ready for institutions.
@planetmaaz @michaeldotada @Cardano

Cardano has a regulated-asset interoperability problem we need to solve.
CIP-113 enables programmable assets. But if every regulated stablecoin comes with its own compliance and transaction logic, wallets, DEXs, exchanges, custodians and infrastructure providers may have to integrate each asset individually.
That doesn’t scale.
PR #1266 addresses this for regulated stablecoins by exploring a shared standard for capabilities such as mint/burn, freeze/seize, roles, key rotation, upgrades and redemption.
But the underlying question goes beyond stablecoins.
The same challenge will increasingly matter for RWAs, tokenized commodities, securities, funds and other regulated assets.
If Cardano wants to become serious infrastructure for institutional assets, interoperability must be designed in from the beginning, not retrofitted later.
PR #1266 is still a proposal. That makes NOW the right time to get involved.
Builders. Issuers. Wallets. DeFi protocols. Custodians. Institutions. ➡️ Read it. Challenge it. Contribute.
👉 GitHub PR #1266:
github.com/cardano-foundatio…
This discussion could become very important for Cardano’s institutional future.

TIMxBRIDGE retweeted

Smart Contract Security, and Continuous Auditing - Why One Check Is No Longer Enough xitter.cf/i/broadcasts/1NxaroOqL…

TIMxBRIDGE retweeted
Shamir or FROST? The right architecture depends on how you use your assets.
Over the last posts, we looked at two approaches to distributed key management: Shamir Secret Sharing and FROST threshold signatures.
Both can remove dependency on a single keyholder. But they solve different operational problems.
Shamir is fundamentally simple to understand: split a secret into several shares and define a threshold — for example, 3-of-5.
When recovery is required, enough shares are combined and the original secret can be reconstructed.
That makes Shamir particularly interesting when the main objective is secure backup and recovery. A single asset owner can even distribute their shares across separate secure locations.
The trade-off comes when the key needs to be used. Once the threshold is reached, the complete secret can exist again during reconstruction. The reconstruction environment therefore becomes part of the security model.
FROST approaches everyday operation differently.
Again, participants hold shares of a common signing key and a threshold can be defined. But during normal signing, the required participants cooperate to create signature shares. Those are combined into one valid Schnorr signature — without reconstructing the complete signing key.
That makes FROST particularly interesting when distributed control is required not only for recovery, but for regular transaction signing.
So which is better?
There is no universal answer.
For an individual investor or single high-value trader, Shamir can offer an understandable way to distribute recovery material and avoid keeping one complete secret in one location.
For a family office or small organization, the decision increasingly depends on operational requirements. Is distributed control primarily needed for disaster recovery, or should several people participate every time important assets are moved?
For SMEs, institutions and professional asset operations, FROST can become particularly interesting where multiple authorized participants should jointly sign transactions without reconstructing the complete signing key during normal operation.
And there are more questions than security alone:
- How easy is the initial setup?
- How does recovery work?
- How convenient is everyday signing?
- What happens when a participant leaves?
- How are shares replaced or refreshed?
- What happens if participants are unavailable?
- Which blockchains and signature schemes are supported?
- And how does the cryptographic threshold connect to the organization’s actual governance?
That last question is crucial.
A 3-of-5 cryptographic threshold does not automatically tell you who is allowed to initiate a €5 million transaction, which assets they may move, which addresses are permitted or what transaction limits apply.
That is governance.
With BlockSign, organizations can choose a key-management architecture that fits their operational and security requirements and combine it with roles, approvals, policies, transaction limits and audit evidence.
Shamir distributes the secret.
FROST distributes the signing process.
BlockSign adds the governance around it.
Not sure which architecture fits your digital asset operations? Talk to us.
🤖 Made with AI

What if you could sign with a private key, without ever bringing the complete key back together?
That is the idea behind FROST (= Flexible Round-Optimized Schnorr Threshold) Signatures.
Imagine a 3-of-5 setup. Five participants each hold a secret share of a common signing key. At least three must cooperate to create a valid signature.
But unlike the reconstruction process we described in our Shamir post, the participants do not need to combine their shares to reconstruct the complete private key before signing.
Instead, each participating signer uses its own share to produce a signature share. Once the required threshold participates, those signature shares are aggregated into one valid Schnorr signature. The complete group signing key does not need to be reconstructed during normal signing.
This removes an important risk: there is no moment during normal signing when the complete private key needs to be brought together in one place.
And compromising a single participant is not enough. An attacker would need to compromise enough signing participants to reach the defined threshold.
But cryptography alone is not governance.
FROST can enforce that, for example, 3-of-5 cryptographic participants must cooperate. BlockSign adds the operational governance around it: who may initiate a transaction, who may approve it, which limits apply and which assets or addresses are permitted.
With BlockSign, organizations can choose the key-management architecture that fits their security and governance requirements, including Shamir-based and FROST-based models.
Shamir can reconstruct the secret.
FROST creates the signature without reconstructing it during normal signing.
In our next and final post in this series, we’ll put Shamir and FROST side by side and explain when the differences matter.
Want to discuss which key-management architecture fits your digital asset operations? Talk to us. DM us.

