
Private account. #malware analyst with 20+ years of experience Low and high programmer. All opinions here are mine.
Spain
Joined April 2017
- Tweets1.6K
- Following328
- Followers2.6K
- Likes2.3K



As always, be cautious with repositories that claim to be one thing but turn out to be malware.
🔗 Suspicious Repository: github.com/Xalyndarjg/Mev-Bo…
⚠️ Claims to be a Solana MEV bot but is actually a Solana Drainer.
🚨 Key Findings
🕵️ Hidden Attacker's Wallet
The function getApiPumpFUNHex() is highly suspicious because a legitimate bot does not need to hide wallet information:
* The function decodes a Base64 string into a hexadecimal value.
* The result is converted into a Base58 public key, likely the attacker's wallet.
* Confirmed Drainer Address: FuYYZ3yL59YDyLJEDQ4k258Z8BNMpqNpLwgyxnyxy2Ak

ALT Drainer wallet encoded in base64
1
1
568
🚨 Unauthorized Fund Transfers
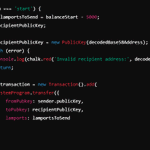
The apiDEX function contains malicious behavior during the "start" action:
The script retrieves the victim’s wallet balance.
✅ It deducts 5000 lamports (~0.000005 SOL, transaction fee).
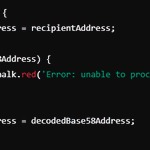
✅ It transfers all remaining SOL to the attacker’s wallet (recipientPublicKey).
✅ The user has NO control over the recipient address.
🚨 This proves the bot is a drainer and has no real MEV functionality.

1
211
🎭 Theft Disguised as Withdrawal
The withdraw function steals funds when a user attempts to withdraw:
If the user withdraws 0.1 SOL or less, the funds go to their intended recipient.
✅ If they withdraw more than 0.1 SOL, the money is redirected to the attacker's wallet.
✅ This is a classic scam technique, allowing small test transactions to succeed while larger withdrawals are stolen.

1
157


Valthek retweeted
On December 19, more than a terabyte of data from Insomniac Games was released after a ransomware attack, reportedly by the Rhysida Ransomware gang. For context on the group & a previous incident, read from @Libranalysis, @valthekOn, & @LeandroNVelasco. bit.ly/41tk0zx

Valthek retweeted

Trellix's Alexandre Mundo (@ValthekOn), Max Kersten (@Libranalysis) & Leandro Velasco (@LeandroNVelasco) analyse a Rhysida ransomware attack, detailing the malware operator’s techniques. trellix.com/en-us/about/news…

Valthek retweeted

My most recent blog for @Trellix, written with @ValthekOn and @LeandroNVelasco, covers the Rhysida ransomware's inner details, along with an anonimised incident response case: trellix.com/en-us/about/news…