

rebuilding https://teapawt.net/t.co/oFH3BQm9YZ and creating zseano methodology v2. *COMING SOON!!* ex full time amazon hacker 2018-2026 🫡
Joined February 2012
- Tweets7.7K
- Following722
- Followers83.6K
- Likes10.7K






zseano retweeted

hackers: can't stop, won't stop
Six months in and no signs of slowing down. High & Crit findings now at 39% of the total with slop continuing to decline.


zseano retweeted

I gave a talk at @BSidesSF on hacking Google Groups at enterprise level. Check it out: youtube.com/watch?v=OF20oFJ_…
#googlegroups #ophionsecurity #research

zseano retweeted

Earlier this year, I hacked a major automotive company with @samwcyo. We were able to remotely unlock cars in the AU and US. My writeup for AU is here: shubs.io/unlocking-any-car-f… and our writeup for the US here: samcurry.net/forgerock
zseano retweeted

Had some time off of work and was finally able to release a few blog posts: the first is about an RCE on ForgeRock that allowed us (@infosec_au) to remotely send vehicle commands for two automakers using only a customer's name, email, or phone number: samcurry.net/forgerock

zseano retweeted
I built a new tool called Frag. A CSS-only token exfiltration tool. No JavaScript needed. Inject a stylesheet, steal the token. Uses De Bruijn graphs to reconstruct secrets from overlapping CSS attribute selector fragments. Built on research by me and @Alex_______C Source: 👇

zseano retweeted

*sshole is out
if you run sshd on alpine, openwrt or any musl box with password auth on: update now
official writeup: sshhole.com

zseano retweeted

Just dropped a new blog post! 🔥
blog.orange.tw/posts/2026-10…

The new bugbountyhunter site is *hopefully* going to be publicly released next month as I do some final touches, which means yes, zseano methodology v2 will be dropping before Christmas ;)
So much work has gone into this and I hope to continue helping people on their bb journey!
Expedia Group Program has gone from $21k bounties paid to $250k in just 2 months. Seems people are making good $$$ here: hackerone.com/expediagroup_b…
@m0chan98 is leading rep in last 30 days
(it will be interesting to log data for 1year+ to see what's happening across programs)


zseano retweeted

Our security research team discovered a cross-site scripting vulnerability in Cloudflare's /cdn-cgi/image/ endpoint by chaining an SVG sanitizer bypass with a new Cache-Control header trick to bypass the CSP. The issue was reported to Cloudflare and has since been fixed.
You can read more here:
slcyber.io/research/cache-me…
zseano retweeted

Kudos to @GeminiApp, @php_net Core, @OpenAI, @calif_io, & partners for coordinated disclosure.
👇 Full breakdown & PoC: wiz.io/blog/php2shell-php-rc…

pay attention bug bounty program owners.
if your top hackers are walking away and not submitting anything anymore, then you have failed somewhere.
(although let's be honest.. these days *most* programs don't actually care if people stop submitting. they're like "okay w/e")


92% of 77 CTBBP researchers surveyed have stopped or reduced submissions due to poor program experiences.
Fair treatment ranked above bounty size when choosing a new program.
Our new research with @ctbbpodcast:
The Researcher Attention Problem
bugbountymaturity.com/resear…

zseano retweeted
You can now perform content discovery at 100k requests per second with h3fuzz on http/3 hosts (fork of ffuf with http/3 support).
Tool here: github.com/assetnote/h3fuzz
Research post here: slcyber.io/research/how-prac…
non hacking post, but did anyone here ever do Halo2 Superbouncing? then Halo3 came out and the bouncing era ended as it didn't work anymore.
Well thanks to AI, 22 years later.. superbouncing on Halo 3, ODST and Halo: Reach has been unlocked
youtube.com/watch?v=zPGxUCEd…
Mindblown.
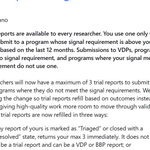
1 month to triage which then burns one of your trial reports. imagine you report 3 valid bugs, but no one touches 'em for 1month++. and then you find more bugs.... but you can't submit them. what then?
there is a better solution than all platforms adding submission limits imo


zseano retweeted

I got $90,000 for a RCE in Google.
simonkoeck.com/writeups/goog…

zseano retweeted

Bug bounty queues are drowning in AI-generated reports. Platforms, programs, triagers and researchers all pay for it.
So we're open-sourcing the triage skill we use internally @BugBunny_ai to filter out false positives and non-actionable reports. It does two things:
1. Validates the report with an end-to-end test
2. Escalates valid bugs to their highest defensible impact, e.g. a DOM XSS pushed to full account takeover
Every report gets a verdict:
🟢 Green: validated end to end, ready to submit
🟡 Yellow: more work needed first
🔴 Red: do not submit
github.com/Sequester-AG/bug-…
