

@ApacheArrow / Databases / Compilers. (past @SDFLabs, VoDa, @Spotify). Rust/C++/TLA⁺🇧🇷 → 🇸🇪 → 🌎
Joined June 2008
- Tweets29.5K
- Following2.6K
- Followers5.8K
- Likes42.4K
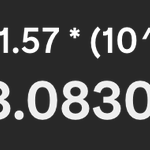






If you could store one private key per proton in the universe (you can't), you would only be able to store 2^263 keys (log_2(Eddington Number)~=263). A truly random 384-bit key has never been written down or appeared anywhere in the universe. But sure, pick the number 4.

Very pretentious from eMudhra’s part to say they *chose* to leave the business. The business is trust and they can’t be trusted. There is no business for them anymore.

This is the most recent one. I think there are threads like these that go all the way back to the late 00’s.
bugzilla.mozilla.org/show_bu…
This CA debacle reminds me of Mozilla simply refusing to take SERPRO (a technical Brazilian agency) seriously in its attempts to add itself as a root CA.

