
maldev hobbyist. glasses. mustache.
Joined October 2019
- Tweets101
- Following272
- Followers650
- Likes1.3K







Christian W retweeted
Hacking is boring.
Wanna know what's fun? Browsing MSDN documentation at 2 o'clock in the morning, looking for APIs to potentially abuse in malware. It'll also probably never go in the wild and it'll go unappreciated for several months or even years.
That's where the fun is
Christian W retweeted

Happy to get this out the door: cloud.google.com/blog/topics…
Big thanks to @onfvp @jinx_soda @nicastronaut and the other named and unnamed authors.
A few highlights ⬇️

Christian W retweeted

I'm exited to release GraphStrike, a project I completed during my internship at @RedSiege. Route all of your Cobalt Strike HTTPS traffic through graph.microsoft.com.
Tool: github.com/RedSiege/GraphStr…
Dev blog: redsiege.com/blog/2024/01/gr…
#redteam #infosec #Malware #Microsoft

So more MATLAB stuff. I managed to get this loader working as a standalone executable and learned a few things during the process that I thought I'd share.
1/?


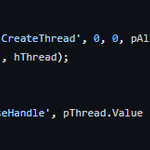
- MATLAB Coder doesn't like loadlibrary()/calllib(). Instead I had to use "coder.cinclude(<header>)" and "coder.ceval(<api>, <arg1>, <arg2>, ...)" in order to leverage Windows APIs.
Example:
hThread = coder.ceval('CreateThread', [], 0x0, hAlloc, [], 0x0, []);
3/?
1
2
391


90 therapeutic shellcode execution methods for the soul
github.com/Wra7h/FlavorTown/…

Christian W retweeted

I'm VERY HAPPY to say that my Blogpost is out!!!!
As a content, we'll discuss about how to exploit a simple (not so much) TypeConfusion vulnerabilities in a modern windows versions (Windows 11 22621).
Now let's get our SYSTEM privileged shell!
wafzsucks.medium.com/how-a-s…

Christian W retweeted
Zero day summer continues, late Friday blog release because the baddies never sleep. mandiant.com/resources/blog/…

Christian W retweeted

[Blog] No Alloc, No Problem: Leveraging Program Entry Points for Process Injection
An analysis of AddressOfEntryPoint and the 'new' ThreadQuerySetWin32StartAddress (ThreadQuery) process injection techniques
bohops.com/2023/06/09/no-all…

Christian W retweeted

"Mandiant has observed wide exploitation of a zero-day vulnerability in the MOVEit Transfer secure managed file transfer software for subsequent data theft."
UNC4857 observed actively deploying the LEMURLOOT webshell post-exploitation.
mandiant.com/resources/blog/…

The ol' "process injection that stomps ExitProcess() to execute shellcode instead of actually exiting" trick.
gist.github.com/Wra7h/0bfa02…
Probably been done before, but I thought it was cool. Notes and reference included in gist.