

CVE-2026-64861 | Security Engineer | Bug Bounty Hunter
Joined June 2022
- Tweets963
- Following320
- Followers2.2K
- Likes13.2K




Pinned Tweet
Secured the #24th spot on the MSRC’s 2023 Q4 Leaderboard! 🚀🏆
Check out Microsof Leadboard: msrc.microsoft.com/leaderboa…
#Microsoft #BugBounty #ethicalhacking #hacker #PenetrationTesting #Pentesting #Cybersecurity #infosec #infosecurity

🚀 Excited to be featured in HackProve Security Roundtable!
Sharing practical insights on recon, hidden APIs, vulnerability research, and bug bounty hunting.
📅 November 12 | 12:30 UTC
📍 Live on Discord
See you there! 🔥
#BugBounty #CyberSecurity

🚀 How to Approach Real-World Targets & Identify Attack Surfaces
Join us for the first episode of "HackProve Security Roundtable", featuring Muthu D, an MSRC (Microsoft Security Response Center)-recognized security researcher, with recognition from Microsoft, Apple, Google, GitHub, and Cloudflare.
In this session, Muthu will share practical insights and approaches to:
🔍 Reconnaissance & Attack Surface Discovery
🌐 Hidden APIs, Assets & Endpoints
🛡️ Manual Vulnerability Research
⚡ Business Logic & Authorization Testing
🎯 Real-World Bug Bounty Hunting – Applying effective techniques to real-world targets.
Whether you're an experienced bug bounty hunter or looking to sharpen your security research skills, this is a session worth joining.
📅 November 12, 2026 | 12:30 UTC
📍 Live on Discord
👉 Join the conversation: discord.gg/uTpCaCD4S8
#BugBounty #Cybersecurity #VulnerabilityResearch #AttackSurface #HackProve

There's a new version of this post
1
160
Dear @SBICard_Connect @TheOfficialSBI ,
Five international debit card refunds worth $411 are still missing despite the merchant confirming successful processing and providing ARN references.
The promised 7 business days have passed. Multiple follow-ups, but still no resolution.
2
3
1,271
Is this what grievance redressal means, SBI?
How long does a customer have to chase their own money?
1
1
82
Not even the bank manager or customer support team seems to know how to trace an ARN. Then who is actually handling these refund complaints?
@TheOfficialSBI @SBICard_Connect
1
51


Excited to start this new journey with @Yalla_Hack
Thankful for the opportunity and trust 🙌

We’re thrilled to welcome @_anonysm to the @Yalla_Hack team as our new Senior Security Analyst!
Muthu has already made waves in the cybersecurity community from uncovering critical bugs in @Microsoft platforms to contributing to security advancements at @Apple .

Muthu D retweeted

We’re thrilled to welcome @_anonysm to the @Yalla_Hack team as our new Senior Security Analyst!
Muthu has already made waves in the cybersecurity community from uncovering critical bugs in @Microsoft platforms to contributing to security advancements at @Apple .
Grateful to GSDC for recognising me as a Knowledge Advisor and awarding the Certificate of Achievement for my ISO 42001 & ISO 27001 session. ✨
#bugbounty #cybersecurity


Saw the love & negatives. Just to clarify my intention:
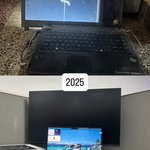
This is to inspire anyone with an old laptop - even a 10-year-old machine can do bug bounty.
Mac isn’t a downgrade, I switched as I’m focused on Apple BBP. And no, I’m not selling any course 😅 Just sharing my journey.

Bug bounty gave me more than money.
It gave me the power to choose and afford my life.
Grateful to the programs that made this real 🤍
#bugbounty #cybersecurity

Bug bounty gave me more than money.
It gave me the power to choose and afford my life.
Grateful to the programs that made this real 🤍
#bugbounty #cybersecurity

After a long time, a fast accept from Google! ⚡
Business Logic Flaw accepted in just 4 days.
#GoogleVRP #BugBounty #InfoSec

1
94
4,165

Another issue I reported to Apple BugBounty Program got fixed ✅
Bug bounty is funny sometimes—you report & forget… then one day, during a low phase, you get an update that reignites hope ✨
#BugBounty #AppleSecurity #Infosec

1
34
3,382

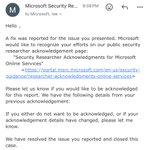
Found & reported a critical Azure vuln — exposed service principal creds → admin-level access, full app control, & privilege escalation.
MSRC rated it moderate but fixed it in 20 min. No bounty, but a win for cloud security .
@msftsecresponse
#BugBounty #InfoSec #Hacking

Honored to be recognized by the @hackprove_ Team with a Certificate of Appreciation for sharing my experience in the webinar “How I Earned $10,000 for a Single Vulnerability from Microsoft”.
#BugBounty #CyberSecurity #Pentesting

Just randomly checked my Apple Security portal and realized I was awarded a bounty—$$$$ for reporting a security issue! Didn’t even notice the email from 3 weeks ago.
#bugbounty #infosec #securityresearch
