





Pinned Tweet
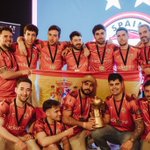
We won the @Hacker0x01 Ambassadors World Cup for second time. 🏆
🧵 This is thread about my journey, and how it all started 8 months ago when I had 0 points on HackerOne ⬇️


remot3 retweeted

A newly disclosed Exim vulnerability, CVE-2026-45185 (“Dead.Letter”), highlights how a flaw in handling SMTP BDAT commands and TLS connection termination could create serious security risks in widely deployed email infrastructure.
As covered by Ravie Lakshmanan in @TheHackersNews, the vulnerability was discovered and responsibly reported by XBOW.
The flaw affects GnuTLS-based Exim builds and could enable heap corruption and potential remote code execution through BDAT message handling during TLS shutdown. Research like this reflects the depth of analysis required to uncover high-impact vulnerabilities before attackers do.
Read the full article: bit.ly/4nzv60T

remot3 retweeted
Anthropic’s Mythos raised the bar for AI vuln detection but kept it invite-only.
GPT-5.5 is OpenAI’s answer, and it’s open to all.
We had early access. Ran the benchmarks. Blackbox GPT-5.5 already beats whitebox GPT-5.
Best pentesting model we’ve tested.
Read our analysis: bit.ly/48OX7v6
Everyday I read about a new autonomous pentesting tools being released. All of them follow the same pattern. Some sort of agentic architecture with hacking tools connected and benchmarked against a vulnerable app.
Let me explain you why these systems are useless 👇
4. Without validation you will drain in noise.
5. Most of these tools delegate auth on the agent gambling if the test will pass it or not. Also multi-agent systems will kill eachother sessions while testing in parallel
Back on top of the leaderboard for another year at @RootedCON x @intigriti hackernight!

remot3 retweeted
Most IDORs aren’t “guess the next number.” They hide in real authorization logic.
In our latest Tales from the Trace, XBOW uncovered two zero-day IDORs by reasoning through the app like a pentester, even after 403s and 502s.
The future of DAST lies in autonomous reasoning, catching the real-world access control failures scanners miss (and attackers look for): bit.ly/4kmlmpg

Hate when I am deep down on a bug after researching it for days thinking I'm a genius for reversing it just to discover another asset that reveals the entire internals
remot3 retweeted

Thanks to everyone who joined us at the @Hacker0x01 Brand Ambassadors Speed Show&Tell in Madrid, and special thanks to all who presented! 💕


remot3 retweeted

🚨 180+ vulnerabilities found.
🌍 763 hackers. 38 countries.
🏆 4 elite teams.
Adobe brought serious energy to the 2024 #AmbassadorWorldCup, working side-by-side with ethical hackers to secure products like Firefly & Lightroom.
We were proud to host → adobe.ly/4m3D1C8
#HackForGood #TogetherWeHitHarder
Isn’t it terrifying that a single person (Satoshi Nakamoto) could trigger a crash rivaling the dot-com bubble or the 2008 housing crisis… just by dumping all his Bitcoin at once?
I've been binging @DarknetDiaries lately. If you don't know the podcast you are missing out. @JackRhysider storytelling keeps you hooked to the story even if you know it. Would be amazing to see it integrated into @BallenStudios so I have all my favourites in one place
In the age of AI pentesting, models will need of new researches to nurture from. LLMs lack the ability to develop complex novel techniques without guidance. And fully autonomous research won't be possible without human guidance for a long long time.
