

seceng @monad | grew @Spearbit @Cantinaxyz | ex seceng @Coinbase
nyoooom
Joined September 2020
- Tweets2.5K
- Following3.9K
- Followers10.2K
- Likes5.5K




endgame blockchain

Quantum-resistant consensus without sacrificing performance
Another big step toward a post-quantum future from @category_xyz
Monad is necessary

I am a technology optimist. I believe:
1. decentralization and censorship-resistance (real versions of these properties, not larps) matter to human freedom in the coming age of AI
2. self-sovereign money, implemented by code and maintained through decentralized consensus, is the final form of money. But it needs to be truly decentralized -- cut out every possible weakness, trust assumption, keeper, etc. Of course there will be connectors to the real world - harden those maximally
3. AI will write most smart contract code. Spec-driven development with Formal Verification will be how new contracts are written rigorously. FV will also be crucial to securing all the infra including the blockchain itself
4. AI will harden our surfaces, with some unfortunate hacks in the process, but ultimately the crypto and financial industries will come out stronger
5. properly-constructed and properly-indexed data lakes will enable agents to build software far more productively
6. governments will move to restrict AI usage in the future, causing true decentralization and CR to matter in dramatic fashion
7. quantum security will be a must for any ledger where people trust their assets. And specifically, blockchains will need to deliver quantum-resistance while retaining programmability and performance. Again, no larping
8. ZK will be an important part of the puzzle too, as it'll be increasingly important to prove off-chain computation and utilize the result on chain. But again, performance and effortlessness for users will be the differentiator
9. pragmatic and composable privacy will be the missing piece for real adoption. People will use apps that stack together stablecoins, DeFi, blockchain settlement, passkey or MPC authentication, and friction-free onramps, but the part that gets fintechs over the line is knowing that user balances will remain private while still being able to tap into shared liquidity
10. blockchain will serve as the global, universal marketplace, for anyone anywhere to get the best opportunities. For that we will need guarantees of fair execution, protection from frontrunning, and a convergence of all of the best assets
At @category_xyz and the @monad Foundation, we are assembling all of these missing pieces in parallel with extreme urgency, and I hope this is clear from our actions. See you in the future
Omar (mainnet arc) retweeted

After the week we’ve just had, DeFi and blockchain protocols need internal security more than ever
This was just a preview. We are going to see a lot more vulnerabilities and incidents in the coming months
Time to build your in-house security expertise

Most protocols spend a lot on audits and bug bounties but have zero internal security
Launching whohassecurity.com to highlight the ones that do
Having an internal security team should be in every protocol's New Year's resolutions for 2026
Omar (mainnet arc) retweeted

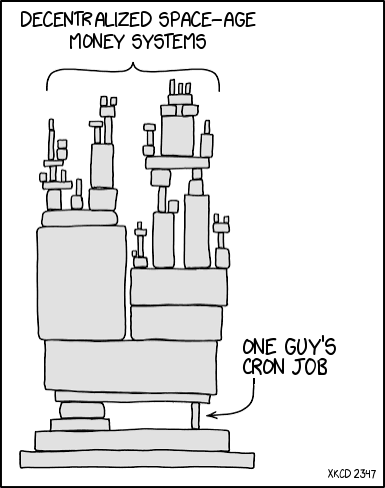
Yesterday's Railway issues, and an increasing stream of cloud provider incidents, highlight a major issue: decentralized apps have no way of scheduling or automating smart contract calls. Someone needs to run that cron on a server, which are becoming increasingly unreliable in the age of AI.
The point of decentralized systems is that we shouldn't need to rely on a single server to maintain an invariant that protects the correctness and solvency of self-sovereign money protocols. Automation needs to move to the blockchain, where a network of distributed nodes brings fault-tolerance and checks-and-balances.
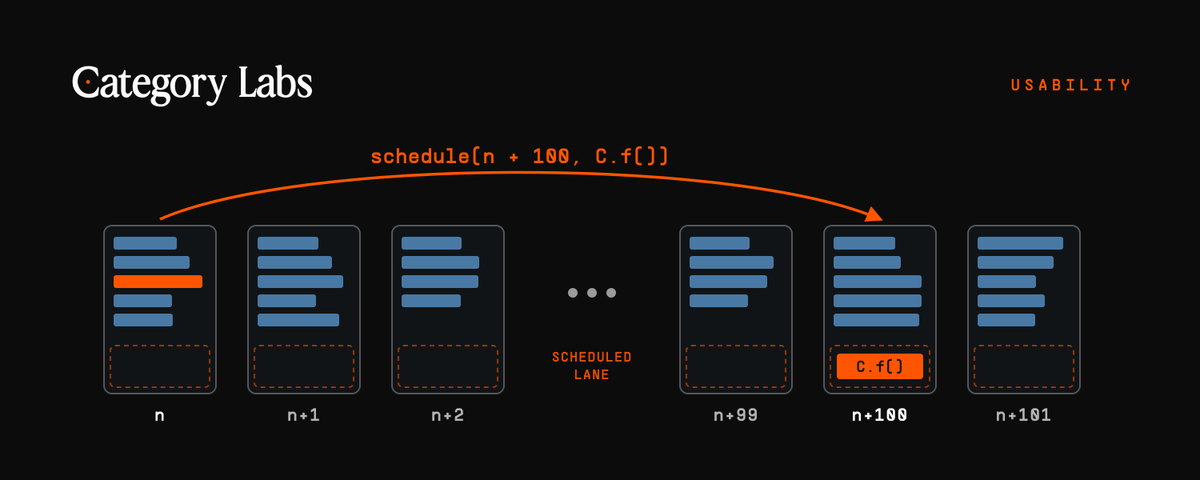
Scheduled Transactions are how we accomplish that.
Scheduled Transactions are far more than a replacement for keepers. They let users and applications alike set up interactions that recur on a cadence, happen once at a chosen moment, or follow from something that happened earlier.
Check out the details below, as well as a few examples of what you can build with Scheduled Transactions, such as on-chain keepers, recurring payments, long-running (asynchronous) computations, automatic refunds in atomic swaps, and order-book cleanup.

If you’re in cyber and you feel like giving up I’m sorry but I do not understand.
Most electric time to be in this industry and make a mark.
We have progress to make and hard problems to solve.
Chew glass. Breath smoke. Ride the tiger. Lan Jiao. Gmonad.
(I am sleep deprived)
Omar (mainnet arc) retweeted

a few security-related things that I believe are not even close to being solved by AI
- opsec
- monitoring
- understanding
- incident response
Crypto teams please patch Telegram Desktop on employee devices and have your employees do the same on their personal devices.
< 7.2.9 is vulnerable to possible session takeover + file exfil


Telegram Desktop: one-click account takeover via IPC injection
beaksec.github.io/posts/tele…

If there’s a single team of people I’d want to be tackling the hardest problems facing blockchains.
It’s @category_xyz


Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
Omar (mainnet arc) retweeted
Today we are announcing Monad Private Settlement, which gives banks and enterprises the best of both worlds: sovereign execution environments with privacy and compliance by default, which benefit from the composability and performance of Monad
Monad Private Settlement enables an onchain financial ecosystem where enterprises can run entire business processes onchain and interact with each other on the open Monad network.
Read the design specifications here: category.xyz/monad-private-s…
Omar (mainnet arc) retweeted

people will realize how hard it is actually to build out a new sustainable ecosystem, esp for a new corporate chain
I’m not convinced that any corporate chain is actually neutral in the first place
read this:
blockchaincapital.com/blog/t…


idk man, I was and still am a big RH believer, but I really hate the hands-off approach they're taking. vlad’s exact words:
“one of the reasons robinhood chain has been so successful is we haven’t really been picking winners. I mean, we wanna help developers out, but we really stay a neutral platform and lower the fees as much as possible”
coinbase and robinhood attract good developers (and lots of rapists) because of the name and help with initial distro, but outside of that initial hype, it feels like RH isn’t doing enough to help projects - similar to base
US-based CEXs obviously can’t move like the Binance cabal and blatantly kingmake things, but there’s a massive middle ground between that and doing nothing. hackathons, grants, incubators, demo days, ecosystem funds, better discovery, etc. can go a long way, and there just doesn’t seem to be enough of that happening rn
kinda fried until this changes
Omar (mainnet arc) retweeted

today we're releasing apex-flash-1, our first open-weights model for security research post-trained on real vulnerabilities we found and got paid for.
we are also releasing the abliterated variant for researchers who want fewer refusals in their own authorized workflows.
how we built it: cantina.security/apex-flash

Omar (mainnet arc) retweeted

coming soon™️
- privacy
- quantum resistance
- MEV resistance
- 100ms blocks
- new assets
- new exchanges
- new launchpads


reminder
Category Labs is proud to introduce Cadence, our multiple-concurrent-proposers (MCP) consensus protocol that matches the optimal good-case latency of single-leader consensus while supporting arbitrarily short block intervals. When combined with BTX, our design for encrypted mempools, this represents a significant step towards solving the problem of MEV at the protocol level.
In nearly every blockchain today, a single party ends up in control of each block: it decides which transactions get in, and can reorder them at will. MCP is the natural fix, but most recent designs pay for it with a separate aggregation phase, adding two extra communication rounds per block.
Cadence makes the proposers part of consensus itself. Its fast path finalizes in an optimal three communication rounds, even when proposers are offline. Cadence also offers speculative finality, similar to MonadBFT, after just two rounds, revertible only if a proposer provably equivocated. In a simulation using estimated network delays between Monad mainnet's 200 globally distributed validators, finalization takes 219 ms on average, speculative finality 167 ms.
Cadence pushes pipelining to the extreme: each block is proposed and finalized in its own independent consensus instance, without waiting on preceding blocks. The block interval then becomes a protocol parameter that can be arbitrarily small. At our initial target of 100 ms, a transaction waits on average just 50 ms to enter a proposal, and oracle prices, liquidations, and auctions can update every 100 ms. Cadence dynamically throttles the opening of new instances to bound the number of outstanding slots even during periods of network instability.
When the network is healthy (under synchrony), a transaction included by an honest proposer can be neither dropped nor deferred (short-term censorship resistance), and no proposer can see the others' proposals in time to react (hiding). We prove both, together with safety and liveness under partial synchrony at the optimal 3f+1 fault bound.
The Cadence protocol is modular: each module is simple on its own, and any of them can be swapped out without touching the rest.
Cadence also builds on components already being deployed: proposals are disseminated as erasure-coded chunks over Deterministic RaptorCast, now rolling out on Monad, and validators vote on proposal digests, so voting does not wait for the full data to arrive.
Start with the interactive tutorial: category.xyz/cadence.
Full paper: arxiv.org/abs/2607.02275.
Joint work by Kushal Babel, Fatima Elsheimy, Lioba Heimbach, Mohammad Mussadiq Jalalzai, Tobias Klenze, Jovan Komatovic, Jason Milionis, Mike Setrin, and Victor Shoup.
Omar (mainnet arc) retweeted

Crystal is live.
Users can trade, launch tokens, and provide liquidity, with Crystals distributed to eligible users each week.
app.crystal.exchange/