
(| 26 w/ Bachelors in Cyber Operations 💻 | Current System Administrator, Security Researcher & Bug Bounty Hunter 👾 | @sitereboots |)
Joined June 2017
- Tweets1.6K
- Following780
- Followers4.2K
- Likes11.3K







Clover - 🖥️ retweeted
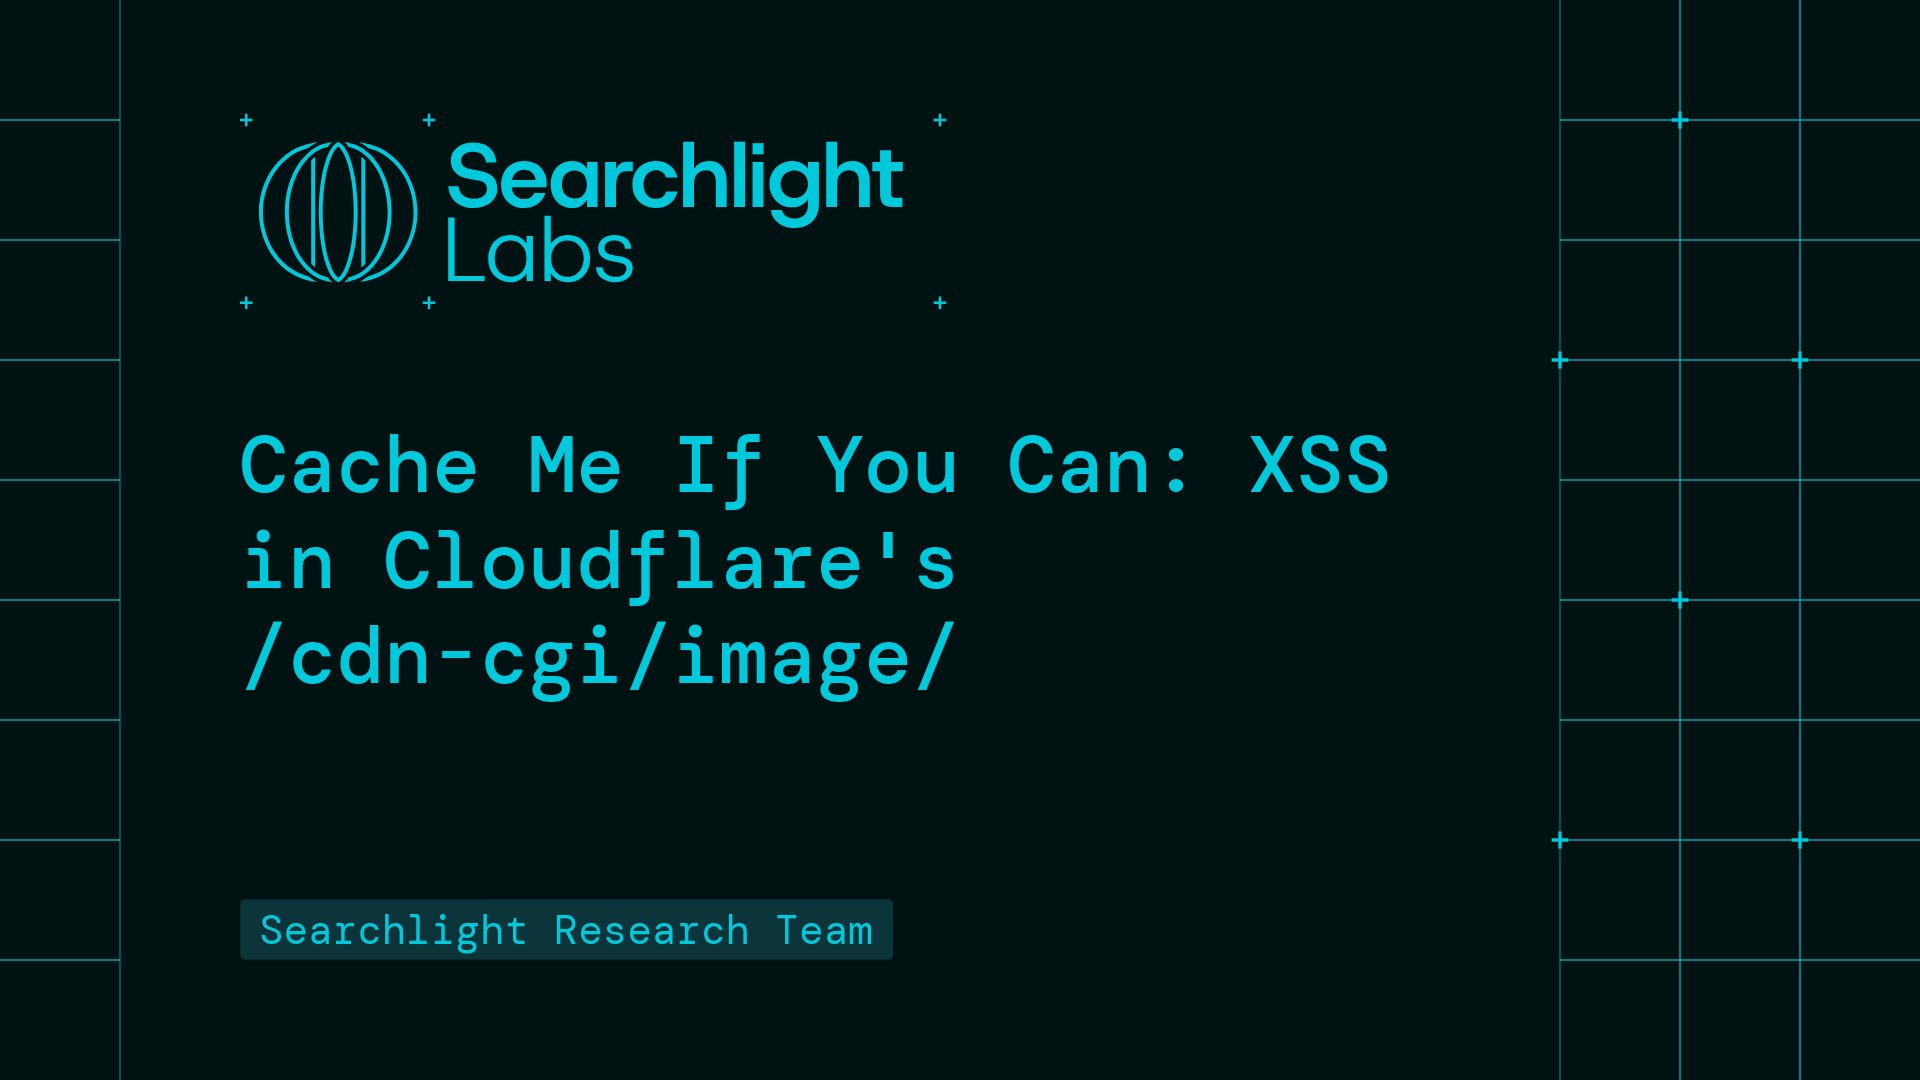
With @hash_kitten, we've been looking into Cloudflare's /cdn-cgi/image endpoint and managed to get an XSS :D
To achieve this, we used what I believe to be a new CSP bypass involving the Cache-Control response header, combined with a sanitizer bypass!
I hope you'll enjoy it! 👇

Our security research team discovered a cross-site scripting vulnerability in Cloudflare's /cdn-cgi/image/ endpoint by chaining an SVG sanitizer bypass with a new Cache-Control header trick to bypass the CSP. The issue was reported to Cloudflare and has since been fixed.
You can read more here:
slcyber.io/research/cache-me…
Finally signed an Independent Contractor Agreement for Penetration Testing with a privately owned security consultant company this month.
rewriting my bug bounty corpus and I constantly run into this (while reworking code?..) despite having all Cyber Approval verifications outside of the Org related ones for Claude Code? quite annoying as of lately... didn't seem to be as bad a week ago?

triaged a month ago... then get told by the team a month later that it's an internal duplicate.. yeah bug bounty isn't fun right now at all...


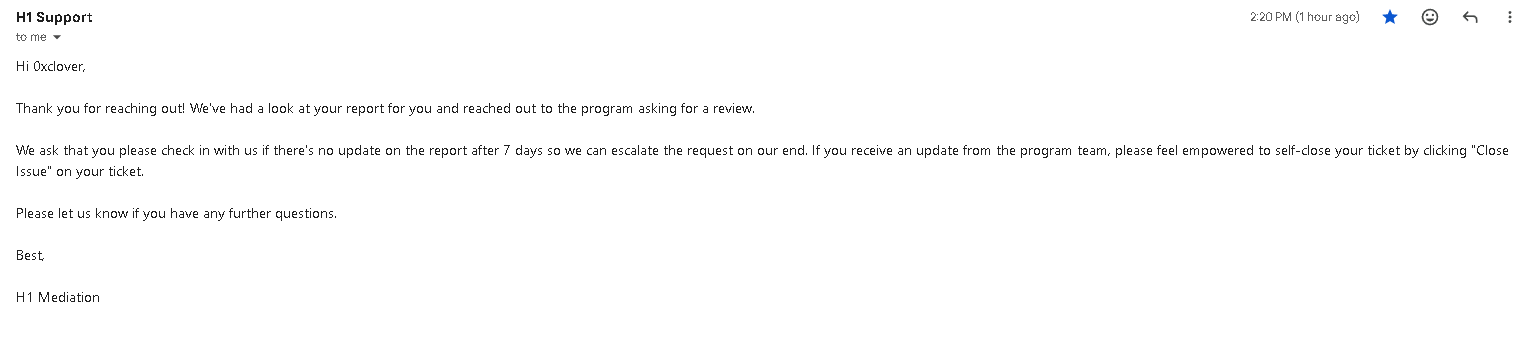
no update on the report yet, 7+ days later.. bumped mediation as they asked me to do. do they 👻 me again? 🙉

Clover - 🖥️ retweeted

🚨Breaking: OpenAI and Anthropic executives are reportedly privately preparing for catastrophic AI events
According to Axios, they're planning for the fallout of a major AI cyberattack that could potentially take down banking, internet or power
Absolutely insane that we're already at this point, many AI industry insiders apparently believe a major incident will happen within the next 6 to 12 months


gonna go ahead and steer clear of this duplicate pool... gave me two N/As as well w no description as to why they're N/A.. they also never ref'd the duped report which is sus.. moving onnnn:


Clover - 🖥️ retweeted

I am very uncomfortable about people trying to ascribe religious force or a surrender of human judgment to AI models, and think it is a real safety issue.
In September, I submitted 21 vulnerabilities to 14 programs on @Hacker0x01. #TogetherWeHitHarder hackerone.com/last-month
seeing how many people are finding cool bugs on @vercel gives me extreme fomo since when I hacked there I found/reported 5 Critical Duplicates, makes me curious if I would've been quicker would I have gotten the same praise😅

Clover - 🖥️ retweeted

Huge for ethereum:0x4a220e6096b25eadb88358cb44068a3248254675:
“At Capgemini, we are helping shape the next generation of payments, where intelligent agents can identify liquidity needs, evaluate alternatives, and recommend or initiate actions within defined governance controls, while programmable digital money enables value to be moved and reconciled in real time. … Our collaboration with Quant reflects a shared commitment to moving beyond theory and demonstrating how these technologies can work together in practical, enterprise-grade use cases.”
@Capgemini 🤝 @quantnetwork
Via @SanNL11