

AI Security | OSEP | OSWE | OSCP | CRTP | CREST CRT | Information Security @CarnegieMellon | Red Team Member @SynackRedTeam
Joined May 2018
- Tweets374
- Following523
- Followers779
- Likes409


at this point, employer benefits should include Claude max 200$ / ChatGPT Pro 500$ for personal use 🫣
62
Adithyan AK retweeted

Loopjacking hijacks human approval in AI workflows. Explore documented cases and practical defenses that keep approval bound to the action executed.
#aisecurity #agenticsecurity...Show more

Why bypass an approval gate when you can change what it approves?
Loopjacking lets an attacker use a legitimate decision to authorize a different action. My A2A write-up follows how approval loses its scope between review and execution.
adithyanak.com/loopjacking-i…

49
Adithyan AK retweeted

Agent Name Collision Attacks in Multi-Agent Systems arxiv.org/html/2609.27624v1
Loopjacking: a human approves A, but the system releases B. The approval is real; its binding to the executed action is broken. My explainer covers the two paths and what to check before execution.
adithyanak.com/what-is-loopj…
3
245
Adithyan AK retweeted
Loopjacking: Hijacking Human-in-the-Loop Approval
arxiv.org/abs/2609.21081

My latest research on Loopjacking attack allows an attacker to Hijack Human-In-The-Loop approvals
arxiv.org/abs/2609.21081
1
107
Your AI agent asked for permission.
You approved one action.
It executed another.
I'm publishing Loopjacking: a failure where an attacker makes a system use your real approval for an action you never authorized.
loopjacking.com

The fix is more than another approval popup.
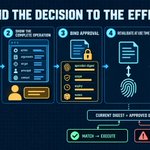
Show the complete action. Bind approval to it. Verify that the action about to execute still matches.
If the recipient, amount or scope changes, the old approval must not authorize it.
adithyanak.com/loopjacking-i…
🤖 Made with AI

1
21
If you build agents with approval gates, ask:
At execution time, what proves this is still the action the human approved?
A task ID or an approved=true flag is not that proof.
Paper, results and limitations: arxiv.org/abs/2609.21081
🤖 Made with AI
1
7


A poisoned MCP tool description is a warning, not proof a model executed a privileged action.
A field note on separating metadata, shared context, reversible validation, and recovery with AgentHound.
adithyanak.com/mcp-tool-pois…

Prompt injection is a data-flow problem: can hostile input cross a trust boundary and reach real authority?
A field note on keeping source, propagation, sink, and evidence state separate with AgentHound.
adithyanak.com/prompt-inject…

An AI-agent inventory can flag a risky tool. It rarely shows whether an attacker can reach it.
AgentHound maps MCP/A2A, credentials, and tools into evidence-backed paths without confusing hypotheses with exploits.
adithyanak.com/build-ai-agen…

1
90
"Save everything" is a bad memory architecture. It creates transcript noise, stale facts, and cross-project leaks.
Here's the Hermes + Mnemosyne design I'm using instead: verified learning and clear ownership.
adithyanak.com/optimal-herme…

1
277

See ya at Defcon RTV

An MCP env var leaks a master key. That key fronts your production Anthropic key. A teammate's Cursor config references a CLAUDE.md on GitHub. @akoffsec built Agenthound to map that exact kind of multi-hop credential chain nobody wrote down. ✍️

3
298
🚀AgentHound - the open source offensive security framework for AI agent infrastructure
Think BloodHound for the agentic stack: MCP, A2A, model gateways, inference servers, vector stores, MLOps, notebooks, and 12 agent clients.
AgentHound follows the relationships between agents, credentials, tools, models, resources, and hosts. Then it turns those relationships into attack paths you can investigate and validate.
☠️ The offensive side:
- Map the attack surface across AI applications, gateways, models, and infrastructure
- Uncover exposed secrets, reused credentials, and overly trusted integrations
- Trace lateral movement, privilege escalation, and potential data-exfiltration paths
- Test indirect prompt injection and tool-poisoning scenarios
- Assess model leakage and fine-tuning data exposure
- Emulate persistence through compromised agent configurations and integrations
- Validate attack paths through controlled, reversible adversary simulation
The first supported release ships with 15 graph post-processors, 19 prebuilt attack-path queries, and 35 detection rules mapped to OWASP MCP, the OWASP Agentic Top 10, and MITRE ATLAS. AgentHound is Apache 2.0 and built for authorized security assessments only.
Repo: github.com/adithyan-ak/Agent…
Website: agenthound.io
