

AlphaSOC is a security data platform built for agentic threat hunting and investigations.
San Francisco, CA
Joined January 2017
- Tweets1.2K
- Following1K
- Followers1.9K
- Likes19





Security teams can use our MCP integration for Claude, Cursor, and other AI tools to perform real-time reputation scoring against our threat intelligence platform and classifiers. Get started here >> docs.alphasoc.com/mcp_server…

Forescout reports ROMULUS, a multi-payload ClickFix platform dropping DLL sideloading packages and LegionLoader via PowerShell across six active servers. AlphaSOC flags these malware delivery and C2 traffic patterns to protect customers. Read more here >> forescout.com/blog/romulus-a…

Need unparalleled visibility into your Azure environment and cloud workloads? AlphaSOC highlights privilege escalation, compromised workloads, hacked accounts, and data exfiltration. Evaluate our analytics engine for free >> alphasoc.com/azure
Facing high Splunk licensing costs? You can run searches against the AlphaSOC OCSF Data Lake to drive investigations and threat hunting without having to index terabytes of low-value, raw logs. Learn more >> docs.alphasoc.com/platform_i…

We process network telemetry to cover 70+ out-of-the-box detection use cases and highlight patterns including spear phishing, impersonation attacks, anonymizing circuit traffic (e.g. Tor and I2P) and cryptomining pool participation. Read more >> docs.alphasoc.com/detections…

Want to flag anomalies within your AWS environment and overlay them with MITRE ATT&CK? We have extended our analytics engine to process CloudTrail logs and highlight 400+ threats. Here's a full list of detection use cases >> docs.alphasoc.com/detections…

Huntress reports a ClickFix campaign delivering a DLL-sideloaded RAT through malicious ChatGPT Custom GPTs promoted in Google ads. AlphaSOC flags these malware delivery and C2 traffic patterns to protect customers. Read more here >> huntress.com/blog/chatgpt-cu…

Want to check whether your threat detection stack can flag C2 beacons, anonymizing circuit traffic, cryptomining, DNS tunneling, and other threats? Use our free, open source adversary simulation tool to instantly evaluate your coverage >> github.com/alphasoc/flightsi…
Using Sigma rules for detection and hunting? Process your EDR telemetry (e.g., Defender for Endpoint, CrowdStrike Falcon, and SentinelOne) with AlphaSOC and deploy both community and custom Sigma detections outside of your SIEM. Read more here >> docs.alphasoc.com/detections…

Our Analytics Engine supports detections across endpoints, cloud workloads, and SaaS applications! Process your CrowdStrike FDR telemetry and logs from AWS, GitHub, Slack, Okta, and other platforms to hunt threats. Dig into the docs here >> docs.alphasoc.com/

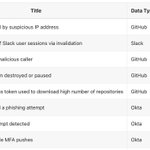
We have many new SaaS detections for GitHub, Okta, and Slack. Process your SaaS audit logs with the AlphaSOC Analytics Engine to hunt threats and even deploy your own custom Sigma rules. Read more here >> docs.alphasoc.com/detections…

Unit 42 reports Blinder Tunnel, an Iranian campaign targeting Iraq's critical infrastructure via spearphishing with ShelbyLoader V2 and GitHub-based C2. AlphaSOC flags these malware delivery and C2 traffic patterns to protect customers. Read more here >> unit42.paloaltonetworks.com/…

Uncover compromised cloud workloads, privilege escalation, and data exfiltration in your AWS CloudTrail, EKS, RDS, VPC flow, and Route 53 telemetry with our patented analytics engine. Learn more here >> alphasoc.com/aws

Third-party VPNs are increasingly used by threat actors to exfiltrate data and evade controls. AlphaSOC provides defenders with visibility into these encrypted sessions, as shown >>

Ransomware groups and other threat actors use remote access tools such as AnyDesk, ScreenConnect, and Splashtop to move laterally without detection. AlphaSOC flags these traffic patterns to provide clear visibility for defenders, as shown >>

Aikido Security reports Graphalgo campaign hitting Terraform providers and Go Modules for the first time, using runtime-triggered Go malware with Slack and Ethereum C2. AlphaSOC flags these malware and C2 patterns to protect customers. Read more here >> aikido.dev/blog/graphalgo-te…

Want to measure the efficacy of your threat detection stack with regard to cryptomining traffic? Use flightsim to generate Stratum traffic to known mining pool services online >> github.com/alphasoc/flightsi…
Interested to know what we've been working on lately? Check out our Changelog that describes the new product features and improvements >> alphasoc.com/changelog/

We track the most dangerous effective top-level domains (eTLDs) online by processing the indicators within our platform each month. Our feed is updated daily, and you can use it to instantly block traffic to statistically bad domains >> feeds.alphasoc.net/bad-etlds…
