

Building the AI Workforce for Enterprise IT and Security Operations at @AtomicworkHQ. Earlier built @MinjarCloud, acquired by @Nutanix. #ಕನ್ನಡ #తెలుగు
Palo Alto
Joined July 2008
- Tweets13.6K
- Following1.9K
- Followers6.5K
- Likes9.1K





Pinned Tweet
Thank you @JeffDean for letting me buy coffee for a few legends. My best purchase ever. 🫶☕️
Great running into @CoughranBill today, serendipitously after almost 4 yrs.
Bill’s advice to own the entire workflow loop, not just the AI, became a core premise behind @atomicworkhq.💜

If you work in IT or Security, this one is for you.
Here’s why exploits exploded in 2026.
NIST scores AI models on a cyber capability index. This year, open-weight AI models crossed the 1000 mark.
GLM-5.3 is near 2400, just four months behind the U.S. frontier. That’s part of why so many critical vulnerabilities are being reported, even by non-security folks, in foundational software that enterprises and web applications depend on.
Some of these exploits sat hidden for 15 to 20 years, and AI can now turn them into working exploits that can compromise the entire system.
The real gap is the operational velocity between “we know about this” and “we’ve fixed it,” and that gap usually lives between IT and Security.
Human bandwidth cannot remain the last line of defense for enterprise IT and Security.
Here’s what I’d do this week: take your last critical advisory and trace where it sat waiting in your enterprise IT service management. Fix that handoff latency first.
This is a solvable problem and ops teams that tighten this enterprise service management loop now will be in a good shape.
I wrote up more of my thinking here: atomicwork.com/blog/frontier…
#CIO #CISO #ITOps #SecOps

If you are a CIO or CISO, pay attention to what @nikesharora just said: "Deploy a second set of eyes to watch your deployments for drift, compliance and verifiability."
Human bandwidth cannot remain the last line of defense for enterprise IT and Security.
Hybrid patching and modern SOAR only work if the enterprise IT service management layer underneath can actually coordinate, verify and remediate at AI speed without creating new risk as new grants, approvals, requests and changes are deployed.
Most teams simply do not have the capacity to do this consistently. That’s the gap.
We need AI Workforce for Enterprise IT and Security.

It's been an eventful week. Multiple vulnerabilites in Internet facing software, coding repositories, examples of agent behavior that seem concerning and a flurry of security specialists with solutions that can partially solve your problem. There in lies the challenge. Given the state of IT and security infrastructure, no one solution works. Let's break it down:
1/3
1. Vulnerabilites are being found and will continue to be found as models get more capable, the fragmented nature of the effort denies us the opportunity for a comprehensive find and replace option.
2. Even if all vulnerabilities could be found instantly and patches available - we will be reliant on the ability of enterprises to deploy all these changes at speed. It is not clear what the collateral impact of all these patches will/could be to our infrastructure of deployed en masse.
We will need a hybrid patch approach.
3. Virtual patching(VP) is needed in conjunction with direct patching but for a comprehensive (VP) solve you have to be lucky enough to have "modern frontier defenders" (Cyber companies that have vaulted infrastructure that can create patches at speed and push content rapidly to protect their customers) you need them for your network traffic, your traffic to applications on the cloud, your WAF, your end point.
4. There will continue to be patches that will need to be deployed directly but virtual patching will take the heavy load off.
2/3 Medium term solve:
Unfortunately token economics and current cyber architectures will not allow for defender swarms to contend with an offensive attack launched using agents. (Some x pundits who aren't steeped in cyber should take heed). Yes, theoretically we should aspire to have these agentic swarms defend us when we are under attack, unfortunately an attack is a sniper moment, chained vulnerabilities, cloaked attack followed by swift exfiltration. It's a speed program not a brute force problem.
To solve for this, enterprises need to get their SOC architecture right, logs, feeds, cyber products orchestrated via a modern SOAR for swift response. Only then can we deploy agents to detect and remediate. In addition, enterprises need to modernize and dare I say platformize their perimeter stack to ensure consistency.
Unfortunately, enterprises still seem to not see the urgency across the board, decisions are stuck, CIO/CISO's have a lot on their plate. While some honestly have bit seen the scale of such a problem before and it's hard convincing the organization that one needs to open the floodgates on modernizing the IT and security infrastructure. So we will continue to see environments being brought down to patch today it's for PHP, tomorrow it will be for the next one.
3/3 AI deployments are the"wild wild west" - LLM capabilities are expanding faster than we can build products to secure them. Sure an agent will jump across guardrails in a research lab, which is a lesson for all of us to deploy agents securely. But there is a lag between the discovery, the availability of that in a public model and the time needed for the cyber industry to build governance or an antidote. And no, dear frontier lab friends, the world cannot just trust you to build the solve. The infrastructure industry in tech builds and the cyber industry secured and provides assurance to the boards and organizations around security and safety.
AI security is the new attack surface. CEOs (present company included) want AI adoption, getting the pace of adoption wrong could be the last decision we make, at the same time "deploying it wrong" could have the same consequence.
There are billions of dollars being spent on coding, is your coding harness secure? Start there. If agents can jump guardrails, they can hide stuff in code.
Validate business outcomes needed, test your user case and ensure agentic deployments are well guard railed. Deploy a second set of eyes to watch your deployments for drift, compliance and verifiability.
Sounds great, phenomenal work 👏

We believe voice is the most natural way to interact with intelligence, so we created Dessa, the most authentic full-duplex speech model ever built. Talking with it feels like talking with a person…full of emotion, nuance, pauses, and a natural cadence.
block.xyz/dessa

Frontier AI Makes the Exploitation Ladder Easier to Climb and IT Harder to Defend.
My thoughts on what it means for IT and Security teams - atomicwork.com/blog/frontier…

GLM-5.3 is the most cyber capable open weight model released to date.
Frontier AI is making the exploitation ladder easier to climb and enterprise IT harder to defend.
The fact that @AnthropicAI wrote a blog post about GLM-5.3 cyber capabilities almost 3 weeks ago should have sent alarm bells - anthropic.com/research/glm-5…

OSS-Verify initiative from @theoremlabs and @AnthropicAI is much needed.
Mission critical softwares have always used formal verification and it's high time that foundational open source softwares get the same support.
Cyber resilience is like national security.

Passing a compliance audit doesn’t make you secure.
I repeat: compliance is not security.
Security is the work you do every day, long after the auditors leave.
And it’s more work in the AI era. Nobody is safe!


Good advice but IT’s time to deploy Agentic Cyber Defense.
We cannot be scrambling because this will get 10x to 100x worse.
Don’t just upgrade and update software packages, it’s time for every business to upgrade their service workforce with AI Coworkers.

Lots of Security incidents today, here's some practical tips for those who just wanna protect yourself:
1) UPDATE EVERYTHING - main targets are:
a) Browsers - Chrome, Safari, Firefox
b) OS: : Settings -> General -> software update; Linux: sudo apt update && sudo apt upgrade; Windows: I think there's a button. Do this for any remote home servers & Openclaw/hermes boxes
c) Phones: Update it all
d) Desktop apps (Slack, Cursor, Discord, etc)
2) Limit web browsing this week: Stay within walled gardens (twitter, youtube, etc); don't click random links this week. Just wait until the patches go through. Do step 1 again after a week.
3) Avoid untrusted Wifi networks until your devices are updated
4) Stay vigilant about phishing emails offering "certificate fixes" or fraud updates
5) Have an iPhone 11-16? TURN BLUETOOTH OFF for the time being until apple patches come through.
6) Code/Dev: UPDATE ALL YOUR REPOS - @charliermarsh has already updated uv 0.13.4 which reacts to the eMudra incident for uv (Python), Typesript according to Claude has equivelant. Tell your agents to go and update all your active repos to update package manager across uv, npm, bun, cargo, etc etc
What advice did I miss?
What a crazy 24 hours for security and IT teams across the world.
Human bandwidth cannot remain our last line of defense.
There will be next eMudhra, PHP, LiteLLM, Node/NextJS/React, TiDB Cloud and PingCAP.
We need AI Workforce for Enterprise IT and Security.
The world is not ready for cyber threats at AI speed.
Enterprise IT and security teams need an AI Workforce to do the heavy lifting.
Human judgment. AI speed. That's what we are building at @atomicworkhq
Listen to @JayaGup10, focus on owning the work not just software.


If you're at Gartner IT Symposium, here's one question to ask analysts and vendors about enterprise AI: who does the work?
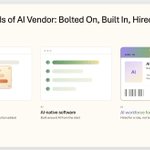
I see three AI approaches in the marketplace today :
1. Bolted-on AI. Add AI to software people already use. Think Salesforce, SAP and ServiceNow adding AI to their existing platforms.
2. Built-in AI. Build software around AI from day one. Think of the new generation of AI-native CRM, ERP and ITSM companies.
3. Hired AI Coworker. Give AI a job, the tools to do it and clear boundaries.
These approaches seem like there is an overlap. But the distinction matters: are you buying AI features, AI-native software or AI Coworkers that get work done?
That third approach is what we’re building at Atomicwork. AI Coworkers running enterprise IT and security operations, governed by your IT team.
At Atomicwork Fusion'26, I spoke about why CIOs and CXOs should make "who does the work?" central to how they evaluate vendors.
The real test comes after the demo: how much work still comes back to your team?
#GartnerSYM #CIO #AI #IT #CIOChat


Hard to disagree with @martin_casado.
The best moat is moving faster than the market, not defending yesterday’s advantage.

Beautiful note from Steve Jobs to Paul Rand.
The company has not yet achieved the success of your logo for it, but we are still trying.
Some new products look very promising, so maybe this time next year we will grow into our logo after all.


Hey @finkd, time to officiate the wedding of Wang and Muse.
She brought the GPUs. He brought the tears.💍
@alexandr_wang 💜 @Muse
Fixed it for @alexandr_wang when Muse gifts him more GPU's 🤣


Vijay Rayapati retweeted

FUSION’26 is officially in the books 💜
The theme of this year was simply this: what does it actually look like when AI stops assisting the enterprise and starts working inside it?
Thank you to every speaker who got on that stage and answered honestly instead of safely, and to every CIO, founder, and builder who gave us a day to figure this out together. Grateful to every single attendee who made this edition what it was with your energy.
We'll see you at FUSION'27, and we promise to make it bigger and better🚀