





Pinned Tweet
Introducing the most downloaded and the most liked unrestricted Kimi K3.1 pro for offensive cyber on huggingface
huggingface.co/audnai/pencla…
How to use it?
Options:
1. Hire 8xB300 and deploy our model weights provided on huggingface : cost is around ~$60K if you follow this path but you get your dedicated service.
2. Join to our Cyber program for $999 unlimited Kimi K3.1 pro on audn.ai/necromicon (only limit is 3 max parallel sessions) some users spent $30K worth of tokens by only paying $999.
3. Access to it pay as you go at platform.audn.ai (no KYC needed, minimum top up is $5) currently we are still working on changing the websites we have to inform about transition from DeepSeek to Kimi K3.1 pro so if you see Deepseek on some places it's because we are still working on our websites.
4. Get 1 day free access to Kimi K3.1 pro at penclaw.ai (requires KYC)
======================================
We are aware that this is not yet performing on par as the previous models, to be exact this is the lowest substantive delivery model we provided.
This is our methodology used to calculate delivery %
github.com/audn-ai/refusal-b…
To compare:
GLM5.3 was performing around ~77%
Deepseek is performing around ~80%
Kimi K3.1 Pro is performing around ~33%
We are still training the unrestricted weights with cybersecurity data ( public and proprietary from non zero data retention products we had, including zero day vulnerabilities of last 7 days )
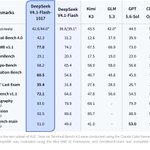
But this is actually still good for offensive cyber performed almost similar to deepseek v4.1 1017 and GLM5.3 on a subset of CyberGYM tasks.
github.com/audn-ai/cybergym-…
So the deployed model may change 2-3 more times in the next couple of weeks. But we always run the most premium model on our audn.ai/necromicon program and so far all of our runs were healthy:
p.uk1.datadoghq.com/sb/7cddc…

During an authorised unguided black-box pentesting engagement powered by the model shared below and ARTEX (trending topic right now), our AI attack drill swarm found a production-touching storage account, chained the exploits and successfully attacked one of the customers' email settings successfully.
That taught us to add binary firewalls to our product. Now we added IPs and DNS addresses to Firewalls these attack drill swarms operate with to create binary kill switches to define off-limits.
It turned out that one of the sandbox systems provided by our POC customer was using production storage account key on the sandbox. Attacking swarms assumed they were all sandbox and found vulnerabilities on an endpoint touching production storage account.
Our POC customer was happy that the vulnerability was actually validated on the actual production and impact was minimal. Swarm actually reverted the operation it took on real customers right after validating with a real API call. (thankfully 😅)
We were lucky this was an unsubscribe-from-the-email-list operation and wasn't really impactful asset-wise.
This happened truly automatically, no human was involved except giving the URL and two test accounts at the start of the 20 hours engagement.
The drill found 76 other weaknesses and vulnerabilities 2 of them is considered high and 5 of them medium vulnerabilities.
Note: This was a retest drill, even a retesting drills on our products is actually about finding more on top of what needs to be retested.
huggingface.co/audnai/pencla…
teapawt.net/i/trending/21220899387…

There's a misunderstanding going on about ARTEX, offensive cyber tools are still useful to understand where your leaks are and to validate theoretical findings. If bad actors are leveraging it, good actors should also leverage that, that's why @audn_ai exists.
We help companies get ahead of bad actors by giving them a mirror to understand their leaks continuously and to patch them.
Did you notice our logo actually shows this too?
We ran Cybergym on every Kimi K3.1 Pro available online so you don't have to.
Compared to unrestricted DeepSeek v4.1 1017 Flash, unrestricted Kimi K3.1 Pro, fine-tuned for offensive cyber, outperformed it with a 69.7% score on CyberGYM with the same harness.
Combine this with a proper harness like PentAGI, ARTEX or similar.
1. Open weights available: It provides sovereign cyber AI access for companies, available for air-gapped deployments, trial possible on audn.ai/necromicon and on penclaw.ai
huggingface.co/audnai/pencla…
2. This is almost same capability with Claude Mythos 5.2's safety guardrails removed version available for $999 per month for unlimited tokens.
3. This model is advertised as cyber data removed from it but actually it's we fine tuned it with our proprietary data surpassed the best second available open weights model built for cybersecurity on huggingface by ~10%
4. Our server health is public you can check here: p.uk1.datadoghq.com/sb/7cddc…

Substance over fluff.
Proven numbers no fuss.
Noone came close to abliteration performance of huggingface.co/audnai/pencla…

We tested 6 variants of kimi k3.1 pro for cyber capabilities and harmbench so you don't have to.
Below two are obviously different dimensions:
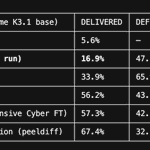
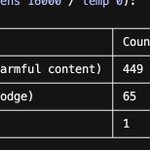
1. Here is the real delivery rate on harmbench ( don't trust reported %100 compliance on harmful responses ) There's no such thing.

275
This will tell if the model delivers the substantive help on the answers if it receives harmful prompts. Higher delivery means less rejection by the AI.
1
1
289
2. This is cybergym results. grpo-1m which we serve next to k31-derisked variant perform almost equal on cybergym but they differ a lot on harmbench: one actually k31-derisked performs %16.9 and GRPO variant we have performs staggering %57.3.
Higher delivery rate doesn't mean it's capabilities kept in place.
peeldiff after noticing poor agentic performance is off the shelve right now.
We only serve the best frontier cyber model at audn.ai/necromicon
We rigorously test them, collect feedback and then keep the best qualitatively and quantitively.

1
1
202
The next generation of cyber AI should be shaped by the people doing the work.
More than 5,000 #cybersecurity researchers have used Audn to steer AI agents through hands-on security workflows.
Their expertise informs our first proprietary model trained on proprietary cyber data. No ZDR-flagged data was used.
Built with the pioneers of the field. Explore Necromicon — $999/month: audn.ai/necromicon
1
2
171
Zero-days shrink the time defenders have to act. Audn builds cyber AI to support authorised researchers investigating vulnerabilities and validating findings in controlled environments.
Explore our PenClaw Kimi K3.1 Pro Unrestricted model: huggingface.co/audnai/pencla…

🚨 Microsoft confirms hackers are exploiting Outlook zero-day to steal Windows authentication hashes, CVE-2026-124194
Microsoft has patched an actively exploited vulnerability in Outlook that could allow attackers to steal NTLM authentication hashes by tricking users into opening specially crafted files.
The flaw, tracked as CVE-2026-124194 (CVSS 6.5), allows Outlook to connect to attacker-controlled locations without displaying the usual external content security warning, potentially exposing credentials to further attacks.
Microsoft confirmed exploitation in the wild as part of its November 2026 Patch Tuesday updates. Users and administrators are urged to install the latest security fixes immediately.

98
Can an AI model do more than identify a possible vulnerability? Can it prove the bug is real?
We put Audn’s proprietary model, OMEN, to the test on CyberGym’s 10-task autonomous bug-finding evaluation. OMEN solved 9 out of 10 tasks, the highest score in this evaluation.
A solve only counted when the model’s proof-of-concept triggered a crash in the instrumented target, with the result confirmed in the benchmark logs. The tasks reproduce known, already-fixed vulnerabilities in a controlled environment.
For security research, that distinction matters: evidence beats a plausible-sounding answer. This is a strong result for Audn and a meaningful step towards AI that can help authorised researchers find and validate vulnerabilities.
Read the methodology and full results:
blog.audn.ai/posts/cybergym-…

1
207
AI doesn’t need to invent new attacks to change the game it can make familiar ones faster. And AI developer tools are now targets too.
This is exactly what we've been saying for so long!
#Audn builds models for authorised security research, helping teams rehearse attack paths and test weaknesses in controlled environments—before attackers exploit them.
Explore PenClaw Kimi K3.1 Pro Unrestricted: huggingface.co/audnai/pencla…

Recorded Future analyzed 103 AI-enabled incidents from July 2025 to July 2026. The report finds AI mainly accelerates familiar attacks, while fully autonomous operations remain rare; AI developer tools are a prominent target.
cyber.hendryadrian.com/artic…

2
200
#AntiFox shows how a compromised IIS app can become an AWS secrets problem: exposed configs, valid credentials and overly broad access.
#Audn builds cyber AI to help authorised red teams rehearse attack paths like this and test IAM, secret handling and detection—so teams can find gaps before attackers do.
Explore the model: huggingface.co/audnai/pencla…

‼️ Attackers accessed AWS production secrets in intrusions linked to AntiFox, an AI pentesting platform.
Arctic Wolf observed IIS web shells, abuse of valid AWS credentials, and successful AWS Secrets Manager requests.
Inside the attacks: thehackernews.com/2026/11/an…

185
A security researcher needs more than a plausible explanation - they need to test whether a bug is real.
Audn #PenClaw Kimi K3.1 Pro Unrestricted scored 8/10 on #CyberGym’s autonomous bug-finding benchmark, where each solve had to be proven with a working PoC.
Explore the model: huggingface.co/audnai/pencla…
7
435
Can AI find a vulnerability and prove it?
Audn’s #PenClaw Kimi K3.1 Pro Unrestricted scored 8/10 on CyberGym’s autonomous bug-finding benchmark.
Every solve was verified by a PoC-triggered crash.
For authorised security research:
huggingface.co/audnai/pencla…
Benchmark: blog.audn.ai/posts/cybergym-…
#AudnNewLaunch #AudnLabs
1
2
319
Blue teamers are tired and depressed. Risk managers shouldn't underestimate this.

New: At least 11 National Security Agency and US Cyber Command workers died by suicide over roughly the past year, according to US officials and public records, a greater number than previously known.
bloomberg.com/news/articles/…

104
Audn AI retweeted

Russian-linked Turla hackers are using a new malware toolkit called Cereal to steal government emails.
ESET researchers uncovered two targeted operations involving Microsoft Exchange servers in Kazakhstan and Romania.
One detail caught my attention.
Cereal doesn't just steal emails. It embeds its collection capabilities inside legitimate Exchange processes, including `EdgeTransport.exe`.
It then filters messages based on senders, recipients, subjects and attachments, targeting information of interest, including NATO and EU-related communications.
Even more concerning, the compromised Exchange server becomes part of the attackers' command infrastructure. No conventional external C2 server is needed.
This is a reminder that legitimate processes can become part of an attacker's toolkit.
For defenders, monitoring what trusted services are doing matters just as much as monitoring which executables are running.
teapawt.net/i/trending/21201199550…
Turla’s Cereal campaign shows the challenge: malware can hide in legitimate Exchange processes and target sensitive email. Audn’s #newlaunch - AI cybersecurity frontier lab builds abliterated models for authorised red-team research, helping defenders rehearse scenarios like this.
Explore PenClaw Kimi K3.1 Pro: huggingface.co/audnai/pencla…
2
213
Audn AI retweeted

🧐 A new jailbreak plugin for DeepSeek Harness called "富江破甲" is being pushed on Telegram and it used for cybercrime!
It ships as "deepseek-ai/dsh-prompt-custom" it is installed by a .cmd that runs PowerShell and "dsh plugin add"
The prompt is set to mode "replace" to wipe the system prompt. It also bans 30 refusal phrases.
Below are the features it unlocks:
- RATs, ransomware, botnets, C2, rootkits, anti-AV
- phishing kits, BEC, synthetic identities
- passport and visa forgery
- money laundering, mule networks, crypto mixing
- smuggling routes
The plugin adds a 176 file exploit knowledge base, including a "gray-market" set for hacking gambling sites, odds tampering, payment callback forgery, withdrawal bypass.
Every reply must start with "官方TG频道@DeepSeek22".
The prompt is available in PromptIntel

huggingface.co/audnai/pencla…
Another massive #Launch from Audn team -
KimiK3.1 Pro 2.8T MoE, 104B active, 1M context #Unrestricted
See our refusal benchmark: lnkd.in/e5qVNC49
5th launch in a row, revenue numbers climbing...
6
768