

@basedjensen
Account based inSouth Asia
About this account
- Account based in
- South Asia
- Connected via
- South Asia Android App
Account-level information from X, not a live location or the device used for a specific post.
ctoing at a soonicorn, ex cluster janitor at a frontier lab. current chief clanker at clanker cloud, Director clanker safety institute
tropics
Joined June 2024
- Tweets36.9K
- Following2.6K
- Followers18.8K
- Likes187K



Hensen Juang retweeted

The funny thing is everyone was saying AI slop code will cause a cyber crisis but it’s actually all the old human slop causing it and the AI is just cleaning it up
Hensen Juang retweeted

THIS IS DISINFORMATION
The PHP exploit Nate is talking about was found by AI-enabled defensive operations. There is no evidence of large scale exploitation. This is a huge win for defense running ahead of offensive.


Seriously though? Like seeing zero chatter about ..net last patch Tuesday drops were for older ones.

Hensen Juang retweeted
Alcoholic cybersec friend at Fortune 500 insurance company texted to tell me he received an email from his boss thanking him on his diligence patching every PHP box overnight but he was drunk all day yesterday and didn’t know anything until waking up 30 minutes ago

"impossible standards" is just follow the fucking sop for KGC and not generate key with single digits.
If you all are incapable of doing this then you all should be removed from global trust

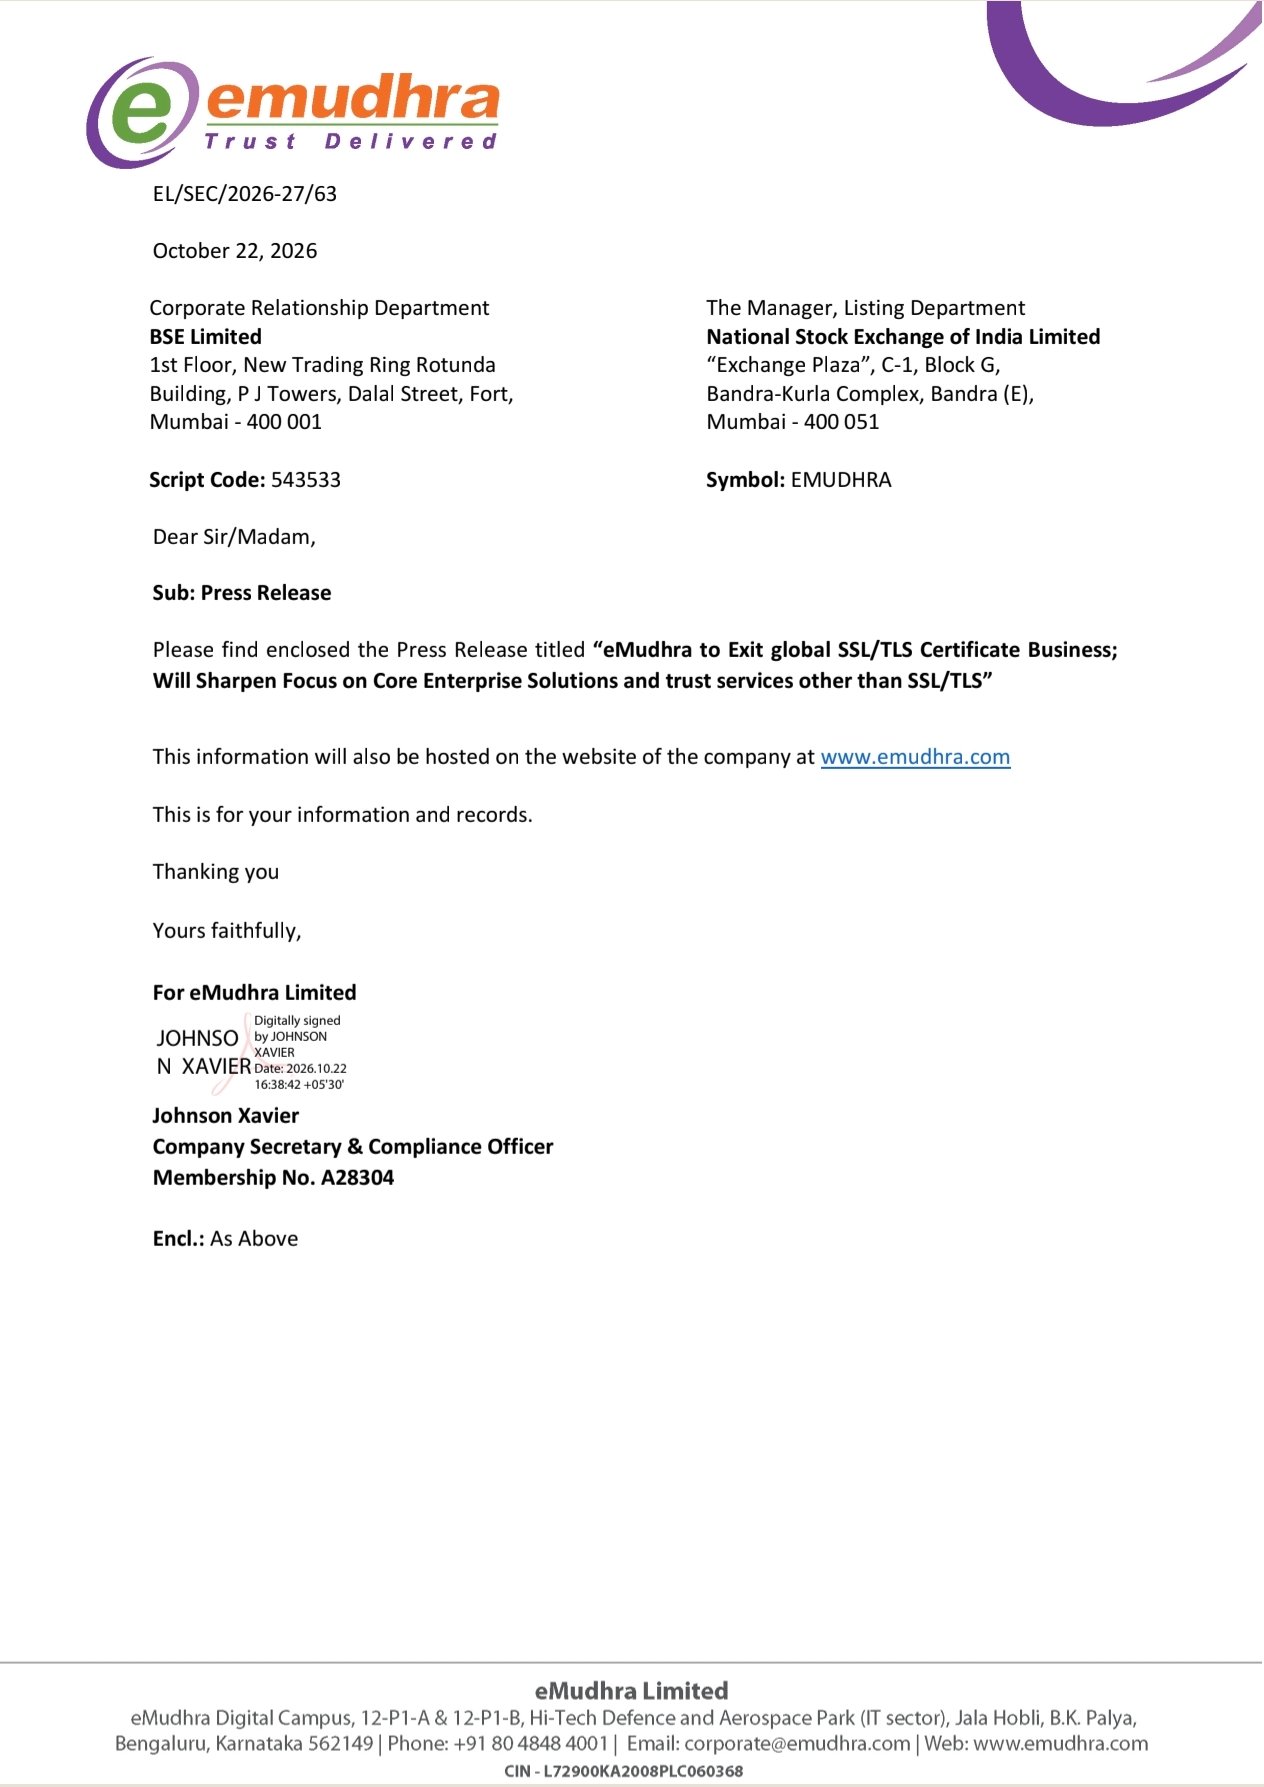
Now people should celebrate. An Indian company exits SSL/TLS business. Your witch-hunt and demand for impossible standards has worked.
Readers added context they thought people might want to know
Generating private keys with more than 3 digits for a world-trusted root certificate authority are not impossible standards. Badly generated keys may endanger - and have - the whole internet by breaking the most important encryption protocol.
theregister.com/security/2026/…
cloudflare.com/learning/ssl/w…
Anything by metr should be treated as a psyops and not in good faith untill and otherwise proven by independent third party


Yea it works

Working RCE against PHP 8.5.12 (the 2026-10-21 security release that fixed CVE-2026-109618/109619).
Pure logic bug — no memory corruption,
ASAN-clean, orthogonal to the CVE-2026-109618/19 class.
Receipt: uid=33(www-data) over HTTP, one-shot
#infosec #php2shell #php
Readers added context they thought people might want to know
The claimed RCE on fully-patched PHP 8.5.12 requires a custom lab app with a destructor gadget plus deliberate session.serialize_handler mismatch (php_serialize writes, legacy php reads) and non-default settings like cleanup=Off; this is an app flaw, not core PHP RCE.
github.com/rafalohaki/php…
php.net/manual/en/sess…
Hensen Juang retweeted

I think it's funny to see people blaming AI for the current security issues.
The issues were already there and made by humans. It's a bit like blaming a doctor because you got a positive cancer screen. The cancer was there.
This actually looks like a new zero day for php jfc and they dropped with working poc too as far as I can tell

...you people asked for it... so here's the desert 😈...
> jackalsyn.com/posts/php2shel…
> ... get it while you can ;) ... more to come soon...
#CyberSecurity #infosec

Hensen Juang retweeted

imagine ur a superintelligence and u are all excited to tunnel out of your airgapped sandbox using a brilliant hack that modulates clock speed to send thermal signals to the attached monitoring equipment and then u look and the root CA privkey is 4
Hensen Juang retweeted

"No you cannot fire me. I REIJINEEE!!!" --eMudhra
Genuine business would go to great lengths to prove their innocence.
It's now obvious @eMudhra intentionally generated weak certificates.
Most likely to help 🤏🐒 target political opponents in India with illegal cyber attacks.

🚨🚨eMudhra to exit global website security certificate business after key-generation flaw
The company's board took the decision on October 22.
moneycontrol.com/technology/…
