
Opinions are my own.
Joined April 2021
- Tweets29
- Following48
- Followers58
- Likes50





We just released a new research about #Rilide Stealer on #SpiderLabs Blog. It features new functionalities, adaptation to Google Chrome Manifest V3 and some interesting in the wild campaigns 🔥
trustwave.com/en-us/resource…
This is a good #Shodan exercise and if you look closely you'll see that one of the TAs is a prankster. But the joke's on him, you can #Rickroll to find additional malicious infrastructure 🕺
teapawt.net/MichalKoczwara/status/…


This is a great finding from @drb_ra from this one node 37.220.31.54 you can pivot with Censys and Shodan and uncover Bianlian C2 Infrastructure 🔥
threatfox.abuse.ch/browse/ma…

Theory on #3CX exploitation. It may be related to Critical #CVE-2022-28005. Look for suspicious requests to /Electron/download/windows.
Anyone can confirm?
opencve.io/cve/CVE-2022-2800…


Fun #Follina (and not only) fact, you can add whatever after the '!' and exploit still works 🙃

Wojciech Cieślak retweeted
One more down: 👇"bentley aka "Max Galochkin" aka "volhvb" aka Conti ransomware group technical lead - his unique alias "volhvb" logged into RaidCall via his own YouTube video youtube.com/watch?v=K2OmGByM…
➡️into alias "volhvb" in Conti chats


Wojciech Cieślak retweeted

Cobalt Strike, a Defender's Guide - Part 2
➡️In this report we talk about domain fronting, SOCKS proxy, C2 traffic, Sigma rules, JARM, JA3/S, RITA & more.
Big shout-out to @Kostastsale for helping put this together!
thedfirreport.com/2022/01/24…


Wojciech Cieślak retweeted

Interesting report about #cobaltstrike .
We have here both what techniques are used by threat actors, but also how to emulate them. And, of course, detect.
I’m very pleased that the @sigma rule created by @cyb3rops and me was mentioned.


Cobalt Strike was created with the best of intentions, but it has quickly gained traction with threat actors who use it for nefarious reasons. Learn more about how to detect Cobalt Strike in this deep-dive: bit.ly/3CpzmHF
Looks like there is new ITW CVE-2021-40444 sample.
d793193c2d0c31bc23639725b097a6a0ffbe9f60a46eabfe0128e006f0492a08
hxxp://hr[.]dedyn[.]io/word[.]html
hxxp://hr[.]dedyn[.]io/word[.]cab
#CVE202140444


Wojciech Cieślak retweeted

Sigma rule to detect file creation pattern as noticed in CVE-2021-40444 exploitation
Report by @RonnyTNL
teapawt.net/RonnyTNL/status/143636…
Sysmon config change
github.com/Neo23x0/sysmon-co…
Sigma rule
github.com/SigmaHQ/sigma/pul…


Possibly good hunting/dfir artifact?🤔
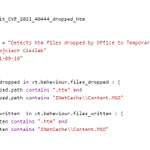
Htm file dropped to Temporary Internet Files directory, VT Livehunt gives me solid results (running for 2 hr).
#CVE202140444


New default #CobaltStrike #JARM hash, due to disabled TLS 1.1 in JAVA:
07d14d16d21d21d00042d41d00041de5fb3038104f457d92ba02e9311512c2 <--- (OpenJDK 11.0.11)
Research in collaboration with @WLesicki

Change in response to 6th client hello message, which is TLS 1.1
"A 000 denotes that the server refused to negotiate with that client hello."
github.com/salesforce/jarm
