




Pinned Tweet
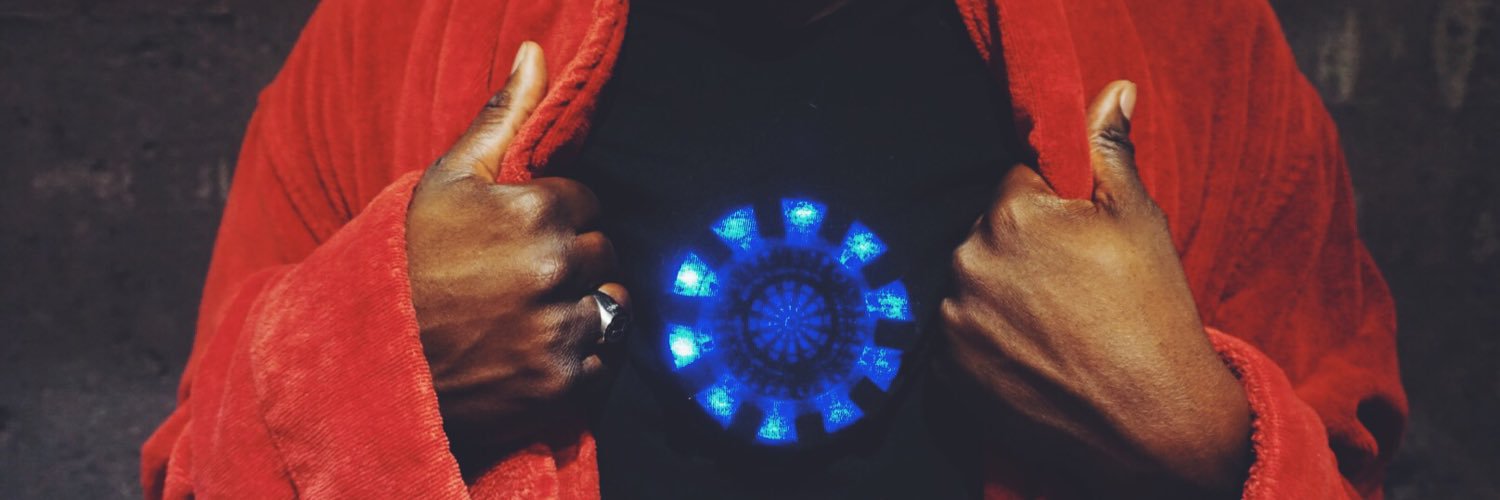
#blackpanthercosplay update circuit work complete: “left/right sides”. The next step, making sure the suit is CON-PROOF... durability testing and upgrade videos are coming soon, the #TonyDark edition !!!
#adafruit #circuitpython #micropython – at Manhattan, NY
Malcolm Jones retweeted
This is going to be a very important resource for everyone managing any technology infrastructure to bookmark.

Introducing Zero Wire: a public vulnerability intelligence feed on @CloudflareRadar, bringing the clarity of a news wire service to critical security developments. cfl.re/4iCvSbj

Malcolm Jones retweeted

this is basically the bitter lesson at work
the smartest models will need fewer and fewer tokens, they won't need to verify their work or check it for bugs, they will just be right

maybe a hot take but i now consider adversarial reviews mostly a waste of tokens. far better to use those tokens on empirical combined with formal verification. i have updated pstack to use the interrogate skill less, and eventually i think i may remove it altogether
i have found very little value with code review in the abstract, agents tend to just get lost in the nitpicks and yagnis
Malcolm Jones retweeted
Playwright and browser security reminder.
We saw a post suggesting that you delete Playwright because it bundles browsers with CVEs. That is a misconception. Do not delete Playwright🙃. Here is how it works and what you should do.
No Playwright package bundles a browser. Agents on Playwright MCP or CLI run your stable Chrome, which gets Chrome's security updates, with the sandbox on.
🤖 If you use Playwright MCP or the Playwright CLI
They use the stable Chrome / Edge on your machine, so it gets its normal updates. No config edit is needed.
🧪 If you use the test runner
When you run npx playwright install, Playwright downloads Chrome for Testing, pinned to the build we tested that release against. The pin is on purpose. Your tests run on the same browser on every laptop and CI machine, and a browser
update cannot suddenly break your suite. You choose when to move by upgrading Playwright. New releases usually pin a build ahead of stable Chrome, so you see breakage before your users do.
We recommend this for full e2e test suites on your own trusted app. This build can miss Chrome security fixes until the next Playwright release, and by default it runs with the sandbox off. Do not use it on the hostile web.
📚 If you use the library API
chromium.launch() has the same defaults: the pinned build with the sandbox off. If your code visits pages you don't control (scrapers, agent scripts), max out protection:
chromium.launch({ channel: 'chrome', chromiumSandbox: true })
🔒 Always keep Chrome / Edge updated. Some bugs can escape a sandbox.
Happy testing!
Malcolm Jones retweeted

‼️ Apps built with the AI app-maker Lovable left passport numbers, payment information and 200,000 chat messages open to anyone, no login needed.
German security firm Crissy Field scanned 159,041 Lovable projects and found databases with email addresses readable on 7,403 sites.
Lovable promises no coding skills are needed. Its terms make customers responsible for their apps and data.
Lovable told German business daily Handelsblatt the problem is industry-wide.


Malcolm Jones retweeted

So schedule for the upcoming week on here
Discourse Monday
Election Tuesday
Reinvasion of Iran Wednesday
Fable 5.5 and Astra 6.2 Thursday
Fake ceasefire to market pump Friday
Gonna be an all timer, stop touching grass and get your ass online
Malcolm Jones retweeted

Hard to overstate how big this is.
tl;dr - CVE-2026-98432: a remote use-after-free in the Linux IPv4 TCP handshake (kernels 4.4+).
Any unpatched server that accepts IPv4 TCP on an MPTCP listener can be taken over as root, with no credentials. Go servers built with Go 1.24+ use MPTCP listeners by default.
Ubuntu and RHEL have no fixed kernel yet. Check with ss -Mlnp. Quick fix for Go: GODEBUG=multipathtcp=0.

What a disaster atlasum.net/blog/cve-2026-98…

Malcolm Jones retweeted

Update on the 9.8 CVSS TCP/IP RCE in the Linux kernel (CVE-2026-98432): we've detected what appears to be a threat actor activity scanning the entire internet for exposed affected systems. Our own scanning also suggests that the number of potential targets is high, therefore there is an increased likelihood of threat actors attempting to develop exploits for the vulnerability.
while CVE-2026-98432 is believed to require MPTCP to be enabled in the kernel, as well as a listening app/service which binds an MPTCP socket, which many have suggested should be rare, several kernels including Debian enable MPTCP by default.
Additionally, Go 1.24+ binds MPTCP sockets by default if the option is enabled in the kernel, so anything built on top of Go (including Caddy) will create the required MPTCP listener.
The mitigation of setting net.mptcp.enabled=0 disabled MPTCP, but does not apply to existing sockets, so any applications that have bound MPTCP sockets need to be restarted, otherwise the system remains exploitable.
You can check if your server is running any MPTCP listeners with the following command: sudo ss -Mlnp
On 2026-10-30 our preliminary internet-wide scan of port 443 confirmed that there are approximately 2,102,043 servers that are successfully reachable via an MPTCP connection. A deeper scan which attempts to connect to each endpoint on port 443 and negotiate a full TLS connection with MPTCP enabled returned about 762,774 systems.
Neither scan can confirm that these are unpatched kernels, just total exposure, but it's a lot more systems than expected. Since a valid HTTP connection is not required to exploit the vulnerability, the total attack surface is likely closer to the 2.1 million number than the 763k one.
As of today (2026-11-02), we've picked up several residential proxies and VPNs scanning the internet on port 443 using MPTCP-enabled connections. Since regular scanners do not negotiate MPTCP by default, and no data is being sent to the HTTP server over 443, we strongly suspect this activity is scanning for CVE-2026-98432 specifically. The use of residential proxies and RU-based VPN servers suggests that this is likely threat actor scanning, rather than security researchers.
Currently there are no known publicly available remote code execution exploits, but there are several denial of service proof-of-concepts floating around. This code gives threat actors a starting point to begin attempting to weaponize the vulnerability. Building exploits for the vulnerability is reported to be extremely difficult, but several state-sponsored threat actors likely have the resources required to succeed.
Malcolm Jones retweeted

Hard to overstate how big of a deal this is.
tl;dr — ANY unpatched Linux server with even a single TCP port exposed to the internet (say for HTTP or SSH) and MPTCP active (default for many Go web servers) is vulnerable to complete takeover.
What a disaster atlasum.net/blog/cve-2026-98…
Malcolm Jones retweeted

Worth checking your Playwright setup today. You probably have instances running you aren't aware of.

Malcolm Jones retweeted

The coding interview is dead, at least for my team at Anthropic. I've seen enough to know that it no longer provides signal. I removed it from loops this month.
I have a spicy, optimistic take - I think there's an opportunity for junior engineers: felixrieseberg.com/hunger-be…

Malcolm Jones retweeted
I highly recommend cloudflare's security audit skill: github.com/cloudflare/securi…
Run it on all your software. Run it with the free models. Use it even if you used a model to audit something - it will find much more things. Works in all agent harnesses and is model independent.

Malcolm Jones retweeted

How on earth did this happen:
The Indian certificate authority (CA) eMudhra had one job (well, two):
1. Create secure, 384-bit private keys
2. Store these securely and do not leak them
Well, eMudhra chose private keys between 1 and 256 (the numbers!!) and called it a day. WTF


Malcolm Jones retweeted
Prompt of the day:
/grill-me on how a /software-factory might help us
Helps you figure out if a software factory can help you, and brainstorms the infra you need to set it up.
github.com/mattpocock/skills…

Malcolm Jones retweeted

Gemini 4 Argon is here.
It’s available globally today for developers and enterprises in the paid tier of the Gemini API and the Gemini platform, for Ultra subscribers in Google Antigravity, and Ultra and Pro subscribers in the Gemini app and Search.
Hope you all enjoy it!
Malcolm Jones retweeted

You can now train your own Decision model like Jev locally!
We increased Qwen3.5 0.8B’s aggregate accuracy from 20.7% to 74.3% across 3 decision benchmarks - on just 4GB VRAM.
Turn any LLM like Qwen3.8, Gemma 4 into decision models with our open-source Unsloth repo.
We fine-tuned with a Clef head using Unsloth and LoRA (r=64) for one epoch, increasing downstream accuracy from 30–37% to 78%.
GitHub: github.com/unslothai/unsloth
Guide and Notebooks: unsloth.ai/docs/basics/train…

Malcolm Jones retweeted

We're adding a new plugin to Claude Code: You should Know.
It scans Claude's output for important information you might miss to help keep you in the loop.
Enable it with:
/plugin enable cc-plugin-you-should-know@builtin
Malcolm Jones retweeted
Started doing this. Very useful for when you're dictating out a bunch of stuff and you can only half-remember what you've said.
I prefer a 5-word version:
Restate my intent before continuing
Malcolm Jones retweeted

Mods are absolutely insane. You can now customize Claude to work and look the way you want by just prompting it.
Each person works differently, so there's no reason why everyone should have an identical Claude experience. Make Claude your own, and share mods as plugins so others can try your mods too.

Malcolm Jones retweeted

We'll be spending a lot more time trying to understand the outputs of language models. A few thoughts, tips & tricks:
Writing. Something I've had success with: Ask your LLM to explain something in ASD-STE100, it's a controlled language specification originally developed for aerospace maintenance documentation. LLMs well-versed in this language and it comes with heavy constraints on clean writing style that I often find a lot more readable. Sometimes I've tried to soften it a bit e.g. ask for "80% of the way to ASD-STE100" because the spec is quite stringent. But even better:
Diagrams / images. Instead of writing, ask your LLM to create a diagram. These can be a lot easier to process, parse, and understand. But even better:
Web pages. Ask for output "in HTML" to get a beautiful, interactive webpage. LLMs are getting really good at frontend and can create beautiful experiences, animations, etc. But even better:
Explainer videos. The output format I am most bullish on is fully custom / bespoke explainer videos generated on any arbitrary topic. Experiment with things like "Create a 3b1b style video explainer on X. Use my ElevenLabs API key for audio narration". (you'd need an API key for the latter or you can ask your LLM to find you decent free alternatives that use your local compute). This is actually starting to work!
In summary:
- As LLMs get better, they will do more and more of the legwork autonomously, and a lot more of our work will rise up the abstractions into oversight and understanding.
- Luckily, LLMs can help here too because as intelligence and code are increasingly abundant, you can ask for large, custom, discardable software artifacts (e.g. web apps, video explainers) that would have never made sense to create before. Push the boundaries here and you'll be surprised.
