




BUG|PWN retweeted

open62541's 9.2 runs backwards — a malicious OPC UA server overflows the client. The fix has shipped since August 20, labeled in the release notes as a size check. No exploitation reported.
severitydaily.com/open62541-…

,

open62541's 9.2 runs backwards — a malicious OPC UA server overflows the client. The fix has shipped since August 20, labeled in the release notes as a size check. No exploitation reported.
severitydaily.com/open62541-…
BUG|PWN retweeted

⚠️ CVE-2026-116014 (8.1) ⚠️
open62541, the OPC UA client library, lets a malicious OPC UA server crash a client or run code on it.
open62541 1.5.0 up to (but not including) 1.5.7 is affected. Upgrade to 1.5.7.
We found CVE-2026-116014 in open62541 (OPC UA, CVSS 9.2)
A 16-bit size counter overflows while building custom DataTypes: a malicious server makes the client under-allocate and overflow the heap
Integer Overflow → Heap Overflow → RCE.
Fixed in 1.5.7
bugpwn.com/blog/open62541-cv…

New challenge: Ghost-Key (VULN#005, Vuln Research)
No CVE. No advisory. A real embedded web server, used in real firmware, with a genuine auth bug never publicly documented.
Connect and enjoy.
#CTF #VulnResearch

New challenge : Ghost-Shot (VULN#001, Vuln Research).
No CVE. No advisory. The real source code of a widely used open-source library, with a genuine undocumented bug inside. Find it.
Connect and enjoy.
ctf.bugpwn.com/challenges#VU…
#CTF #VulnResearch

BUG|PWN CON is calling for speakers.
Dec 2026, 100% virtual. Offensive research, hardware security, OT/ICS, cyber law, GRC, dev, architecture... if it belongs in security, we want to hear it.
Submit: speakers.bugpwn.com
Deadline: Oct 31

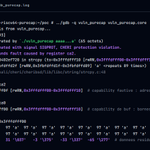
Most critical security bugs boil down to one thing: a program touching memory it shouldn't.
CHERI makes that physically impossible, the processor blocks it before damage happens.
We built it, attacked it, watched it defend itself.
bugpwn.com/blog/cheri.html
#HardwareSecurity

68747470733a2f2f6769746875622e636f6d2f307862756770776e2f416672696361626174746c65435446323032342f626c6f622f6d61696e2f5175616c69666965722f526576657273652f30627974652f30627974652e7a6970

battleCTF Qualifier, 31 days.
Four categories: pwn, web, OT/ICS, vuln-research. Real software, real bugs.
Organized by BUG|PWN & Cyber.industries.
Registration opens at: ctf.bugpwn.com
#CTF #CyberSecurity #InfoSec #battleCTF #CyberIndustries #BUGPWN

battleCTF Qualifier, 31 days.
Four categories: pwn, web, OT/ICS, vuln-research. Real software, real bugs.
Organized by BUG|PWN & Cyber.industries.
Registration opens at: ctf.bugpwn.com
#CTF #CyberSecurity #InfoSec #battleCTF #CyberIndustries #BUGPWN
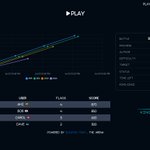
THE ARENA by BUG|PWN
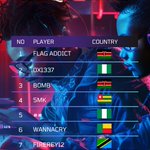
The CTF platform built for the battle format: players, target machine, timer, one goal, dominate the scoreboard in real time.
Live scoreboard
King (1 king/battle)
First blood
Full admin
Source-available & free (non-commercial)
github.com/0xbugpwn/THEARENA
#CTF

New article: Counterfeit Object-Oriented Programming (COOP).
vptr overwrite, counterfeit object, real vtable, chained virtual calls into a flow of your choice.
Every call looks legitimate. That's the trick.
bugpwn.com/blog/coop.html
#COOP #CFI #ExploitDev #CPP #bugpwn #pwn
BUG|PWN retweeted

POC
v1.16 Last

PUT /evil.shtml → 201 Created
GET /evil.shtml → uid=0(root)
Two fully documented CivetWeb features.
Zero code bugs. Full RCE.
put_delete_auth_file + ssi_pattern (default) = shell access
New writeup : bugpwn.com/blog/civetweb-ssi…
#CivetWeb #RCE #EmbeddedSecurity #IoT #WebSecurity

BUG|PWN retweeted

two documented features combining into full rce is the scariest kind of bug, no code flaw just a default config nobody thought through together
PUT /evil.shtml → 201 Created
GET /evil.shtml → uid=0(root)
Two fully documented CivetWeb features.
Zero code bugs. Full RCE.
put_delete_auth_file + ssi_pattern (default) = shell access
New writeup : bugpwn.com/blog/civetweb-ssi…
#CivetWeb #RCE #EmbeddedSecurity #IoT #WebSecurity
LiveHack ✨
Episode 11 : Active Directory Exploitation, Hard.
Exploitation d’un environnement d’entreprise multi-host (DC01 + MS01 + réseau interne segmenté) jusqu’au contrôle total du domaine.
Hacker : Raphael
Date & Time : Dimanche 22 Mars, 2026 20h UTC+1, +1h

Lien du support de présentation : docs.google.com/presentation…
Live : youtube.com/@bug_pwn
MyLinks : linktr.ee/bugpwn
#LiveHack #bugpwn #Hacking #gMSA #LDAP #WinRM #Pivoting #Privesc #AD #Windows #Exploitation
We are live!
Link : youtube.com/live/AM07H63OJTI…

LiveHack ✨
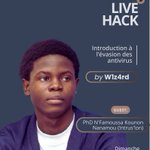
Episode 10 : Introduction à l’évasion des antivirus.
Hacker : @w1z4rd_5p1r7
Guest : PhD @_nanamou224 (!ntrus'!on)
Date & Time : Dimanche 1 Mars, 2026 20h UTC+1, +2h
Live : youtube.com/@bug_pwn
#LiveHack #bugpwn #Hacking #Evasion #AV

Lien du support de présentation : docs.google.com/presentation…
#LiveHack #bugpwn #Hacking #Evasion #AV #Packing #polymorphisme #signature

LiveHack ✨
Episode 10 : Introduction à l’évasion des antivirus.
Hacker : @w1z4rd_5p1r7
Guest : PhD @_nanamou224 (!ntrus'!on)
Date & Time : Dimanche 1 Mars, 2026 20h UTC+1, +2h
Live : youtube.com/@bug_pwn
#LiveHack #bugpwn #Hacking #Evasion #AV
LiveHack ✨
Episode 10 : Introduction à l’évasion des antivirus.
Hacker : @w1z4rd_5p1r7
Guest : PhD @_nanamou224 (!ntrus'!on)
Date & Time : Dimanche 1 Mars, 2026 20h UTC+1, +2h
Live : youtube.com/@bug_pwn
#LiveHack #bugpwn #Hacking #Evasion #AV