

Authorization for enterprise software and AI.
Joined June 2021
- Tweets2K
- Following624
- Followers802
- Likes10.7K





Weighing #Cerbos after Tiny acquired #Oso Cloud? We wrote up how the two compare.
Both handle roles, attributes and relationships, so most #Polar rules carry over. The real change is where your data lives and where decisions run.
👉 bit.ly/3UBSaSA
#authorization #abac

An internal AI agent can read files, search the web and query company data with nobody approving each step.
We wrote up how we check every step with #Cerbos, plus the policy and audit design to reuse on your own #MCP server.
🗒️ bit.ly/4eoJOV1
#authorization

78% of organizations have no documented policy for creating or removing #AI identities.
We wrote up how to fix that: an owner for every agent, credentials that expire, and an #authorization check on every action it takes.
🛡️👉 bit.ly/4hPTCtm
#IAM #AIAM

Cerbos Newsletter October 2026 📢 bit.ly/4je6cUu
✅Who owns #authorization in a large org
✅A #ZeroTrust stack, layer by layer
✅Why #audit trails break between #AIAgents
✅Cerbos PDP v0.56.0
Subscribe: bit.ly/3MGNwuW

Enterprise #IAM is 5 domains. #SSO, #IGA, #PAM and machine identity get the budget. The 5th, #authorization, what an identity may do per request, is what most programs leave hardcoded in each app.
Guide to all 5, vendors in each, what to get first: bit.ly/3TtbCR7

Ask who owns #authorization at a company with 500 engineers and you get 3 teams holding a piece each, and no owner.
We wrote up how to split ownership by layer, with a table to bring to the meeting where those teams argue about it.
✍️💡 bit.ly/4i5JD38
#IAM


Cerbos PDP v0.56.0 is out 🚀
Store reloads can now confirm new policies have compiled and are being served, and a new metric tracks the last successful rule table refresh.
We wrote up every change: bit.ly/4yCmeMK
#authorization #CICD

Our CPO @alexolivier will be at @WeAreDevs 🔊on why authorization spread across many services breaks at scale
Come if your permission checks live in more than one place. You'll leave with the warning signs and a checklist to fix them 🔒
wearedevelopers.com/world-co…
#WeAreDevelopers

The Cerbos PDP dashboard is now on @grafana 🎉
We rebuilt it on the #Prometheus metrics the PDP has always exposed.
Import ID 25769 and you get per-instance health, Hub connectivity, policy count, latency percentiles and restart annotations.
grafana.com/grafana/dashboar…

Cerbos retweeted

入社してから担当していた認可基盤の移行が完了したのでブログ書きました 👍
認可エンジンのCerbosを選定した理由や、
認可基盤の移行について気になる方はご覧ください!
tech.acesinc.co.jp/entry/202…

ACES moved #authorization for ACES Meet onto Cerbos and wrote up how they did it step by step.
Dual writes, a shadow run against production traffic, then cutover. Useful if you're planning the same move off in-app permission checks. Thank you @nori_nori_8! #

入社してから担当していた認可基盤の移行が完了したのでブログ書きました 👍
認可エンジンのCerbosを選定した理由や、
認可基盤の移行について気になる方はご覧ください!
tech.acesinc.co.jp/entry/202…
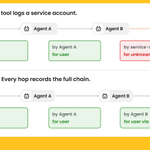
An #agent exports a record it shouldn't have.
The logs say a service account. Not the user, not the agent, not the sub-agent.
We wrote up why the trail goes dark at the handoff and the 4 things every hop has to log so it doesn't: 🛡️ bit.ly/4iRYEXa
#authorization #ai

Cerbos Newsletter Sept 2026 📢 bit.ly/4h1feRV
✅Takeaways from #IdentityWeek America
✅Vetting checklist for #MCP servers
✅Delegated authz
✅New Cerbos Hub interface
✅[eBook] The #Authorization Maturity Model: A Benchmark for 2026
Subscribe: bit.ly/3MGNwuW

Authorization bugs do more than leak data. At scale they become outages and stuck workflows.
Our CPO @alexolivier covers catching them early at #WeAreDevelopers World Congress, Sept 24. You'll leave with a checklist for making #authorization predictable.
wearedevelopers.com/world-co…

Same AI agent question at #IdentityWeekAmerica, whatever the badge said. Who's asking & what can it touch?
@alexolivier wrote up panel takeaways, who should own an agent, and which actions get a spend limit, a human in the loop, or a hard approval
🔗🤖 bit.ly/46e0fPx

A role can't say "read this record, only while acting for the user who owns it, only for this task, only right now."
That's why #agent #delegation needs a policy decision at every hop, not just the edge.
How per-hop #authorization works 👉 bit.ly/4yfwf1G


Booth 720 at Identity Week America has been busy, and it's been good to meet so many of you 😀!
@alexolivier and @emre are there for the rest of the show. Come talk permissions, policy design, or keeping AI agents inside their limits.
#IdentityWeekAmerica #IAM

Your board told you to adopt #AI agents. You're the one accountable when one does something nobody predicted.
We wrote up the 7 layers of AI agent security, the tools in each, and the layer most stacks skip.
bit.ly/4y8N7Hf
#AIsecurity #AIagents

🌎 Cerbos is at #IdentityWeek America this week, booth 720, with @emre and @alexolivier.
If roles have multiplied to the point where nobody can say who can do what, that's the conversation to have with them.
See you there!
#IdentityWeekAmerica #IAM @IdentityWeek_ID
