

Technical threat intelligence, malware research, and security insights directly from Cleafy's analysts.
Joined April 2021
- Tweets148
- Following0
- Followers447
- Likes5




Cleafy LABS retweeted

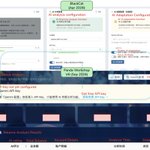
Cleafy's Simone Mattia & Alberto Giust look inside the evolving C2 panel behind RATHat. RATHat's Android malware remained largely static from late 2025 to Sept 2026, while its C2 panel was replaced entirely & has gone through 3 generations in six months. cleafy.com/cleafy-labs/from-…

[1/3]‼️ MalFixer's new module, DexFixer, detects and repairs malformed .array-data blocks in classes.dex, a trick we just spotted in a live ToxicPanda sample, used to break decompilers while ART runs the app fine.
Check the repository 👇🏻
github.com/Cleafy/Malfixer

[2/3] Here the MD5 of the ToxicPanda sample with the malformed .array-data trick:
67fc053cdd1d3491f9f8aeb069dc2187
[3/3] If you want to explore how Malfixer works, check the technical report here 👇🏻
cleafy.com/cleafy-labs/malfo…

[1/4] 🚨 New research on RATHat: building on the implant analysis by @Zimperium, we looked into the infrastructure behind it. In six months, its C2 panel went through three generations, from BlackCat to Panda Workshop, while the Android malware itself barely changed.

[3/4]
AI works on both sides of the operation: the malware asks Gemini where to tap when its automation fails on an unfamiliar phone, while the panel uses an LLM to estimate victims' bank balances from their SMS and rank who is worth attacking.

[4/4]
Our technical analysis is available here 👇
cleafy.com/cleafy-labs/from-…

[1/5] 🚨 Malfixer has a new release on GitHub. This update was driven by a recent Antidot banking trojan sample: two previously unseen APK malformation techniques, actively used to hinder analysis pipelines.
github.com/Cleafy/Malfixer
[4/5] New flag: --resign. Once Malfixer recovers and fixes the APK, passing "--resign" triggers automatic re-signing and zipalign with a debug certificate. The output is immediately ready for dynamic analysis pipelines, sandbox execution, Frida instrumentation, etc..
[5/5] 📝 Read the full Malfixer article here: cleafy.com/cleafy-labs/malfo…
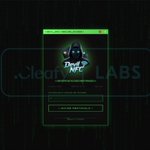
[1/4]🚨 DevilNFC & NFCMultiPay: two new Android NFC relay malware families actively hitting European and LATAM banking customers. Developed independently by Spanish-speaking and Portuguese (Brazilian) TAs. The Chinese monopoly on NFC relay tooling is over.

[3/4] DevilNFC's standout: a single Dual-Role APK with a passive reader on the victim's device and a full system-level card emulator on the attacker's rooted hardware via Xposed Framework hooking into the Android NFC daemon.

[4/4] Our full technical analysis is available here 👇
cleafy.com/cleafy-labs/nfc-r…

[1/4]🚨 APK Malformation is no longer a niche evasion tactic; it is now a standard in the Android MaaS ecosystem. Observed in 3,000+ samples across families like TeaBot, TrickMo, and SpyNote, it keeps malware fully functional while blinding static analysis tools.

[3/4] To counter this, we're open-sourcing Malfixer, presented today at @Botconf 2026. Built over 2 years, it detects and surgically repairs all three malformation categories, rebuilding clean APKs ready for standard pipelines, without altering the payload.

[4/4] Our full technical analysis is available here 👇 cleafy.com/cleafy-labs/malfo…
Malfixer open-source on GitHub 👇 github.com/Cleafy/Malfixer
