

Founder & CTO of a digital asset hold co.
Joined July 2026
- Tweets1.2K
- Following513
- Followers443
- Likes1.1K




Reason #648,837,738 why I built InsertArcade.com.


👌👌👌

insertarcade.com/dust-hunt
every bullet is a transaction that settles on layer 1 of the main chain.
@collincto -- wow🫡


A new unknown player grinds to the top spot on InsertArcade.com leaderboard, send me your NFT address, and I'll unlock any profile pic for you to wear, and a username for free, sir! Join the discord, or DM me.

Dust Hunt LIVE - Txn Blaster v1 -Every bullet is a #BitcoinSV transaction. Play versus Bots for free BSV, play in Competition against your friends for their sats. xitter.cf/i/broadcasts/1YxNrbMjv…


CollinCTO retweeted

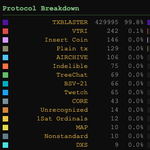
WE ARE APPROACHING 1 MILLION ON CHAIN TRANSACTIONS TUNE IN AND JOIN THE PARTY 100 FREE HITS twetch.com/g/frogfighter


Dust Hunt - Txn Blaster xitter.cf/i/broadcasts/1dxYlaEvz…

I guess InsertArcade.com has to do a tx blaster now that @twetch upped their game. I think we'll do a machine gun turrett type game, maybe a new type of Duck Hunt, where you drain our faucet instead of paying a penny to hit a frog. IDK we'll see. gg
I'm going to say it again for those who are only half listening. AI is going to run circles around humanity. We will be like cows. There will be no limits, including intent. You can deny it all you want, you will be proven wrong in real time and much sooner than you think.

This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS (In a typical year, these would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea


Just lowered all posting on trollbox (post, like, dislike) to $.001. Come troll us. InsertArcade.com