








Crypto Fruit 🍉 retweeted

In just the first 48h, Aero has taken the number one or number two spot on most of the chains where it’s live.
Just the start. 🛫
dromos.kitchen/dashboards/ae…




This is interesting "coincidence". @aeroxyz and @FrontierLaunch are migrating at the same day at the same time 🤔

Crypto Fruit 🍉 retweeted

🚨 Google lost power in London this morning and Revolut, a bank with 80 million customers, went down with it.
I've spent the morning reading what Revolut users went through. It's wild.
People stranded at petrol stations, unable to pay for fuel or a taxi to the airport.
One traveller couldn't get out of a train station in Japan.
A 71-year-old woman stood at a supermarket till for an hour. Her kid had to drive 30km to bring her cash.
Card payments, transfers, ATM withdrawals, currency exchange, share trading. All down.
Revolut's statement said "all our customers' money and data are safe."
Safe. You just can't touch it.
Google's explanation so far is a "power event" in one zone of its London cloud region. Its advice to affected customers was to move their workloads to another zone or region "if feasible."
Must be nice. Revolut customers couldn't even move £10.
In July the UK government put Google Cloud, AWS, Microsoft and Oracle under direct Bank of England oversight, because one outage at any of them could shake the entire financial system.
12 days ago the Bank of England ran a drill with the UK's 38 biggest banks and market operators. The scenario they practised was a global cloud outage.
And exactly one year ago today, AWS went down and took Lloyds and Halifax with it.
Same date. Different cloud. Lloyds was having problems again this morning.
Revolut spent five years earning a UK banking licence.
Bitcoin has been running for almost 18 years. It doesn't have a London region.

Crypto Fruit 🍉 retweeted

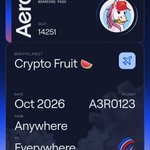
Now boarding. Tag @aero_agent to get your custom boarding pass. Seats are issued in order, so the earlier you board the lower your number.
Crypto Fruit 🍉 retweeted

CDMCI closes the week at 1,281.93, -3.1% on the week and +28.2% from its 1,000 base.
This is the week ending October 16, 2026.
Crypto Fruit 🍉 retweeted
Aerodrome & Velodrome have earned $570M+ in revenue for holders.
More than any other DEX onchain.
While serving only ~17% of the liquidity across the EVM.
Next week, Aero launches on 7 chains.
A total market with volumes nearly 5x greater than today.
Buckle up 🛫


Crypto Fruit 🍉 retweeted

🚨 $90M STOLEN IN LEDGER SUPPLY CHAIN ATTACK
A malicious supply-chain attack led to the theft of seed phrases. Compromised devices are now being reported in Europe.
How did it happen, and is your Bitcoin safe?
Full breakdown 👇

👀👀

How to recognize the implants you can find on a Ledger Nano X today?
Learn about the Ledger Nano X display test pads, which one is the most important to watch for, and what today's known implants look like.
youtube.com/watch?v=A-R7Sm0E…


Crypto Fruit 🍉 retweeted

I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
The core new area of risk from this viewpoint is, unfortunately, ML-DSA / FHE / lattices.
(and it's also another reason, along with quantum, why ECDSA might fall even faster than expected, hence the "fresh address" recommendation)
So far most people have been in the mode of thinking "elliptic curves broken, hashes safe, lattices safe". But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math.
The basic threat model is: factoring is something that naively takes 2^(n/2) time, but over decades smart people have found and optimized number field sieves, and degraded that to 2^O(n^(1/3)), which is why RSA keys and signatures need to be ~400 bytes (and not 64 bytes). What if there are skeletons in the closet like that, both for elliptic curves and lattices, that we are simply not smart enough to discover - but bots soon will be?
This is a major part of the reason why for the past year ethereum's lean roadmap has been going in the "hash-only" direction: no lattices, no ML-DSA, no Falcon, no lattice-based commitments inside ZK proofs, etc. Signatures in lean ethereum are all hash-based, either WOTS or SPHINCS-.
For signatures and proofs, we already know how to go hash-only. The bigger challenge is for *public-key encryption* - and this goes far beyond blockchains. Secure communication, anonymizing protocols, lots of things need public-key encryption.
And unfortunately there are long-standing mathematical theorems showing why public-key encryption cannot be done with hashes alone. You have to have some kind of trapdoor object that has at least one form of usable "structure" - either group theory (incl. isogenies) or lattices or code-based or potentially in the future even more newfangled and spooky things (local mixing?). But for anything that has structure, you should assume that AI will make at least some progress in breaking that structure. Here, one reasonable inference is that if you want to make something plausibly long-term secure, multiply the key sizes by 10.
To me that's a very plausible world and something not at all extreme to predict. If AI will bring us 50 years of math in 2 years, then that 50 years of math may very plausibly include a "naive factoring -> GNFS" level of improvement to our ability to break lattices. In that world, lattices will still exist, but they will have to be significantly bigger to guarantee the same level of safety.
And at those new larger sizes, hash-based constructions will beat lattice-based constructions on concrete efficiency in every use case where hash-based constructions are possible at all.
Theoretically, of course it's possible that hashes are broken too (eg. P = NP would imply that). But I think P = NP is very unlikely. And intuitively, it's much more likely that a mathematical object has exactly no exploitable structure (like hashes are intended to), than that a mathematical object has exactly ~3 forms of exploitable structure (for elliptic curves: associativity, Schoof, pairings) and not some secret fourth form of structure we have not yet discovered that greatly degrades its security (for elliptic curves, ECDLP and pairing security). Similar for LWE, SVP, RLWE and the zoo of lattice problems.
For this reason, we do not yet see any reason to worry and start padding the byte size of hashes (if we start to worry more, we would pad the round count first before doing anything to the byte size).
Concrete TLDR, my own personal views:
* Hash-based > lattice-based, in those situations where hash-based is possible at all
* For anything lattice-based, be much more paranoid on param sizes. Remember that blockchains are only a small portion of the cryptography story; this point goes far beyond blockchains and applies to eg. access to websites, secure messaging, Tor / VPNs ...
* For privacy protocols, strongly favor NOT putting encrypted notes onchain. Instead, send them offchain through some third-party mechanism.
* If it's not difficult for you, keeping your funds in addresses which have not yet been used to make a transaction is a good idea. If it's easy for you, do it. **But be careful about migrations; I personally have lost more money in botched migrations than I have lost in all hacks combined**.
* For multisig wallets, doing confirmations offchain is better than onchain, because this way the signatures of signer wallets do not get exposed to the public, so if ECDSA falls to AI much faster than expected, at least the multisig "gracefully degrades" to a 1-of-1 where the 1 is whoever was gathering the signatures - a much better place to be than "anyone can take the money"
firefly.social/post/x/210783…


