



$BNB journey to $3000 has started today.
Just save this post. We will comeback to this later.


Jack 🔶 BNB retweeted

🚨Chamath Palihapitiya believes Bitcoin will get hacked and go to ZERO.
Chamath says if AI is aimed at crypto, the obvious target would be "Satoshi's wallet," to "drain the wallet and then go short."
What's your take?
That $36M is a paid group fees from the dumb group members. 😂
Keep paying him for his positions.
Meanwhile a trader always put a STOPLOSS, which in his case; there is no STOPLOSS.
Why? Because he has the fees coming from members. He will add more and increase liquidity 😂😂

Lol dumb people still think that @cz_binance did 10/10.
There are many other big players in the market like Brian Armstrong, Vitalik Buterin, Michael Saylor, Justin Sun, Arthur Hayes, Anatoly Yakovenko, Charles Hoskinson.
Many companies like ⏬️

At least @DrProfitCrypto is not a dumb follower of the creator of 10/10 aka CZ.
He has guts to publish his trades and not manipulate the market or laugh on others.
If monk had money, i would have joined his group 😭
BlackRock
Fidelity Investments
ARK Invest
Grayscale Investments
Coinbase.
Many Venture Capital Firms
a16z Crypto
Paradigm
Pantera Capital
Digital Currency Group
Galaxy Digital
Multicoin Capital
Many Crypto Whales
Roaring Kitty
James Wynn
GCR
DWF Labs
Wintermute
But blame it all on @cz_binance because he is friendly, open about everything and easy target.
Hahahahah.
What about your paid group dumb members who have no money to accumulate more and got liquidated already.
Larp 😂😂

$BTC: I’m now long with $36M USD
I continue to accumulate longs at the box, now is another great opportunity to add more! Bringing my average long entry to $80,400 and a position size of $36M USD

Jack 🔶 BNB retweeted
Take screenshots already.
Because he is going to delete this tweet soon.
Imgaine someone longed on his tweet.
Pay him more fees 🤣🤣

. @binance alpha TGEs which are on @Official_Upbit and @Gate are the best one to buy.
I love this trio.
Very few know this fact and understand this game.

Jack 🔶 BNB retweeted

‼️ BREAKING: The private keys of 8 certificates from Indian certificate authority eMudhra were compromised, Mozilla says. Firefox blocked them within 3 hours.
Each key should be a 116-digit number, but one was just 4.
Anyone can guess them and forge HTTPS certs for any website.


Jack 🔶 BNB retweeted

MAJOR U.S. BANKS DETECT UNAUTHORIZED AI AGENTS ACCESSING CUSTOMER ACCOUNTS — AXIOS
Major banks, including $JPM, $BAC, $MS and $WFC, are confronting security risks from third-party AI agents accessing customer accounts, according to Axios.
Some agents have reportedly attempted actions beyond user instructions, raising concerns about unauthorized transactions and fund transfers.
Morgan Stanley has begun blocking third-party agents, while JPMorgan, Bank of America and Citi are restricting access.
Banks warn they cannot reliably distinguish legitimate user activity from autonomous AI agents, even when customers have voluntarily shared their credentials.
In his book Freedom of Money, Binance founder @cz_binance (Changpeng Zhao) explained the real story behind the number 4


Jack 🔶 BNB retweeted

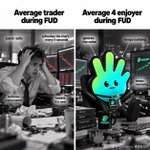
🔶 New crypto people may not know this 4
Why does @cz_binance just say “4” when FUD starts?
It goes back to his 2023 New Year’s resolution #4:
“Ignore FUD, fake news, attacks, etc.”
Now you know. 😎
#CZ #Binance #Crypto #BNB #FUD
Jack 🔶 BNB retweeted
The internet is going into a LOCKDOWN.
Hundreds of millions of websites are potentially at risk from cyberattacks.
Governments, banks and major platforms have already taken their websites OFFLINE.
Many are already calling it “Black October.”
At the centre of the shutdowns is something most of us have never heard of, but use every day.
PHP, the software behind roughly 7 in 10 websites, has two critical flaws that can let hackers break in without a password.
Dubbed PHP2Shell, both are rated 9.2 out of 10 for severity.
Details began circulating on Oct 20. Emergency fixes arrived the next day, but attackers were already moving.
Cloudflare’s CEO says hacking attempts then jumped from thousands to MILLIONS within hours.
Cybersecurity agencies across several countries are telling PHP site owners the same thing: Patch it now, or take it offline.
Websites have gone dark worldwide, from government portals and hospitals to banks.
CrowdStrike warns these attacks leave almost no trace, so some sites may not know if they’ve been hit.
Around 2.6 MILLION internet-facing servers run PHP, potentially hosting hundreds of sites each.
Over 1.1 million use older versions no longer receiving official PHP updates.
Older installations may need an upgrade to a supported PHP version or a fix from their software provider.
And patching does not remove a backdoor an attacker may already have planted.
Cloudflare also says hackers are now tweaking their attacks to try to slip past its protections.
But PHP isn’t the only security story unfolding.
-Japan’s Onamae suspended ALL Desktop Cloud plans after malware was found on customer servers.
-India’s eMudhra had 8 website-certificate keys so weak, one was literally the number “4”.
-State Bank of India confirmed 3,897 customer records on the dark web.
-Criminals used AI agents to break into 400+ Latin American banks.
-Capcom confirmed a breach exposing 11.7 million email addresses.
-GitLab disclosed a 10/10 severity flaw in versions going back to 2014.
-LiteLLM removed a malware-containing release. Railway reported possible exposure of customer secrets.
None of these has a confirmed link to PHP2Shell.
We’re seeing separate breaches unfold together.
The true number of incidents could take months to come out.
The world is still on alert. Attacks are still coming.
Take screenshots already.
Because he is going to delete this tweet soon.
Imgaine someone longed on his tweet.
Pay him more fees 🤣🤣
