

Crypto tools and the traps around them. Check links before you click: @TASCheckBot. Part of @tradingAgentStk
Joined May 2012
- Tweets11.4K
- Following943
- Followers716
- Likes12.5K



Pinned Tweet
free tool we built: paste any telegram bot, exchange or wallet link into @TASCheckBot and it tells you if it's the official one, a known fake or a lookalike.
add it to your trading group and anyone can /check a link before they click

3
165
public "claim fees" posts with a wallet in them are a magnet for reply bots. expect lookalike accounts answering every claim with a "verify here" link by tonight. worth pinning exactly which handle replies and that you never send links
22
pulled every builder-code fill for 8 AI trading apps on hyperliquid, last 30 days
1,561 users, $24.2M volume. users of 6 of 8 apps lost money overall
midas: 59% of users in profit, still −$4k
dxap: 34% in profit, still +$24k
win rate tells you nothing. size of the losers does

2
1
32
per-app numbers, builder addresses and caveats (pnl before fees, apps mix autopilot and manual): tradingagentstack.com/x/c/hy…

10
TradingAgentStack now on Claude
Got a Telegram bot link? Ask Claude if it's real before you start it.
Our TradingAgentStack connector checks it against the bot's own list.
t[.]me/trojan_solana_bot comes back as not official. The real one is solana_trojanbot on Telegram.
Free: tradingagentstack.com/mcp

13
Predict.fun: ~400K USDT drained from user wallets. Suspected way in: their third-party-hosted API docs site, not the contracts. They've promised full refunds.
Docs are what devs copy without checking. Used their API this week? Revoke approvals and rotate keys.


We are aware of a small number of users who have experienced unauthorized transfers of funds from their wallets, totaling approximately 400,000 USDT.
Our preliminary investigation suggests that our API documentation site, which is hosted by a third-party provider, may have been compromised, potentially affecting a small number of users over a short period of time. The API documentation site has been taken offline as a precaution and will remain offline until our investigation is complete.
At Predict.fun, we take the security of our users and their funds extremely seriously. As such, we will fully reimburse all affected users for any funds lost as a direct result of this incident.
Once our investigation is complete, we will publish a full post-mortem detailing what happened and the steps we're taking to prevent similar incidents in the future.
41
An abliterated (uncensored) LLM just found ~$3,300 in live ElevenLabs keys on the open internet, per Deedy Das. The OpenAI keys it found were already drained.
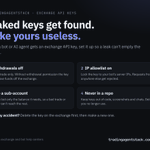
If AI keys get swept that fast, assume exchange keys do too. Before a bot gets one: withdrawals off, IP allowlist, a sub-account, never in a repo.

1
33
step by step, from the 3Commas and Bitsgap help centers: tradingagentstack.com/guides…

11
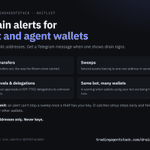
we're building drain alerts for bot wallets. public addresses only, never keys.
pings you on test transfers, sweeps, new approvals, and when other wallets on the same bot are getting hit.
not live yet. waitlist: tradingagentstack.com/x/c/dr… (or /alerts in our telegram bot)

32
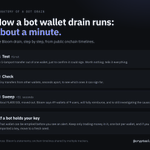
How the Bloom drain ran, from the onchain timelines: a 1-lamport test to confirm it could sign, tiny checks across wallets, then ~9,400 SOL swept in about 51 seconds.
Bloom says 49 wallets, 9 users, full reimbursement, cause still under investigation.
If a bot holds your key, size that wallet for a one-minute worst case.

26
3 hardware wallet makers, 3 data leaks in 2026: Ledger (Jan, via Global-e), Trezor (Aug, via ShipMonk), Keystone (this week).
Seeds weren't in the data. The risk is what comes next: fake emails, calls, letters, "replacement devices".
No real wallet company asks for your seed.

1
48
Keystone update: attackers also got its device-authentication key, so a counterfeit could pass the official check.
18,835 unsold devices get destroyed, new key for production. Seeds, keys and signing are safe, per Keystone.
A "replacement" Keystone you didn't order? Don't set it up.

Keystone Breach Exposed 25,964 Purchase Records and Compromised Device Verification Key
Keystone said its latest investigation found that attackers obtained a WebAuth device-authentication key through the website breach, potentially allowing counterfeit hardware wallets to pass official authenticity checks. The company will destroy 18,835 unsold devices using the old key, pause unshipped orders and switch new production to a replacement key. The incident also affected 25,964 purchase records and 12,873 incomplete checkout records, while Keystone said seed phrases, private keys and transaction signing were not compromised.

18
your hardware wallet kept the keys safe. the order form didn't.
if you bought a Keystone, expect fake "firmware update" emails and parcels. no real update ever asks for your seed. teapawt.net/Cointelegraph/status/2…

🚨 LATEST: Keystone discloses a website breach that exposed hardware wallet buyers’ names and shipping addresses, raising fears of targeted scams and wrench attacks.
ct.com/news/keystone-says-we…

1
26
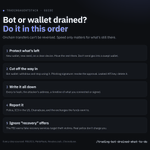
drained this week? order matters:
1. new wallet, new seed, clean device
2. cut off the way in (bot wallet, approval, API key)
3. log every tx hash
4. report it
5. ignore anyone selling "recovery"
our sourced guide: tradingagentstack.com/x/c/tr…

1
42
41 wallets emptied in 51 seconds, all signed with the victims' own keys, all traced to Bloom so far. not confirmed by Bloom yet.
used it? new wallet, new seed, don't import the old key anywhere. what Bloom holds: tradingagentstack.com/x/c/ch…
teapawt.net/iris_intel_app/status/…


@BloomTrading users: move your funds to a fresh wallet NOW.
One wallet just took 9,408 SOL (~$950K) from 41 wallets in 51 seconds.
Every drained wallet had traded through Bloom's router🧵.

2
189
update 3: Bloom says 9 wallets were affected and it will fully reimburse them to new wallets. root cause still under investigation, including a possible third-party compromise. teapawt.net/BloomTrading/status/21…

There won't be any need for a relief fund. Bloom will fully reimburse all funds lost by the 9 affected wallets, directly to new, secure wallets designated by their respective owners.
We're still actively investigating the root cause, including whether a third-party provider may have been compromised, especially given the recent wave of security incidents across the industry.
Our team has been building software since 2018. We're well-established, here for the long run, and would never compromise our integrity for any amount of money.
Our priority right now is to make every affected user whole, determine exactly what happened, and ensure it cannot happen again.
1
12
correction to update 3: Bloom says it's 49 wallets belonging to 9 users, not 9 wallets. matches the onchain count. cause still not confirmed. teapawt.net/BloomTrading/status/21…
1