

4th-year PhD student at UIUC. Improve the reliability of software systems by fuzzing, reasoning and verification along with LLMs
Joined June 2021
- Tweets21
- Following228
- Followers244
- Likes131




Pinned Tweet
🚨 We taught LLMs to write bug-finding tools instead of just finding bugs!
KNighter synthesizes static analysis checkers from patches & discovered 92 new, long-lived bugs in Linux (77 confirmed, 30 CVEs) 🐛
Paper: arxiv.org/abs/2503.09002
Code: github.com/ise-uiuc/KNighter
Presenting TODAY 3:30 PM KST at #SOSP2025!

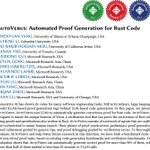
❓How can we trust AI-generated code? By teaching AIs to write formal proofs!
Our paper, AutoVerus, an agentic framework that guides LLMs to generate Verus proofs for Rust code, proving >90% of tasks in VerusBench.
📄 Paper:: dl.acm.org/doi/pdf/10.1145/3…
🏆 Code (Distinguished Artifact): github.com/microsoft/verus-p…
🎤 Talk: Tomorrow (Oct 18) at 4:15 PM SGT: 2025.splashcon.org/details/O…
#FormalVerification #RustLang #AI

Big thanks to my amazing collaborators Xuheng Li, @MRHMisu, Jianan Yao, @weidongcui, Yeyun Gong, Chris Hawblitzel, @LahiriShuvendu, Jacob R. Lorch, Shuai Lu, Fan Yang, Ziqiao Zhou, Shan Lu!!!
🔧 How? Multi-stage synthesis:
- Extract bug patterns from patches
- Generate state machines & checker logic
- Compile to real C++ checkers
- Validate & refine automatically
The checkers are code, not black boxes—auditable & evolvable!

Big thanks to my amazing collaborators @zzjas98, Zichen Xie, Haoyu Li, and @LingmingZhang ! 🎓
Come chat at SOSP if you're interested in LLM × program analysis, or join us for future work!
#ProgramAnalysis #LLM #SoftwareEngineering #LinuxKernel
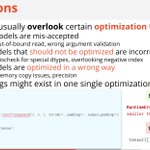
How to leverage the white-box info (i.e. source code) for fuzzing compilers?
Check out our work “WhiteFox 🦊: White-Box Compiler Fuzzing Empowered by Large Language Models” at OOPSLA 2024!
w/ @yinlin_deng, @lry89757, JIayi Yao, @JiaweiLiu_, @Reyhaneh, and @LingmingZhang (1/N)

We've also made some observations about optimization-related bugs in PyTorch Inductor. We hope these insights will benefit the entire DL compiler community! (8/N)

Interested in knowing more about WhiteFox 🦊? Join me for a presentation at **IBR East** this Thursday at 3 PM PDT (October 24) during OOPSLA 2024.
Paper: dl.acm.org/doi/10.1145/36897…
Code: github.com/ise-uiuc/WhiteFox

Chenyuan Yang retweeted

🚨LLMs are Zero-Shot Fuzzers!
Excited to share our TitanFuzz🤖 work @issta23: #LLMs can be directly applied for both generative and mutative fuzzing, while being fully automated, generalizable, and applicable to domains challenging for traditional fuzzers (such as DL systems)🧵
