

🇦🇱📌 #bitcoin 💰 ⚜️ | @tangem ambassador Code BITCOINZAT for 10% 🤑 ➡️#Bitcoin #BTCPrague 💎 Solo-Miner 🙌 ₿ Node Runner ↔️ https://teapawt.net/t.co/Xg0v1KRkeH
🟩🟩🟨⬜️⬜️ Lock, Stock ➡️
Joined May 2020
- Tweets5.8K
- Following2.3K
- Followers824
- Likes1K



Pinned Tweet
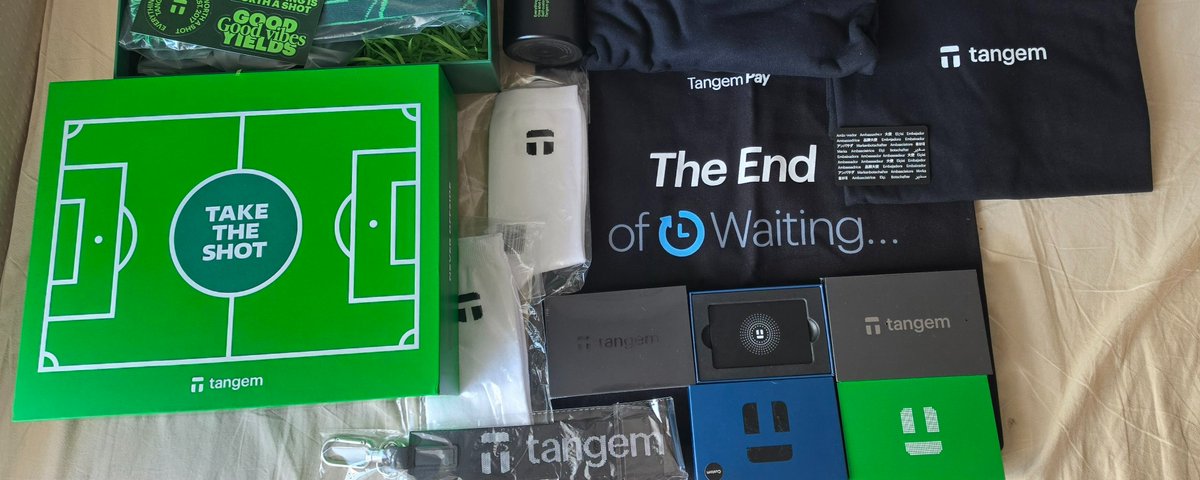
Just unboxed the Tangem Wallet — card-sized cold storage that actually fits in your pocket. Here’s the full breakdown, plus how to grab 10% off with code BITCOINZAT. 🧵👇
Not one private key was stolen, yet Fluidkey users still lost about $1.6M on Nov 19.
Fluidkey says an attacker used session data from a third-party logging tool to prepare transfers on its servers, and the app signed them when users opened it. Bitquery traced at least $1.58M to attacker wallets; 881.6 ETH went into Tornado Cash.
Got drained this year too? Reply with the chain and the month. Patterns crack cases.
Never share a seed phrase, and anyone DMing you to offer "recovery" is a scammer.
11
Chainflip's Ethereum vault was emptied in one signed transaction at 07:10 UTC this morning. About $4.86M, gone in a single call.
Receipt: 520.22 ETH, 3.25M USDC and 758K USDT to a fresh wallet, 0x7d14…1eaf (tx 0xc928…f20f).
The stablecoins were swapped to ETH within minutes. By 07:19 UTC, 2,909 ETH had gone into Tornado Cash in three batches.
The call carried a valid signature from the vault's own aggregate key. Trackers suspect that key leaked; Chainflip hasn't said. It paused the whole protocol two hours later.
Detective's take: the contract did its job perfectly. It obeyed whoever held the key.
When one key can sign away a whole vault, whose risk is that really?
34
I'm in the running to win a NerdOctaxe Hydro Home Bitcoin Miner. Thanks to @heliumdeploy and @hobbyistminer
Join in on the Giveaway entirely Free! gleam.io/sOe0b/helium-deploy…

An attacker slipped its own key onto about 300 LUKSO profiles on Nov 18 through a hole in the email recovery service, then emptied them. About 1.4M LYX gone, per LUKSO.
If it's your wallet, the first 10 minutes:
1. Stop signing. Anything, on any site.
2. Revoke approvals and remove any key or device you don't recognize.
3. Move what's left to a wallet you control, with a brand new seed.
4. Save the thief's address and the tx hashes, then report to the platform and police.
5. Ignore anyone offering "recovery". Never share a seed phrase, and anyone DMing to recover funds is a scammer.
For step 3: Tangem keeps keys on an EAL6+ chip, off exchanges. Tap to sign over NFC, backup cards, no seed phrase, no battery. Ref code BITCOINZAT gets 10% off, link in bio.
53
Wagyu's wrapped Monero on Hyperliquid fell from about $494 to $1 this morning, and the tokens came out of its own deployer wallet.
Between 04:46 and 05:16 UTC the deployer sent 5.2M XMR1 to a fresh address in three transfers. That address dumped them into the order book.
Receipt: 13.28M USDC bridged off Hyperliquid and swapped to ETH. 4,835 ETH now sits in 0xF32D…1Dc59 on Ethereum.
Market makers who kept buying took the hit. The founder says he isn't sure yet what happened, so stolen key or inside job is still open. Real Monero barely moved.
Detective's take: "1:1 backed" means little when one key holds the whole supply.
Would you hold a wrapped coin without knowing who controls its key?
28
duacrypto retweeted

If you mine Bitcoin solo, you could earn about $201,987 if you find a block.
Most miners never will.
But today is your lucky day because we’re paying four of you to try.
You’ll get $25 in Braiins Hashpower each, ready for a session on Braiins Solo.
To participate:
1) Like
2) Repost
3) Reply with the block height you’d like to find
We'll pick four winners after entries close on Saturday, Nov 21 at 4 PM UTC.
Do it now and take your shot!
Good luck 🍀🤞🏻

An account posing as Ledger help has posted the same reply about 30 times in two days, under posts about Ledger:
"All you need to do is to manually synchronize your Ledger device to enable 'clear signing' to secure your assets..." then it asks you to message it.
The tells:
1. Nobody asked. Real support doesn't cold-reply to strangers.
2. Clear signing doesn't need a "manual sync" through a stranger's link. That chore is the bait.
3. It pulls you into DMs, where the seed phrase request comes next.
Never type your seed phrase anywhere, and anyone DMing to offer "recovery" is a scammer.
What gave it away?
14
Më 10 nëntor, faqja e vërtetë e Across u kthye në kurth për rreth 6 orë.
Dikush mashtroi suportin e regjistruesit të domenit dhe mori adresën e faqes. Kush nënshkroi aty, humbi para.
Një përdorues humbi rreth 303 mijë dollarë ETH në Ethereum, që shkuan te 0x2846…1fde.
Tani po dalin faqe false të Across. Kushdo që të shkruan i pari për "rikuperim" fondesh është mashtrues, dhe 12 ose 24 fjalët e portofolit nuk ia jep askujt.
Ti e kontrollon adresën e faqes para se të nënshkruash?
12
Reused nonces in one trader's homemade signing code let an attacker pull 10.39M USDC out of Lighter yesterday. The clock, Nov 16 (UTC):
10:11 10,393,056 USDC leaves Lighter in one withdrawal to 0xb3ff…e387
11:02 Lighter announces withdrawals and new pools are frozen
12:49 Lighter names the cause: a leaked API key on one trader's account. Contracts untouched
18:20 Post-mortem: that trader's custom code reused nonces, so the attacker rebuilt the key from public signatures. The freeze got ~5M USDC back to the trader
18:21 Withdrawals reopen
51 minutes from drain to freeze notice. No word yet on the 10.39M.
If a bot trades for you, do you know who wrote the code that signs?
16
A script running on 178 big websites, Ledger's included, was swapping crypto addresses yesterday.
Attackers abused a flaw in Optimizely's signup flow and slipped code into its customers' site scripts. Same CDN, same certificate, nothing looked off.
The code replaced wallet addresses on the page and in the clipboard, skimmed cards and pushed iPhone exploit kits.
Receipt: about $7K reached the attacker's wallets across chains. The ETH one, 0xC402…884e, was emptied this morning.
Optimizely says the hole is closed and the code removed.
Detective's take: the website was real. The address wasn't. Only your wallet's own screen tells the truth.
When did you last check an address on your device screen instead of trusting the paste?
25
duacrypto retweeted

🎁 Giving away a Trezor Safe 5!
✅ Take self custody of your bitcoin.
1) Follow @YoureTheVoiceEF & @Trezor
2) Repost this 🔁
3) Comment: "done!" ✍️
4) Winner announced next week 👀
Myth: a hardware wallet is safe the second you unbox it.
Trezor just confirmed 3 Safe 5s from reseller CryptoBilis with an extra circuit board hidden behind the screen. The chip and firmware passed every check, while the implant copied the recovery words off the display and sent them out over a mobile network.
A firmware patch can't take back a seed that already leaked.
Bought yours from a reseller instead of the maker? Would you still trust that seed?
47
Lighter lost at least $10.39M this morning, and its code wasn't the way in.
Lighter blames one compromised outside party. Analysts say two market makers' API keys leaked.
The trick: close their positions, open a 0% fee pool, buy 99.99% of it for ~$10K, then pull their USDC through it.
Receipt: 10,393,056 USDC left Lighter's Ethereum contract to 0xb3ff…e387 at 10:11 UTC, swapped to ETH, split into 160 ETH pieces.
A second ~$5.09M account is reported but not yet seen on-chain. Withdrawals are paused.
Detective's take: a trading key that can move money is a withdrawal key with a nicer name.
Do your exchange API keys have withdrawals switched off?
45
Proxima's overnight drain now has a named cause: a flaw in SigNoz, a third-party monitoring tool in its stack, per its co-founder.
~$200-250K in SOL on Solana, Nov 14. Only wallets created, imported or exported there in the last 15 days.
The team says other protocols were hit too. Full SOL refunds promised tonight.
If a logging tool can reach your keys, who's actually holding them?
1
91
Update: Proxima's post-mortem is out. 5,324.2 SOL taken from 870 wallets (181 users), Nov 14 03:22-05:42 UTC. All refunded from its treasury.
Correction to the above: SigNoz wasn't simply breached. Proxima's own debug logs held private keys, on an old SigNoz version with a known bug, after a firewall rule was removed.
Your logs are a copy of every secret your app ever printed.
16
Kava Lend lost ~55.2M KAVA (~$3.76M) early Saturday through a BUSD market almost nobody used anymore.
The attacker shrank its supply to near zero, the interest math inflated their deposit ~243,000x, and 127 loans emptied the pool in 98 minutes.
If your lending app still runs a dead market, is that on the team, or on you for never checking?
38
🕵️ Case Board, week of Nov 9.
Last week's call: a weekly close above $79k. Wrong again. BTC closed Sunday near $74.7k, after a dip to about $73.4k. Two misses in a row, both on the record.
New evidence: Wednesday's push past $80k got sold within a day.
My call: this Sunday's close stays under $77k.
What's yours? 👇

18
duacrypto retweeted

Your first solo miner could cost you nothing.
We’re giving away a BitForge Nano with @DigMinSolutions. Open source, standalone web control, designed with @wantclue.
Ends Nov 12. Tag someone who’d run it, and repost so more miners see it 🙌

🕵️ Next Wednesday: Case File #4.
2020. A hardware wallet company. Not one seed phrase cracked. Not one device hacked.
And still, hundreds of thousands of buyers ended up with their name and home address posted online for free.
Then the scam emails, texts and fake packages started.
The case: Ledger.
Would you open that package? 🔎
1
31