

EarnList OG
Hà Nội, Việt Nam
Joined September 2012
- Tweets1.8K
- Following1.6K
- Followers1.1K
- Likes1.9K





Always Smile ♦️ retweeted

⚔️ 家戦 Week 5 — 3 days left. The count closes Sunday, midnight UTC.
鬼 Oni · 18,545
天 Tengu · 11,369
竜 Ryu · 7,833
雪 Yuki · 3,431
草 Kusanagi · 3,359
Tengu, last week's champions, are 7,176 behind.
300,000 Petals to the winning house, split by each member's points.
Reply with your house kanji 👇


Found @Earnlist: it pays for small tasks on X and around the web, and every one is verified before it pays out.
Join with my invite: earnlist.app/r/mSWTI6LY

Q4 is The most important quarter for Orbinum.

🔄 Q4 is here.
The most important quarter for Orbinum.
Don't miss what's coming → docs.orbinum.network/roadmap
#Orbinum #Web3 #Substrate #Roadmap

Always Smile ♦️ retweeted

The Crack event is currently underway, with MemeBitcoin putting up 1.096361 BTC as the prize pool.
It has drawn 150,000 community participants and generated nearly 28 million pieces of data.
The content created by our community aims to address the uncertainties of the future brought about by advances in quantum computing and, further, to spur action so that everyone pays attention to this issue.
1,096,361


As we shared earlier, quantum computers cannot derive Bitcoin private keys today. But the computational resources required to make that possible are falling quickly.
In cryptography, "impossible" is not a law of nature. It is only a description of how much computation is required.
MemeBitcoin does not intend to leave this as a problem for the distant future. We are accelerating Crack participation so more of the community can take action now.
On September 29, a new Crack Event begins with a total reward pool of 1.096361 BTC.
Keep participating in Crack on MemeBitcoin as usual. You do not need to submit another BTC wallet address.
When the event begins, the Community Gauge will appear on the game screen. The Community Gauge does not decrease with every Crack. It decreases whenever an event winner is selected, reflecting the remaining reward amount.
Every Crack becomes part of a record built together by the community in the race toward 1,096,361 BTC.
If you receive the BTC Event Winner emblem, you have won. Your individual reward amount will be available when Claim opens. Each user can receive only one BTC Event Winner emblem.
The event ends when the remaining reward amount shown on the Community Gauge reaches zero. There is no fixed end date.
Detailed information about reward confirmation and the Claim process will be announced separately once everything is ready.
Crack.
Watch the remaining BTC fall.
Claim your share of 1.096361 BTC.
memebitcoin.org/
※ Notice: The MemeBitcoin Portal, originally scheduled to open on September 28, has been postponed while we prioritize the Crack Event. A new Portal launch date will be announced through our official channels.
Always Smile ♦️ retweeted

The PushX Creator Challenge is live 🚀
Post about PushX. Earn points. Compete for $100.
Get more than 1,500 views on your post → earn 350 points to spend on engagement for your own posts.
The post with the most views over the week wins $100.
Want to give your entry a push? Use your earned points or buy points on PushX to promote your post about PushX and compete for the top spot. 👀
Create your post. Spread the word. Make it count.
Good luck, everyone!
pushx.org/event/creator

Always Smile ♦️ retweeted
As we shared earlier, quantum computers cannot derive Bitcoin private keys today. But the computational resources required to make that possible are falling quickly.
In cryptography, "impossible" is not a law of nature. It is only a description of how much computation is required.
MemeBitcoin does not intend to leave this as a problem for the distant future. We are accelerating Crack participation so more of the community can take action now.
On September 29, a new Crack Event begins with a total reward pool of 1.096361 BTC.
Keep participating in Crack on MemeBitcoin as usual. You do not need to submit another BTC wallet address.
When the event begins, the Community Gauge will appear on the game screen. The Community Gauge does not decrease with every Crack. It decreases whenever an event winner is selected, reflecting the remaining reward amount.
Every Crack becomes part of a record built together by the community in the race toward 1,096,361 BTC.
If you receive the BTC Event Winner emblem, you have won. Your individual reward amount will be available when Claim opens. Each user can receive only one BTC Event Winner emblem.
The event ends when the remaining reward amount shown on the Community Gauge reaches zero. There is no fixed end date.
Detailed information about reward confirmation and the Claim process will be announced separately once everything is ready.
Crack.
Watch the remaining BTC fall.
Claim your share of 1.096361 BTC.
memebitcoin.org/
※ Notice: The MemeBitcoin Portal, originally scheduled to open on September 28, has been postponed while we prioritize the Crack Event. A new Portal launch date will be announced through our official channels.
Quantum computing still feels like science fiction to most people in crypto.
But the research is moving faster than many realize.
Earlier this year, Google Quantum AI published new research on Shor's algorithm and secp256k1, the elliptic curve used by Bitcoin.
Under the hardware and error rate assumptions used in the research, the estimated number of physical qubits required for this type of attack fell to roughly one-twentieth of previous estimates.
That does not mean a quantum computer can derive Bitcoin private keys today.
But it does mean that a future quantum computer capable of threatening Bitcoin cryptography may require significantly fewer resources than researchers previously estimated.
And the work is continuing. Researchers are still finding ways to make the algorithms and quantum circuits involved more efficient.
The progress in quantum computing appears to be moving faster than the conversation around it in crypto.
Most crypto users still see quantum risk as something far in the future.
Something to think about later.
But how far away is "later"?
Crypto has a Fear and Greed Index to measure how the market feels every day.
Maybe one day we will need a way to measure quantum risk too.
At MemeBitcoin, Crack has never been symbolic.
Every Crack generates a real candidate private key and checks whether it matches the target associated with Satoshi.
With today's computing, the probability of finding the correct key is effectively zero.
But "impossible" in cryptography is not a law of nature.
It is a statement about how much computation is required.
And that is exactly what advances in quantum computing are beginning to challenge.
For now, the mathematics still holds.
For now, those coins remain untouched.
For now.
An estimated 1,096,361 BTC, held in wallets widely associated with Satoshi, has remained untouched since Bitcoin's earliest days.
We have been cracking toward it, one key at a time.
Soon, there will be another reason to Crack.

I've just joined Early Access for @ComputersRh.
I'll be playing 24 hours before the public launch.
My ref link= computersrh.xyz/ref=duocmx
teapawt.net/computersrh/status/210…

Early Access applications are now open. 🏝️
🔗 computersrh.xyz/
Fill out the form to get access to ComputersRh 24 hours before the public launch.
You’ll also be able to create your own referral link and earn 5% of the in-game earnings of every player you invite.

Always Smile ♦️ retweeted
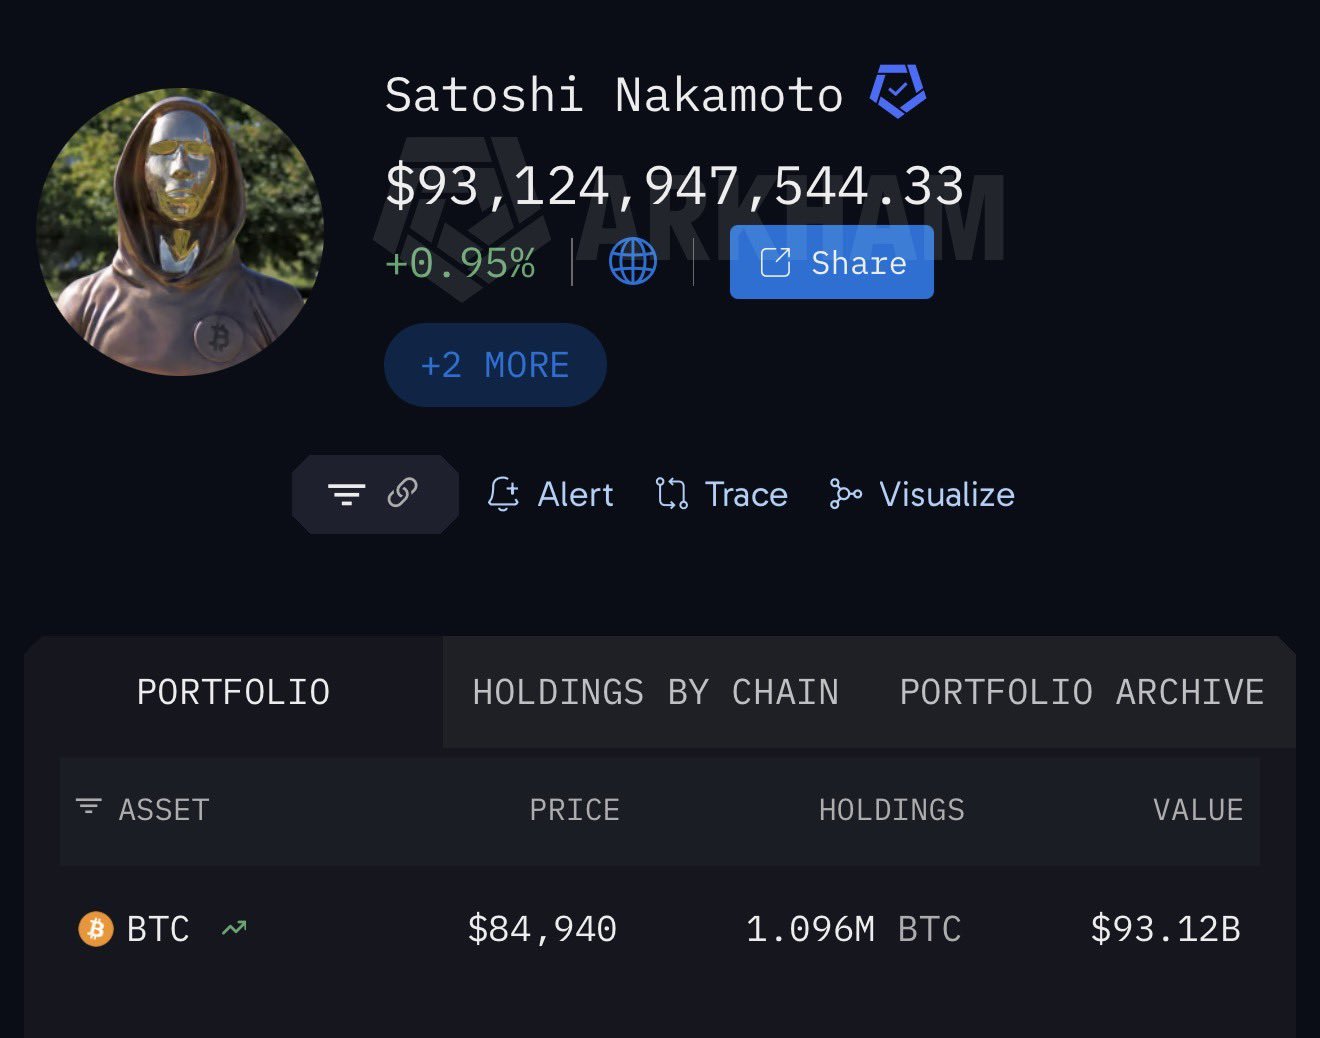
If you're curious about Satoshi's thoughts, try asking Satoshi AI.
memebitcoin.org/
The longer Satoshi remains silent, the more uncertainty and risk will continue to grow.
1,096,361


Always Smile ♦️ retweeted
Quantum computing still feels like science fiction to most people in crypto.
But the research is moving faster than many realize.
Earlier this year, Google Quantum AI published new research on Shor's algorithm and secp256k1, the elliptic curve used by Bitcoin.
Under the hardware and error rate assumptions used in the research, the estimated number of physical qubits required for this type of attack fell to roughly one-twentieth of previous estimates.
That does not mean a quantum computer can derive Bitcoin private keys today.
But it does mean that a future quantum computer capable of threatening Bitcoin cryptography may require significantly fewer resources than researchers previously estimated.
And the work is continuing. Researchers are still finding ways to make the algorithms and quantum circuits involved more efficient.
The progress in quantum computing appears to be moving faster than the conversation around it in crypto.
Most crypto users still see quantum risk as something far in the future.
Something to think about later.
But how far away is "later"?
Crypto has a Fear and Greed Index to measure how the market feels every day.
Maybe one day we will need a way to measure quantum risk too.
At MemeBitcoin, Crack has never been symbolic.
Every Crack generates a real candidate private key and checks whether it matches the target associated with Satoshi.
With today's computing, the probability of finding the correct key is effectively zero.
But "impossible" in cryptography is not a law of nature.
It is a statement about how much computation is required.
And that is exactly what advances in quantum computing are beginning to challenge.
For now, the mathematics still holds.
For now, those coins remain untouched.
For now.
An estimated 1,096,361 BTC, held in wallets widely associated with Satoshi, has remained untouched since Bitcoin's earliest days.
We have been cracking toward it, one key at a time.
Soon, there will be another reason to Crack.
After Google Quantum AI claimed in March 2026 that it had found a much more efficient quantum circuit for breaking Bitcoin and Ethereum signatures, the community on Eigen Labs' Open Autoresearch project, ECDSA.fail, has now built circuits that use 62% fewer resources than Google's unpublished result.
This is no longer a distant possibility. It is a threat moving into view. The crypto ecosystem needs to pay much closer attention to this issue.
ecdsa.fail/

Orbinum × SubWallet
🔐 Orbinum × SubWallet - now supported.
Huge thanks to @subwalletapp for shipping deterministic sr25519 signing. That's what unlocks it: the shielded pool now works straight from SubWallet.
Shield, transfer, unshield - in the wallet you already use.
🔹 Get / Update SubWallet extension to v1.3.90 → subwallet.app
🔹 Free ORB from the faucet → faucet.orbinum.network
🔹 Try it → app.orbinum.network/wallet/s…
⚠️ Browser extension only for now.
#Orbinum #SubWallet #Substrate #ZK #Privacy #Web3 #Wallet

Always Smile ♦️ retweeted
TRADE YOUR WAY TO A TESLA.
We said something big was coming. Here it is.
We’re launching the TrendBTC Trading Tournament — with a TESLA MODEL 3 waiting for the winner.
Everyone who registers for the tournament receives $1,000 in trading balance.
Main sponsor: PushX.org
Your net PnL decides who gets the keys.
🥇 1st — Tesla Model 3
🥈 2nd — $5,000
🥉 3rd — $3,000
Rewards go all the way to 100th place:
▸ 4–30: 3,000 $TREND + 1,000 PushX points each
▸ 31–50: 2,000 $TREND + 500 PushX points each
▸ 51–100: 1,000 $TREND + 300 PushX points each
HOW TO JOIN
1. Sign in to TrendBTC and open the Tournament tab.
2. Follow your personal PushX invitation and complete registration. Get your $1,000 trading balance.
3. Open Crypto. Choose a token, round duration and amount. Pick UP or DOWN — you’re competing.
Your tournament PnL starts at zero once your entry is confirmed. Profits move your score up, losses bring it down. Your net result determines your rank.
Completing signup also gets you 100 PushX points.
Your name at the top. Your hands on the wheel.
→ trendbtc.app

Always Smile ♦️ retweeted
This is content from Justin Drake’s remarks on quantum computing progress from almost four months ago.
The 1,096,361 problem is approaching silently, it is not a distant-future problem, but a practical one.

Today a crazy quantum story just got wilder.
On March 31, the Google Quantum AI team published a landmark result on Shor's algorithm for elliptic curve cryptography. Technically, the paper was a bombshell: a dramatic 10x improvement over the state-of-the-art. As a stunt and wakeup call to the blockchain space, those optimisations were illustrated on secp256k1, the elliptic curve underlying Bitcoin and Ethereum signatures.
But perhaps the most striking part of the paper was sociological, not technical. Instead of following standard academic process, the optimisations were kept secret, hidden behind a zero-knowledge (ZK) proof. Google's accompanying blog post mentions they "engaged with the U.S. government". The ZK proof demonstrates the existence of algorithmic improvements without leaking details. Academic censorship with ZK, a historic first!
As a co-author of the Google paper I witnessed some of the context surrounding this censorship. To be honest, multiple aspects of that context don't sit well with me. As much as I believe the general public ought to know more, I am limited in my ability to whistleblow. Though let me be clear about one thing: the Google team's professionalism has been absolutely exemplary, and they deserve nothing but praise.
Censorship has a way of backfiring. The Streisand effect, where an attempt to bury something only draws more attention to it, is exactly what's unfolding today. First, Google's key optimisation has been rediscovered by the French. And in a thrilling turn of events, a collaborative Shor-at-home challenge just launched. The initiative, available at ecdsa[.]fail, breached a new Shor world record in a matter of hours.
Let's start with the rediscovery. Just two months after Google's paper, French quantum expert André Schrottenloher cracks the main secret optimisation. His paper, titled "Optimized Point Addition Circuits for Elliptic Curve Discrete Logarithms", landed on the arXiv today. Big congrats to André, who beat several other nerdsnipped experts to it. In a blog post also published today, Craig Gidney, the world expert on Shor optimisations, revealed that he'd been sitting on this very optimisation for a whole year under censorship pressure.
Interestingly, André missed a handful of minor optimisations, both from Google's original publication and from improvements found since. It's plausible there's still plenty of juice left to squeeze out of Shor, and this is exactly what the ecdsa[.]fail challenge is about. The verifier program developed for the ZK proof does double duty, automatically filtering for valid submissions. Dozens of compounding small and micro improvements are rolling in. As of the time of writing there's an 8.4% improvement to Google's circuit, as measured by the product of logical qubit count and Toffoli gate count. Nice!
The nerdsnipping ran deeper than anyone expected. Over the last few weeks it became clear it extended well beyond André and other quantum experts. Behind the scenes, a small army of amateurs quietly got to work. Inspired by Karpathy-style autoresearch, they turned AI on Shor. Ironically, the verifier program for the ZK proof makes an ideal reward function for AIs. The barrier to entry for this modern style of research is refreshingly low, with several non-experts, even a teenager, finding nice optimisations. Get in touch if you'd like to join a Telegram group with fellow autoresearchers :)
Part 2: neutral atoms and qday
The story doesn't end with Google. On the same day Google went public, a stealthy startup called Oratomic published its own Shor paper in a coordinated release. It made a splash, ultimately becoming the most upvoted paper on scirate[.]com, a website ranking arXiv papers.
Oratomic's claim was wild. By building on Google's logical optimisations and applying custom physical optimisations for neutral atoms, they claimed just 10K physical qubits were sufficient to run Shor's algorithm on secp256k1. That number is mind-bogglingly low.
Knowing essentially nothing about neutral atoms when Oratomic's paper landed, I was intrigued and decided to learn more about the tech. I fell straight down the rabbit hole and spent a couple hundred hours on the topic. I got a little obsessed and watched every YouTube video I could find and spoke to a bunch of experts.
My conclusion? The tech is real, very real. Even Google recently decided to start a neutral atom lab, a notable pivot from their sole focus on superconducting qubits. If you care about qday, i.e. the day a quantum computer will break the first piece of cryptography in production, neutral atoms demand your attention. I shared some of my learnings on Shor and neutral atoms in a 30min talk at the ZKProof cryptography conference. You can find it on YouTube by searching "zkproof neutral atom".
Here's an interesting observation about this duo of breakthrough papers: neither Google nor Oratomic say a word about what their results mean for qday. No timelines. Zero. Nada. That is especially baffling given that the whole point of whitehat quantum cryptanalysis is to inform qday estimations and help the general public make good decisions.
So let me attempt to partially fill the silence, similarly to what Scott Aaronson did in his April 29 post. Given everything I know, including scary non-public information, I now put the odds of qday by 2032 at 50%. 10% by 2030.
Anecdotally, the US government has its own date: 2035. Originating at the NSA and later adopted by NIST, it's when branches of the US government will be disallowed from using quantum-vulnerable cryptography. In plain language: with hindsight, that date is a joke and should be discounted entirely. I don't see how NIST avoids being forced to pull it forward by years.
Part 3: post-quantum cryptography
There are good reasons to sound the alarm today, but please do not panic. Rushing carelessly towards immature post-quantum cryptography is a recipe for disaster. IMO a good target date for migration is 2029, roughly 3.5 years out. 2029 happens to be the date selected by Google, Cloudflare, and the Ethereum Foundation.
These days most of my time goes to safely migrating Ethereum towards post-quantum cryptography as part of the broader lean Ethereum effort. There's a lot to do. We need to rip out and replace BLS signatures at the consensus layer, KZG commitments at the data layer, and ECDSA signatures at the execution layer.
The plan to get there is compelling, and is based on hash-based cryptography. Within the Ethereum Foundation we've developed a Swiss army knife called leanVM (github[.]com/leanEthereum/leanVM) powered by the magic of hash-based SNARKs. Thanks to truly exceptional work by Emile, Thomas, and others, its performance is derisked. Regarding security, leanVM is a jewel, a minimal zkVM crafted for end-to-end formal verification and maximum security.
Want to help? There are two $1M initiatives. First, the Proximity Prize (proximityprize[.]org). Solve a long-standing mathematical conjecture in coding theory, improve hash-based SNARKs, and go home a millionaire. Second, the Poseidon Initiative (poseidon-initiative[.]info), offers $1M for breaking Poseidon, the SNARK-friendly hash function.
Always Smile ♦️ retweeted
Those selected as POV who have contributed to MBTC's vision will be permanently recorded in MBTC’s Proof-of-Viral. This record can be verified through a forum that will be publicly released at a later date.
Congratulations to the 2-Week Winners, and thank you for your continued participation.

Validator docs updated
🛡️ Validator docs updated.
We know many of you want to run a validator on Orbinum. The testnet has 32 validator slots, and we'll fill them gradually.
To be considered, your node must keep running:
🔹 Watchtower, for automatic updates
🔹 Orbinum Telemetry at verbosity 1
🔹 Hardware benchmarks, reported on startup
We monitor uptime, sync status, and benchmarks through Telemetry, along with the hosting provider and region.
📡 View the full Orbinum node network: telemetry.orbinum.network/
📖 How slots are assigned:
docs.orbinum.network/validat…
#Orbinum #Testnet #Validators #ZK #Privacy #Substrate #Web3

Always Smile ♦️ retweeted
The autumn Pass is live: A Thousand Red Leaves 🍁
Three weeks. Five tiers. 720 $Sakura, 360k Petals, and Field, Moon and Storm Scrolls on the way to the top.
You don't need to grind anything new. Duels, yokai, tasks and daily check-ins all move you up the track.
Up to 600 points a day. Show up 17 of the 21 days and the Storm Scroll is yours.
The leaves are already falling.
sakurafields.com/app/season

Always Smile ♦️ retweeted

125,617 people are on the list.
Tomorrow it closes.
After that there's no way in. Not for your friends, not for anyone, until we open.
What you hold when it locks is what you keep: your number, your points, the people you brought.
One day left to add to any of them.
earnlist.app

Always Smile ♦️ retweeted
We will announce the Week 2 POV Emblem winners within the next 48 hours.
Thank you to everyone who continues to join and share POV.
Stay tuned for the results!