

Software security, cryptography, etc
Boston, MA
Joined August 2009
- Tweets1.1K
- Following1.1K
- Followers6.2K
- Likes4.8K





erbbysam ㋬ retweeted

I got second overall at the Google Bugswat in Singapore!! 🎉☺️
It was a talented group of almost 50 hackers so I am really proud of the findings and thankful to have been invited!


The hackers escaped containment! #bugSWAT


💥 bugSWAT is officially KICKING OFF at Escal8! 💥
We are bringing together Google's security engineers and some of the world's most talented external security researchers under one roof. The mission? Deep-dive into our architectures, hunt for vulnerabilities, and make Google products safer for everyone. 🔐🤝
The target is set. Let’s hunt! 🛠️🎯
#bugSWAT #ESCAL8 #GoogleVRP #BugBounty #GoogleSingapore #CyberSecurity
erbbysam ㋬ retweeted

All vendors should have a plan for rapid remediation in the case of active exploitation.
Here’s some emergency fix strategies we’ve seen over the years:
projectzero.google/2026/10/e…

erbbysam ㋬ retweeted

one of my engineers reached out to me about how they struggled to find satisfaction in their work in the age of AI. I asked them if I could publish our brief exchange, and they agreed. I know people are feeling similarly, so maybe they can relate. shubs.io/do-we-still-enjoy-s…
erbbysam ㋬ retweeted

It’s Thursday,
Not bounty thursday but close enough, here’s a live hacking vlog!
youtube.com/watch?v=tJhuAINZ…
TLDR : Google invited me to Seoul for one of the most unique bug bounty events I've ever attended.
I joined an invite-only group of security researchers attempting to find vulnerabilities in their flagship AI products. Together we spent several days trying to break Google's flagship AI products and uncover real impactful security vulnerabilities and attack chains.
In this vlog you'll follow the entire journey, from arriving in Seoul, meeting the other hackers, and what it actually feels like to not only hang out with, but also compete against some of the best google VRP researchers in the world.
🏆 Results:
• 2nd Place Overall (Most Valuable Hacker)
• Most Creative Report Award
• And Multiple valid bug bounty submissions.
If you're interested in AI security, bug bounty hunting, offensive security, or just curious what these invite-only hacking events look like behind the scenes, this one's for you.
Ft hackers like @rez0__ @Rhynorater @0xLupin @busf4ctor @valent1nee @svennergr and many more,

erbbysam ㋬ retweeted

RIP GitHub Actions Cache Poisoning. 🫡
github.blog/changelog/2026-0…
erbbysam ㋬ retweeted

"brutecat is super talented", "luckily I'm not oncall ;)", "incredible"
These are all real quotes from Googlers after seeing this blog post. Amazing work @brutecat, thank you for sharing!

Hacking Google with A.I. for $500,000
brutecat.com/r/hacking-googl…

erbbysam ㋬ retweeted
In April 2026, we held the latest edition of bugSWAT (our live event for security researchers) in Seoul, South Korea.
For more information on this edition's focus, its impact & winners, as well as bugSWAT in general, see 👇
bughunters.google.com/blog/b…

erbbysam ㋬ retweeted

For Google VRP, inject the full invalid reports guide as system context for your agent. It’s a cheap way to teach it what Google won’t reward, cutting false positives at the source.
bughunters.google.com/learn/…


I have been using Claude Code for bug bounty a lot and I see this pattern a lot in my workflow.
Me: Scan for vulnerabilities in this target
CC: This is interesting. I found 10 vulnerabilities. 2 Critical. 5 High. 1 Medium. 1 Low.
Me: I am interested in only Medium+
CC: Now we have 9 valid vulnerabilities.
Me: Reassess all 9 like an H1 triager
CC: Good suggestion. Let me do that. After reassessment I can see there are only 3 valid ones left. Most of them were by design.
Me: Reassess the pending valid ones with the assumption that the attacker is an external user and does not have access to internal systems.
CC: All the findings are invalid. Sorry about that, I should have analyzed it correctly. I will be careful from the next target onwards.
This happens every time 🤣🤣 and every time Claude Code's confidence level is 2000%.
I have been trying to add these instructions in CLAUDE.md but it seems to not care about them at all. 😅😅😅😅
Jokes aside, Claude Code is really good if you use it correctly.
I have already reported 2-3 reports fully found by Claude Code (using the above conversation workflow).
I am still working on getting a perfect workflow setup.
erbbysam ㋬ retweeted

I'm so happy to have won the MVH at the latest Google LHE (Seoul 2026). Thank you, @GoogleVRP, for the amazing event!


erbbysam ㋬ retweeted
📢 Open source security researchers, take note: we've updated the OSS VRP rules! We're emphasizing the need for actionable reports and verifiable reproduction steps – to allow us to focus on critical threats with real-world impact.
For more details 👇
bughunters.google.com/blog/o…
erbbysam ㋬ retweeted
Turning Almost Nothing into a Supply Chain Compromise of Angular with GitHub Actions Cache Poisoning
adnanthekhan.com/posts/angul…
#BugBounty

erbbysam ㋬ retweeted

Google VRP - Built different 💪
Full talk here:
youtu.be/t0-oXbczPLs
erbbysam ㋬ retweeted
People are now putting AI in their CI/CD deployment pipeline, making them vulnerable to a simple Prompt Injection.
My good friend @adnanthekhan managed to prove that @cline could have been backdoored like this 🤯
adnanthekhan.com/posts/cline…


erbbysam ㋬ retweeted
📢📢📢 Our Patch Rewards Program rules were updated to explicitly encourage batched submissions, and place every Google-filed OSS vulnerability explicitly into scope (thanks for your feedback).
Interested in getting rewarded for your awesome OSS security work? g.co/prp
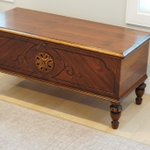
Finally done refinishing this 1935 chest that was covered in scratched lacquer and had a bit of water damage. Pretty happy with the results.


erbbysam ㋬ retweeted
I wrote a post that has a bunch of me and my friends arguing lolllll
do you think Prompt Injection is a bug?
josephthacker.com/ai/2025/11…

erbbysam ㋬ retweeted
I'm really excited to share my first research article related to hacking Google Gemini!
buganizer.cc/hacking-gemini-…
#bugSWAT #GoogleVRP