



flashfish retweeted

Many sophisticated MEV bot contracts use control flow obfuscation techniques to protect their logic. However, this also causes existing tools to struggle with analyzing obfuscated smart contracts, leaving critical vulnerabilities hidden.
Excited to share our solution: SKANF (1/n)

Interesting challenge. Even if you’re not looking for a job it’s useful for anyone wanting to improve their improve their on chain skills.


Worth saying that historically cvxCRV has had a worse peg than ycrv. Yes ycrv has less liquidity, but in reality a dca exit strategy of 3m exiting ycrv would probably net a better result that cvxCRV. I liked the rest of your thread though


My guess at how this was done.
Sandwichers submit their bundle to flashbots (or another builder) who build it into a block and send that block to a trusted relay.
The relay sends the block head to the validator for signing. Only after signing does the validator see inside

Dusk for sandwich bots? A few top mev bots were targetted in block
etherscan.io/txs?block=16964…
@peckshield @BlockSecTeam @bertcmiller @samczsun @bbbb
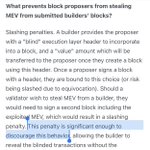
This is normally safe as there are slashing penalties if the validator validates a block with a different head. Due to having now signed two heads.
But what happens if it is worth paying the slashing cost for the opportunity to exploit the block? Maybe that’s what happened here
Looks like it was possible because of a bug with mevboost relay. It didn’t verify the validator signed the head correctly before revealing the internal block. So no double signing slashing and no risk of reorg

Block 16964664: A user managed to drain five MEV bots by exploiting a bug in mev-boost-relay.
Here's the block: etherscan.io/block/16964664
Here's the user: etherscan.io/address/0x3c98d…
Here's the patch: github.com/flashbots/mev-boo…
Here's the longer explanation:

flashfish retweeted

Block 16964664: A user managed to drain five MEV bots by exploiting a bug in mev-boost-relay.
Here's the block: etherscan.io/block/16964664
Here's the user: etherscan.io/address/0x3c98d…
Here's the patch: github.com/flashbots/mev-boo…
Here's the longer explanation:
flashfish retweeted

In a dazzling reverse hack, a substantial chunk of the Playtpus hack stolen funds have been recovered.
Here's how it worked: (1/4)

I think we could use these in normal defi while preserving transfer restrictions. Imagine a lending market where you could lend Ondo tokens and borrow any other. As long as the liquidators are whitelisted there is no risk of non-kyc users touching the Ondo tokens

Wow, just learned Balancer take a 50% fee on the rebase from liquid staked eth in their lps
forum.balancer.fi/t/bip-50-s…

flashfish retweeted

As a trader, there is barely a time that you can transparently share edge, but since FTX has gone down, it is clear that this strategy is never coming back, and I thought I would share insight on how i extracted round 5000% of value from the incompetency off SBF (1/x)