





Well, if any signature can reveal your private key, good luck getting any signed transaction on-chain without being frontrun and having your entire wallet drained before you can even perform your action and rotate your key.

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
> For users, actionable steps include:
> checking undocumented implementation details of your wallet
> understanding complex trade-offs
> applying advanced slippage limits
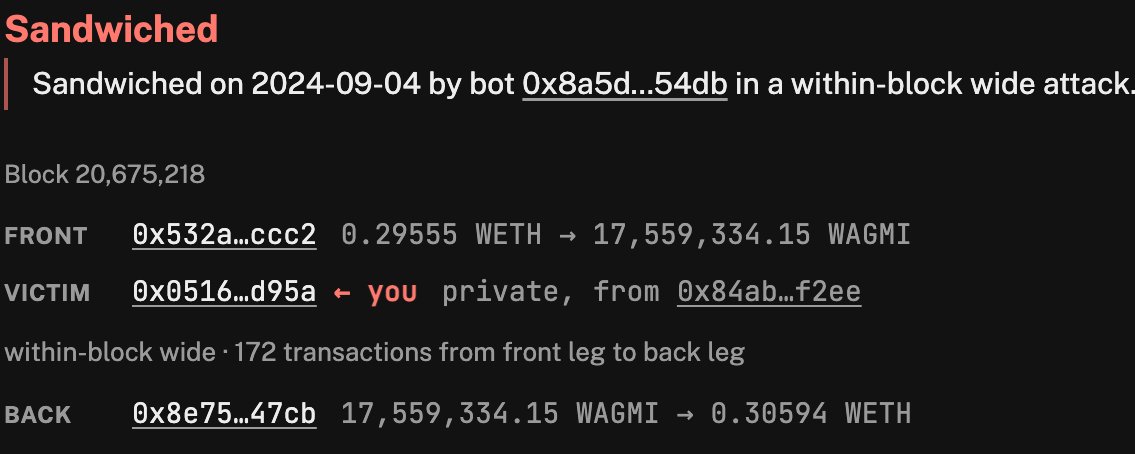
Or you can just use @CoWSwap where professional solvers bear the risk and cost of getting sandwiched.

Felix Leupold retweeted

For years, one of DeFi's best-kept secrets sat behind a locked door. 🔒
TWAP orders.
Advanced traders swore by them. Everyone else needed a Safe, a custom fallback handler, and an afternoon to spare.
Today, the door comes off its hinges. TWAP is open to every wallet.
🧵
One step closer to trustless cross-chain batch auctions.
@etheconomiczone & @CoWSwap will bring fragmented liquidity across stablecoins, RWAs, and beyond back together, without introducing a new validator set or trust assumptions...

We got an important step closer towards unified liquidity between L2s and Ethereum via @etheconomiczone.
Here is a @CoWSwap trade settled on L2 while using liquidity from L1. Bridging tokens out and receiving other tokens back all happens atomically!
Public testnet soon!

Felix Leupold retweeted

Defi legos at work: This morning Fractal settled an @aave debt swap through @CoWSwap using flashloans. The swap routed through 2 @titanbuilderxyz propamms (bopamm and fermiswap) etherscan.io/tx/0xb15f7a5275…

Felix Leupold retweeted

Here is the root cause of the current Gnosis Pay incident. Several other projects are affected. We tried to inform everyone privately in advance, but if you haven’t heard yet and are using a Zodiac module — Delay or Roles — please urgently check whether you are affected 👇

Community Notice: Zodiac Roles Modifier v2 and Delay Modifier v1.1.0 — Security Update
We identified a vulnerability in two Zodiac modules: Roles Modifier v2 and Delay Modifier v1.1.0. It affects only accounts where one of these modules is enabled AND a Safe account with a vulnerable fallback handler is itself assigned as a module or role member to the affected module.
Safe smart contracts, Safe{Wallet} infrastructure & UI are not affected.
Other Zodiac modules and setups are also not affected.
We've been working directly with affected users since identifying the issue. Over 95% of identifiable accounts have already resolved it.
If you have either module enabled and have not yet acted, check your account and follow the steps: app.zodiac.eco/public/fallba…
We apologize for the disruption and concern this incident has caused. Our team is working as quickly as we can to support affected users and help wherever possible.
A full post-mortem will follow.
If you have any questions, reach us at [email protected]
Felix Leupold retweeted
We’ll continue monitoring as Vercel’s investigation progresses.
We have no indication CoW Swap was among the impacted customers. However, we still completed all recommended remediation steps:
✅ Rotated all tokens
✅ Audited deployments -> no malicious code
✅ Reviewed activity logs -> no suspicious access
CoW Swap is safe to use.

We’ve identified a security incident that involved unauthorized access to certain internal Vercel systems, impacting a limited subset of customers. Please see our security bulletin:
vercel.com/kb/bulletin/verce…


Felix Leupold retweeted
UPDATE:
We now have full control of the cow.fi domain.
CoW Swap has been working as normal at cow.finance for some time now, and we are now working to transition it back to it's original domain.
In the meantime, here is an update on we know about the incident so far and what you should do if you were impacted. 👇🧵

The CoW Swap frontend is back up at swap.cow.finance.
Make sure you only sign approvals to 0xc92e8bdf79f0507f65a392b0ab4667716bfe0110 (the original GPv2VaultRelayer contract)


UPDATE: The swap dot cow dot fi domain is currently locked and not accessible. We are working with security experts to assert control over the domain while it is locked, but we *do not* expect it to be live again tonight.
For those who rely on CoW Swap daily, we have spun up a new instance of the CoW Swap UI at swap.cow.finance, which is safe to use.
Please continue to exercise extreme caution when interacting with any websites (including the new URL above) or social media accounts purporting to be CoW Swap. Only rely on official communications from this channel or on Discord surrounding the status of CoW Swap.
One man's “protection” is another man's “patronization”



Felix Leupold retweeted

CowSwap is now powering @aave.
Swap collateral or debt or repay with collateral, all in a seamless experience and best execution with MEV protection.


Few people seem to know that there is a @safe module allowing to guard transactions from being executed before a certain timestamp: github.com/schmanu/multisend…
H/t @schmanu_


It’s one of those mornings where you wake up, see there was a crash, and check how much extra $ you made from your @CoWSwap limit entry bids getting executed better than their limit price 🤌
Only place where a “limit order” can mean more than you asked for.
« You cannot create a backdoor that only lets the “good guys” in. »
Let alone tell who the good guys are these days.

We are alarmed by reports that Germany is on the verge of a catastrophic about-face, reversing its longstanding and principled opposition to the EU’s Chat Control proposal which, if passed, could spell the end of the right to privacy in Europe.
signal.org/blog/pdfs/germany…
It's to explain MEV protection in an intent based solver competition and the price advantages that not crossing the spread when settling a multi dimensional batch auction with uniform price clearing brings to the average crypto user in one word.

Great work by the whole team - from research through development to making a smooth transition in production!
@CoWSwap just got the biggest mechanism upgrade since inception and is now faster and fairer for all.
Probably the most ambitious project from @GnosisDAO yet. If money is just social coordination, why not use your actual social circle to create your own IOUs and use them as money.
Will probably take some more time for people to get, but imo a very interesting experiment...
