


SCAM Update: $SHRUB (Lil' Shrub, @lilshrub_RH - account now suspended) has rugged. It had a second backdoor that allowed the owner to transfer or burn tokens from any address. For example, in their final transaction, they transferred tokens out from the 0xdead address.
CA is: 0x5d9144d2d017386519a7134Fcc7f1E4bA22f920c. Don't interact!


SCAM warning: $SHRUB (Lil' Shrub, @lilshrub_RH) token on Robinhood has a honeypot switch that can be activated at any time and will block any attempt to sell the token for anyone except the owner! Get out while you can!
CA: 0x5d9144d2d017386519a7134Fcc7f1E4bA22f920c

2
287
SCAM warning: $SHRUB (Lil' Shrub, @lilshrub_RH) token on Robinhood has a honeypot switch that can be activated at any time and will block any attempt to sell the token for anyone except the owner! Get out while you can!
CA: 0x5d9144d2d017386519a7134Fcc7f1E4bA22f920c
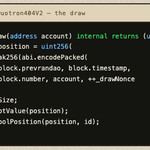
Hey @cruelhandeth, your draw mechanism in @Quotrons404 is really poorly-designed and let's people re-roll until they get the rarest NFT they want. This is a basic Web3 security issue:

1
1
55
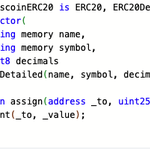
Turns out this June's @syscoin's exploit wasn't their first encounter with an infinite-mint vulnerability. Back in the days they had (a now deprecated) ETH mainnet token that had an unprotected function that just freely printed SYSX without onlyOwner() modifier. -> Evidence...


Preliminary Postmortem: Syscoin Bridge Incident
We want to provide the community with a preliminary update regarding the recent Syscoin bridge incident involving approximately 5B SYS.
The Syscoin bridge is currently paused while the team investigates, finalizes the fix, and works on rectifying the unauthorized SYS output created through the affected bridge path.
Summary
An attacker exploited a validation issue in the bridge flow that resulted in an unauthorized SYS output being created on the UTXO side.
The affected funds were moved and split after reaching the UTXO chain. We are actively tracing those funds and coordinating with exchanges and ecosystem partners to prevent the tainted outputs from being deposited, traded, or further distributed.
What happened
Based on our current investigation, the incident involved the bridge relay path incorrectly accepting or interpreting a transaction proof.
This caused the bridge system to treat the transaction as valid and create an unauthorized SYS output of approximately 5B SYS through the UTXO bridge path.
The funds were first sent to:
sys1qgaelv690g7wwp2xchfdh0enf5uewzq5sm9wvcw
They were then spent and split into additional outputs. The current large tainted balances appear to be associated with:
sys1q2k482wnachkgky4lw60973p4vcf7xlh9kzpv33 — approximately 4B SYS
sys1qx6jjkq89sdaxftfgre3m0nv7vjfd4jeakg5t38 — approximately 1B SYS
Relevant transactions
Initial UTXO transaction:
explorer-blockbook.syscoin.o…
Subsequent spend:
explorer-blockbook.syscoin.o…
Split transaction:
explorer-blockbook.syscoin.o…
Actions taken
- The bridge has been paused.
- We have contacted exchanges and relevant partners and asked them to blacklist, freeze, or closely monitor any SYS deposits connected to the tainted UTXO trail and all descendant spends.
- We are continuing to trace the affected funds and coordinate with infrastructure providers and ecosystem partners.
Remediation
The team has identified the affected validation path and has a fix in place.
Our priority now is to complete implementation and review of the fix, while also determining the correct process to rectify the unauthorized SYS output and neutralize its impact on the network.
We will provide further updates once the remediation path has been finalized.
User Guidance
Users should not interact with the bridge while it remains paused.
We understand the seriousness of this incident and are treating it as the highest priority. We will continue to share updates as the investigation and remediation progress.
1
46
Evidence that this wasn't just an internal test token: It was just to pay a grant, and had Uniswap pools (albeit low liquidity) that were drained in 2022: etherscan.io/tx/0xd39aa4b3da…

29
With all the recent hype around $FWA, an onchain gacha mechanism, let's look at other tokenized "pack ripping" sites and their onchain RNG mechanisms. Spoiler alert: They aren't all as "provably fair" as they claim. First up: @Collector_Crypt ->
1
1
151
Conclusion: Doing randomness fairly and safely on-chain is tricky (plenty of examples of poorly implemented RNGs that were exploited in the past), and claims of "provably fair" require documentation and reproduction tools that only few platforms provide.
1
20
Hey @yieldcore, this is a reminder that your "yieldcore-2nd-deal" vault at 0x98FFBD67fb84506c630a77b901ACeA78CC917470 is still vulnerable. Do not call matureVault() or return any principal until it is patched. DM us if you need help with an audit or tracing the exploiter.
2
71
Hey @yieldcore and @SuperApp_io users, that's you!

Exploit Alert: ycdeal3 / RWAVault unauthorized withdraw on Ethereum
Chain: Ethereum
Loss: ~387,763.999994 USDC
Target: ycdeal3 vault at 0xb9c7c84a1aa0dd40b5b38aae815ad0cdd2e5f88a
Attack Attack Tx:
etherscan.io/tx/0x6b04344d56… Summary: The attacker abused a missing check between receiver and owner in withdraw, then used victim owner addresses to redeem vault assets to attacker contract 0x50c140c2f705fa9d0bd0f4f253bacf4087588d17. Multiple unauthorized withdrawals drained about 387.76k USDC from the ycdeal3 vault flow.
Funds flow: 5,000 USDC was swapped on Uniswap V2 for 2.195959995966763304 ETH, and 387,763.999994 USDC was transferred to 0x7137804200a073f616d92e87007f1f100100b56a.
#DeFiSecurity #ETH #ExploitAlert

3
72