

Risk Management, Reasonable Security, Compliance, Pen Testing, Incident Response, Security Engineering, ISO 27001, CIS RAM, Duty of Care Risk Assessments DoCRA
Schaumburg, IL
Joined March 2008
- Tweets930
- Following185
- Followers558
- Likes1.2K
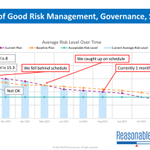





Over 30% of executives indicated they needed to improve their cybersecurity program they are disclosing or have not started working on their disclosures. The webcast recording and materials are now available.
halock.com/compliance-week-w…

ALT SEC cybersecurity reasonable risk
Wright & Filippis, specializing in prosthetics, orthopedics, proposed a settlement of $2.9 million in response to allegations that they inadequately safeguarded personal data. halock.com/orthopedic-and-pr…
#reasonable #security #DoCRA #settlement #data #breach #ransomware

BHI Energy, a Massachusetts-based US energy services firm issued a data breach notification on October 18 about a recent data breach and subsequent ransomware attack.
halock.com/us-energy-service…
#ransomware #risk #DoCRA #energy #breach #GRC

Compliance Week SEC Cybersecurity Rules and Risk. Tomorrow October 24th. halock.com/compliance-week-w…
#CPE #compliance #Risk #SEC #cybersecurity #DoCRA #dutyofcare #reasoanble

Making informed decisions for Risk Management.
halock.com/reasonablerisk
Learn how to establish reasonable security, project manage your risks efficiently, and communicate security priorities and investment needs to the C-Suite and executives effectively.
#reasonable #risk #GRC

Companies and their third parties are interconnected. If they get breached, so do you. halock.com/third-party-risk-…
#TPRM #thirdpartyrisk #reasonable #security #cyber #compliance #tpsp #panorays #threat #monitor #asset_discovery #tpsp #vendor

Define a “clear line of acceptable risk” and more at this complimentary webinar. CEO Jim Mirochnik presents best practices on risk management and how to effectively connect security teams and the C-Suite.
halock.com/complianceweek-we…
#reasonable #security #DoCRA #cyber #compliance

Happy 4th of July! Remember to Protect Your Assets. halock.com/wp-content/upload…
#password #cybersecurity #july4th #reasonable #DoCRA #reasonable #risk #GRC #dutyofcare #MFA #safeguards #privacy #hacker #breach #data #compliance #pentest

Tomorrow halock.com/pci-dss-2 In version 4.0, all periodic cadence requirements must be justified with a targeted risk analysis. Learn how to conduct a targeted risk analysis that use DoCRA, that litigators and regulators expect to see when doing risk assessments. #risk #TRA

Today PCI Requirements Webinar with Viviana Wesley halock.com/webinar-a-deep-di…
#pcicompliance #risk #pcidss

What a great educational and wonderful group of folks. Very insightful sessions on managing payments in one of the most unique industries. halock.com/the-payments-acad…
Viviana Wesley Justin Evans
#PCI #PCIDSS #PCIcompliance #card #sensitive #compliance #risk #TPA #payments #v4 #GRC

Today - PCI Webinar Series on Immediate Requirements. Speaker Viviana Wesley
halock.com/webinar-a-deep-di…
#PCI #PCIDSS4 #compliance #risk


In 1 Week: April 27, 2023 PCI DSS v3.2.1 expires on March 31, 2024. Organizations should now be planning their transition to PCI DSS v4.0. 64 new requirements in PCI DSS v4.0, there is a lot to consider in preparation for the coming deadline halock.com/preparing-for-you… #PCI_DSS

How far can the attacker go before being halted or contained by investments made into existing safeguards? halock.com/pen-test/penetrat… #assumed #breach #penetration_testing #controls #reasonable #DoCRA #cybersecurity #privacy #safeguards #vulnerability

Sensitive personal information must be protected from unauthorized access, use, disclosure, or destruction, and the law requires firms to take reasonable security measures to do so. eyeonannapolis.net/2023/04/d…
#reasonable #security #cyber #data #risk #DoCRA #PIPA

Viviana Wesley of HALOCK Security Labs and Justin Evans of the University of Iowa will present at The Payments Academy Annual Conference on May 7-10, 2023, in Indianapolis. halock.com/halock-presenting…

Weee! is a food delivery service headquartered in Fremont California. The company made an announcement on its website that it suffered a data breach in February of 2023 that compromised the information of customers halock.com/sensitive-data-co…

20/20 Eye Care Network, Inc. detected unusual network activity on January 11, 2021, involving their AWS cloud storage environment. halock.com/eye-care-provider…
#reasonable #security #DoCRA #healthcare #data #breach #privacy #GRC #risk
